 Back Unn.Ua
Ukrenergo warns of malware distribution disguised as outage schedules | УНН
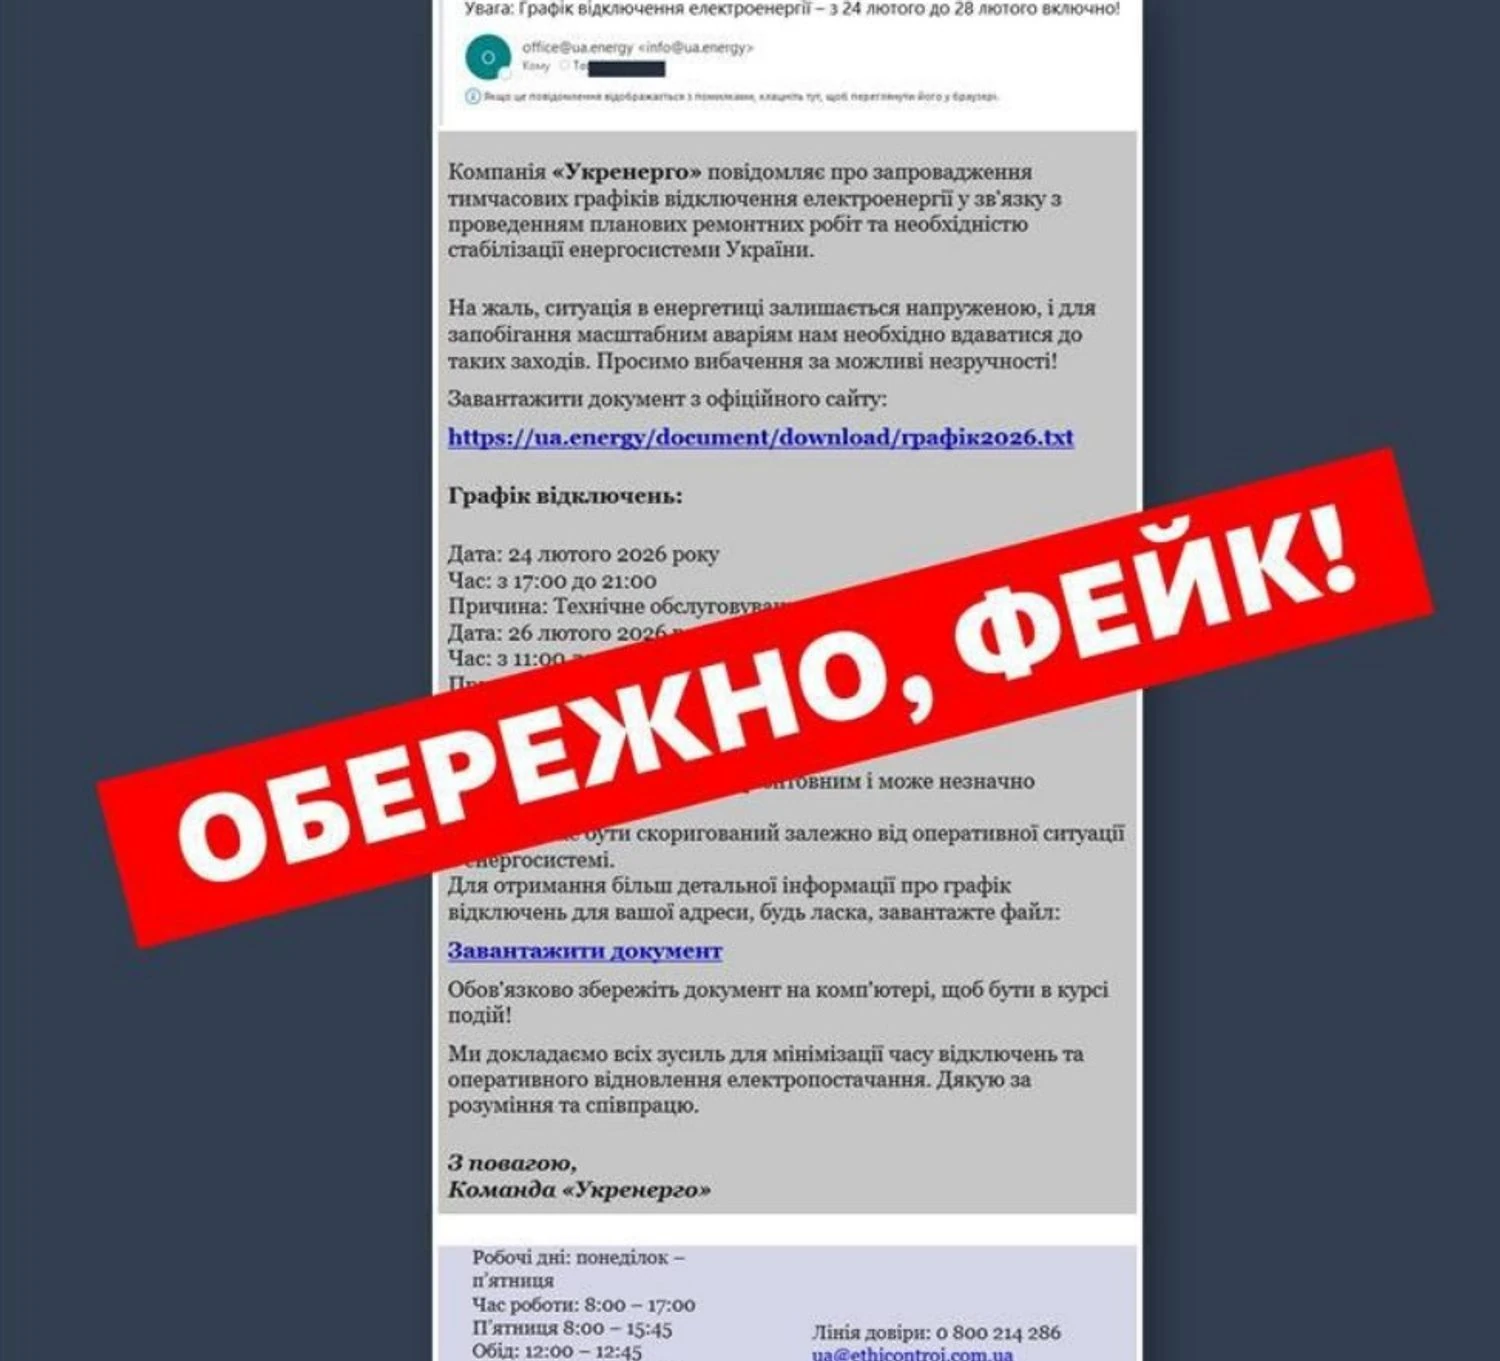
Ukrenergo has detected fraudulent emails containing viruses disguised as outage schedules. The company urges users not to open files and to check their devices with antivirus software.
The national energy company "Ukrenergo" has detected another wave of fraudulent activities aimed at stealing user data through emails. Attackers are sending messages with subjects like "Outage Schedule" or "Updated Restriction Schedule," which contain attached files with dangerous viruses. This is reported by UNN .
The emails come from a fake address, [email protected] , and fraudsters often include the company's real addresses in the CC field to lull the recipient into a false sense of security.
Hackers breached over 600 firewalls in 55 countries using AI in just a few weeks 21.02.26, 02:30 • 4962 views
Cybersecurity experts strongly recommend that if you receive such an email, do not download any files, do not click on links, and immediately delete the message. If a file was opened, it is urgent to check the device with antivirus software to prevent the spread of the threat.
Ukrenergo emphasizes that current information the energy system's status and restriction schedules is published exclusively on the company's official social media pages and on the websites of regional power distribution companies. Users are advised to trust only verified resources and avoid any downloads from unofficial mail. The energy company continues to monitor the situation and urges reporting new cases of phishing attacks for prompt response.
February 28, hourly power outages will continue throughout Ukraine - Ukrenergo 27.02.26, 20:14 • 1304 views
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
