 Back Ntd
US Government Agencies Warn Hackers Are Targeting Food and Medicine Refrigeration
The agencies urged grocery stores, cold storage operators, and related businesses to remove these controls from the public internet, citing the risk that cybercriminals could gain access and force freezers and coolers into defrost mode, potentially jeopardizing critical supplies.
“Every organization that depends on refrigeration and monitoring systems should assume it could be a target,” Chris Butera, acting executive assistant director for cybersecurity at the Cybersecurity and Infrastructure Security Agency (CISA), said in the agency’s release, urging them to “take action now to close known security gaps.”
CISA issued the warning with the FBI and the departments of Health and Human Services, Agriculture, and Transportation. The agencies said the targeted equipment is critical to industries such as health care, food production, agriculture, and chemical manufacturing.
“Industrial refrigeration and cold-chain monitoring systems protect food, medicine, and other temperature-sensitive products, making them attractive targets for malicious cyber actors,” FBI Cyber Branch Operations Director Brett Leatherman said.
“We are seeing these systems targeted across critical infrastructure sectors globally, putting inventory and equipment at risk,” Leatherman said.
Blood Service Facilities Targeted
"While this attack was unsuccessful due to the proper alert mechanisms in place, security weaknesses in unpatched or internet-accessible controllers can allow attackers to change system settings, potentially causing inventory loss and equipment damage," the FBI said.
The warning said more broadly that hackers can exploit internet-exposed controls or systems missing security updates.
Once inside, cybercriminals could raise temperatures and disable monitoring, preventing employees from detecting issues. The alert said the attack could destroy inventory, create fire hazards, or cause consumers to eat food kept at unsafe temperatures.
Businesses should take these steps to protect their refrigeration systems, according to the joint statement:
Remove control system devices and/or systems from the internet.
Change default passwords and strengthen passwords.
Apply patches and keep devices and systems updated.
Identify, retire, and replace legacy devices that the vendor no longer supports.
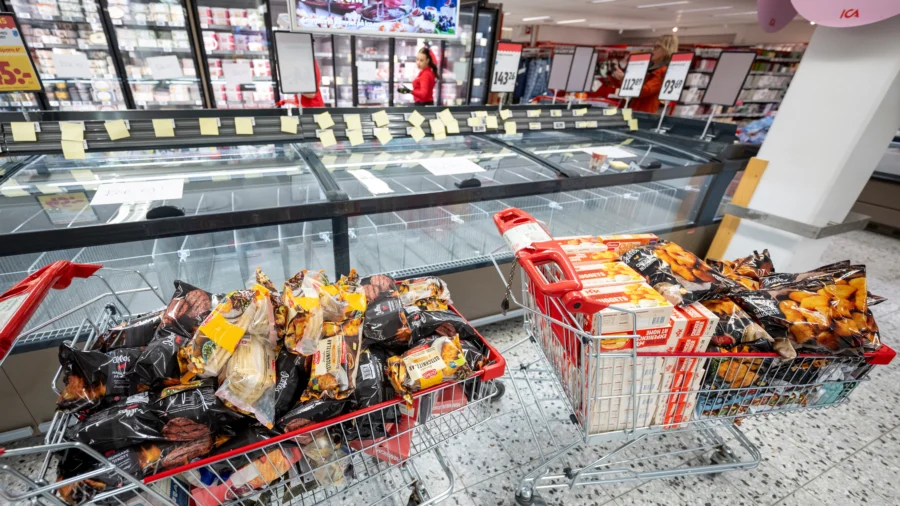
The U.S. warning came days after a new wave of attacks hit more than 100 stores across six European countries overnight Sunday into Monday.
France’s cyber response team reported in October that hackers had compromised refrigeration controls made by Danfoss, Copeland, and Dixell.
Ireland’s cybersecurity agency said Tuesday that attackers accessed controls exposed to the internet and urged businesses to check for changes to temperatures, defrost schedules, or alarms.
Leatherman said organizations should take the steps to protect their refrigeration systems and keep them running. He urged anyone who relies on those systems to follow the recommendations and report suspicious activity to the FBI.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
