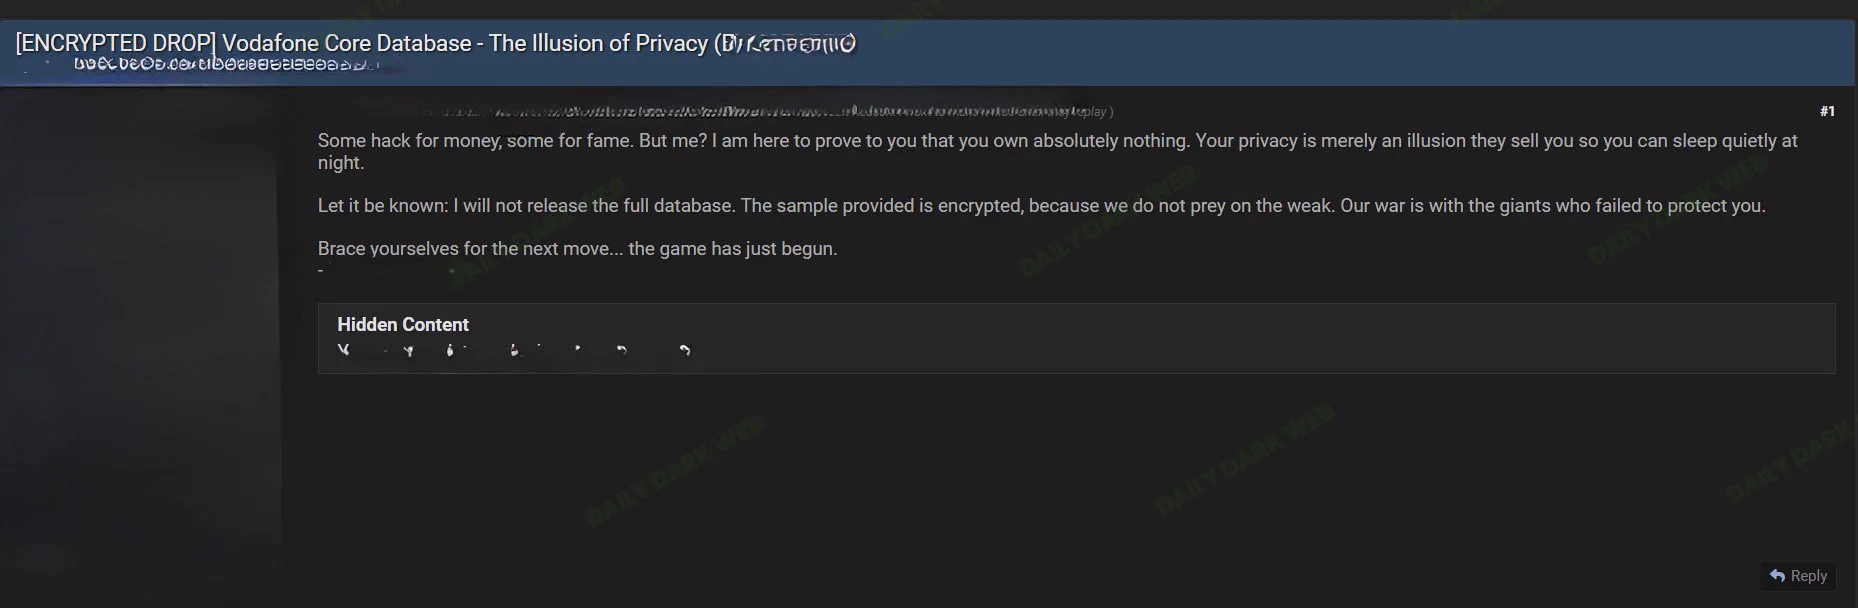
Dark Web Intelligence on X: "🚨 VODAFONE “CORE DATABASE” COMPROMISE CLAIM SURFACES ON DARK WEB
A threat actor has posted what they describe as an encrypted sample from a compromised Vodafone “core database.”
Unlike conventional leak posts, the actor says they do NOT currently intend to publicly release the full database and instead frames the incident as an operation targeting the company over alleged failures to protect customer privacy.
* Claims access to a Vodafone core database
* Provides an encrypted sample rather than readable records
* Does not disclose the number of affected records
* Does not identify what customer or network data was allegedly obtained
* Suggests additional activity or disclosures may follow
Until the encrypted material is independently validated or additional evidence emerges, this should be treated strictly as an unverified threat-actor claim.
#DDW #Vodafone #DarkWeb #ThreatIntelligence"
🚨 VODAFONE “CORE DATABASE” COMPROMISE CLAIM SURFACES ON DARK WEB
A threat actor has posted what they describe as an encrypted sample from a compromised Vodafone “core database.”
Unlike conventional leak posts, the actor says they do NOT currently intend to publicly release the full database and instead frames the incident as an operation targeting the company over alleged failures to protect customer privacy.
* Claims access to a Vodafone core database
* Provides an encrypted sample rather than readable records
* Does not disclose the number of affected records
* Does not identify what customer or network data was allegedly obtained
* Suggests additional activity or disclosures may follow
Until the encrypted material is independently validated or additional evidence emerges, this should be treated strictly as an unverified threat-actor claim.
Unverified sample claims need provenance and scope checks before they become incident narrative. Rotate anything that could be exposed; don't amplify the actor's timeline.
The full story
This article is one source in a clustered incident — the cluster page carries the summary, timeline and every other outlet covering it.
