 Theregister
'123456' Password Linked to Denmark Data Breach Affecting 8.8M People
Article Content

- •8.8 million individuals affected by the Denmark data breach.
- •Weakly protected accounts at a small IT company were exploited.
- •The commonly used password '123456' was linked to the breach.
A data breach in Denmark has reportedly compromised the personal information of 8.8 million individuals. The breach is linked to weakly protected accounts at a small IT company that had access to a national register. Local media reports indicate that the breach involved the use of the commonly used password '123456'. As a result, several IT systems remain offline, causing delays in orders for affected retailers. The incident highlights ongoing vulnerabilities in data security practices, particularly concerning password management. No specific CVEs or technical details were provided regarding the breach or the systems involved. The full scope of the breach and its implications are still being assessed.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Shai-hulud and Hobbs in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
How many people are affected by the breach?
What was the attack method used in this breach?
What is the current status of the affected systems?
Continue Reading
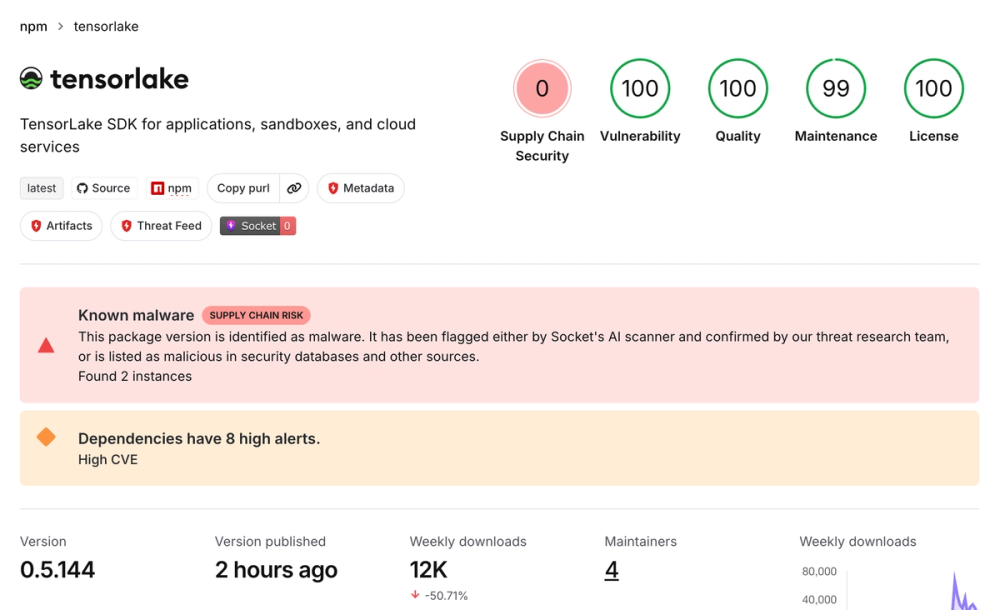 Tensorlake npm Package Compromised by Shai-Hulud Worm On October 8, 2026, the Tensorlake npm package version 0.5.144 was compromised, delivering a credential-stealing worm known as Shai-Hulud. The malware, which was published through a compromised maintainer account, executes a preinstall hook that runs an obfuscated loader to harvest credentials from local files and CI…
 Rise of Malicious npm Packages Threatens Developer Trust As of Q2 2026, Sonatype Research logged 1.8 million malicious packages, with npm accounting for 96.6% of this total. The quarter saw a surge in repository abuse, trojan-class malware, and maintainer compromises, indicating a shift towards targeting trusted developer workflows. ReversingLabs reported a specific…