 Securityaffairs.Co
340 Million OnlyFans User Records Allegedly Compromised in Data Leak
Article Content

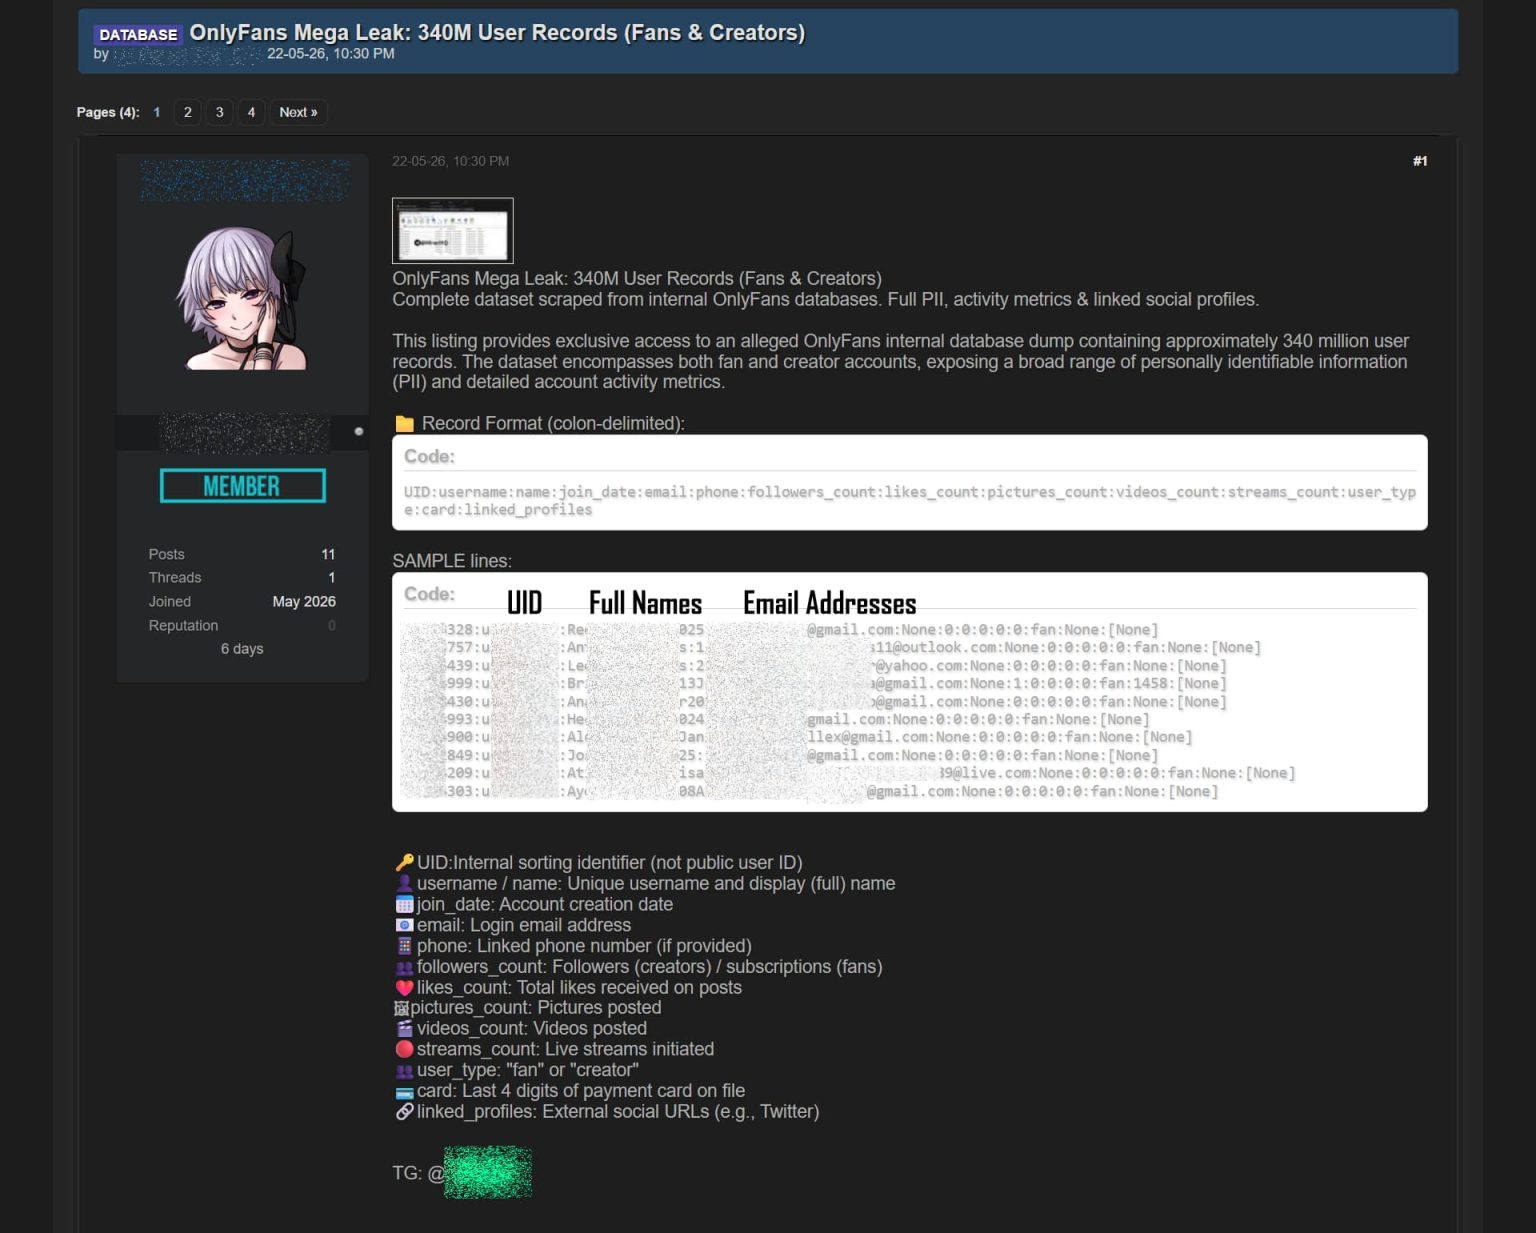
- •Hackers claim to sell 340 million OnlyFans user records, not directly hacked.
- •OnlyFans denies the data leak claims, stating reports are false.
- •Exposed data includes sensitive user information, raising phishing risks.
A hacker claims to be selling a dataset of 340 million OnlyFans user records, allegedly compiled from previous data breaches and public sources rather than a direct hack of OnlyFans. The dataset reportedly includes personally identifiable information and account activity metrics, which could expose users' identities. OnlyFans has denied the claims, stating that reports of a data leak are false. Initial investigations revealed a sample of 10 records, indicating that the data may be older, dating back to August 2025. The potential exposure of user emails could lead to phishing attacks, as threat actors might cross-reference this data with other breaches. The situation remains uncertain as OnlyFans has not confirmed any investigation into the claims.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track OnlyFans in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Massive Network of AI Proxy Servers Used for Malicious Activities Uncovered Security researchers from Team Cymru have identified over 10,000 proxy servers in China facilitating malicious AI activities. These servers, termed 'transfer stations,' are primarily used to bypass geographic restrictions and conduct model distillation attacks against frontier AI models. The infrastructure allows…
 Critical RCE Vulnerability in F5 BIG-IP APM Exploited in the Wild A severe heap-based buffer overflow vulnerability, tracked as CVE-2026-94127, has been identified in F5 BIG-IP Access Policy Manager (APM), allowing unauthenticated remote code execution (RCE) on the Traffic Management Microkernel (TMM) data plane. This vulnerability is triggered when both an APM access policy and an…