 www.interpol.int
95 Arrested in International CSAM Crackdown
Article Content

- •95 suspects arrested in a global CSAM operation.
- •Operation involved 17 countries and executed 127 warrants.
- •One child victim was rescued during the crackdown.
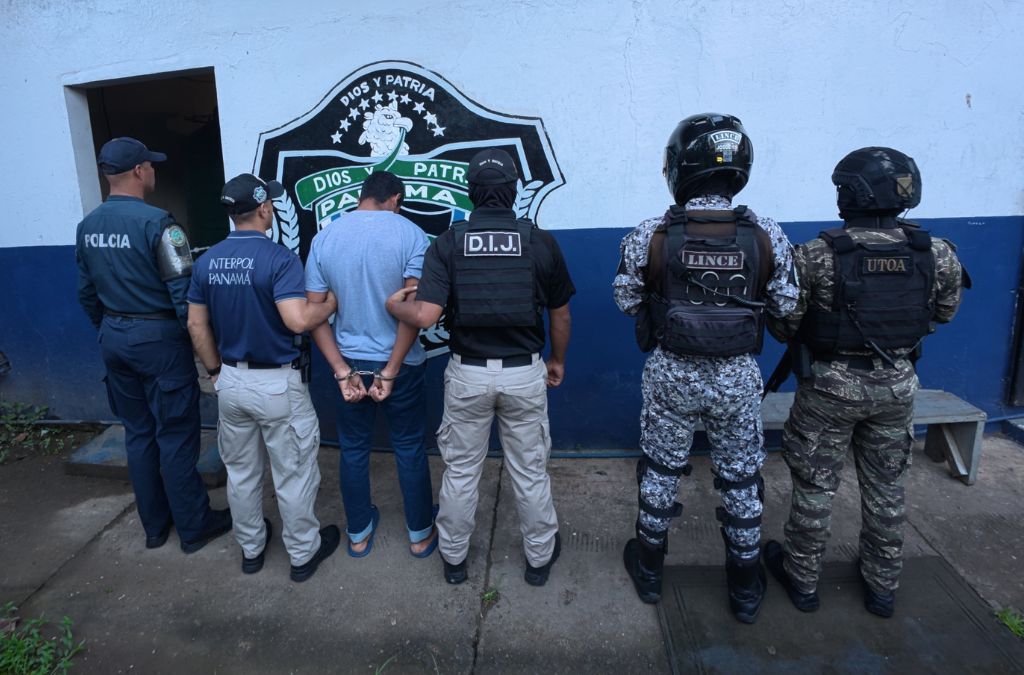
An INTERPOL-coordinated operation has led to the arrest of 95 suspects involved in the distribution of child sexual abuse material (CSAM) across 17 countries in Latin America and Europe. The operation, named International Effort Confluencia, spanned from March to September 2026 and involved executing 127 warrants. Authorities rescued one child victim during the crackdown. The arrested individuals were primarily male, with 89% of the suspects fitting this demographic. The operation revealed the increasing use of digital platforms for grooming children and monetizing abuse material. INTERPOL emphasized the urgent need for effective cross-border cooperation to combat these crimes. Material seized during the investigation is expected to help identify more offenders and at-risk children. This follows previous operations that have seen multiple arrests and the dismantling of significant CSAM platforms.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What is CSAM?
How many countries were involved?
What actions were taken during the operation?
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…