 Gadgetreview
Military GPS Jamming Linked to Fatal Medevac Crash in New Mexico
Article Content

- •Military GPS jamming was active during the medevac flight, contributing to the crash.
- •Four crew members died when the aircraft lost navigation and crashed into mountains.
- •The incident raises significant concerns about the safety of civilian flights in jamming zones.
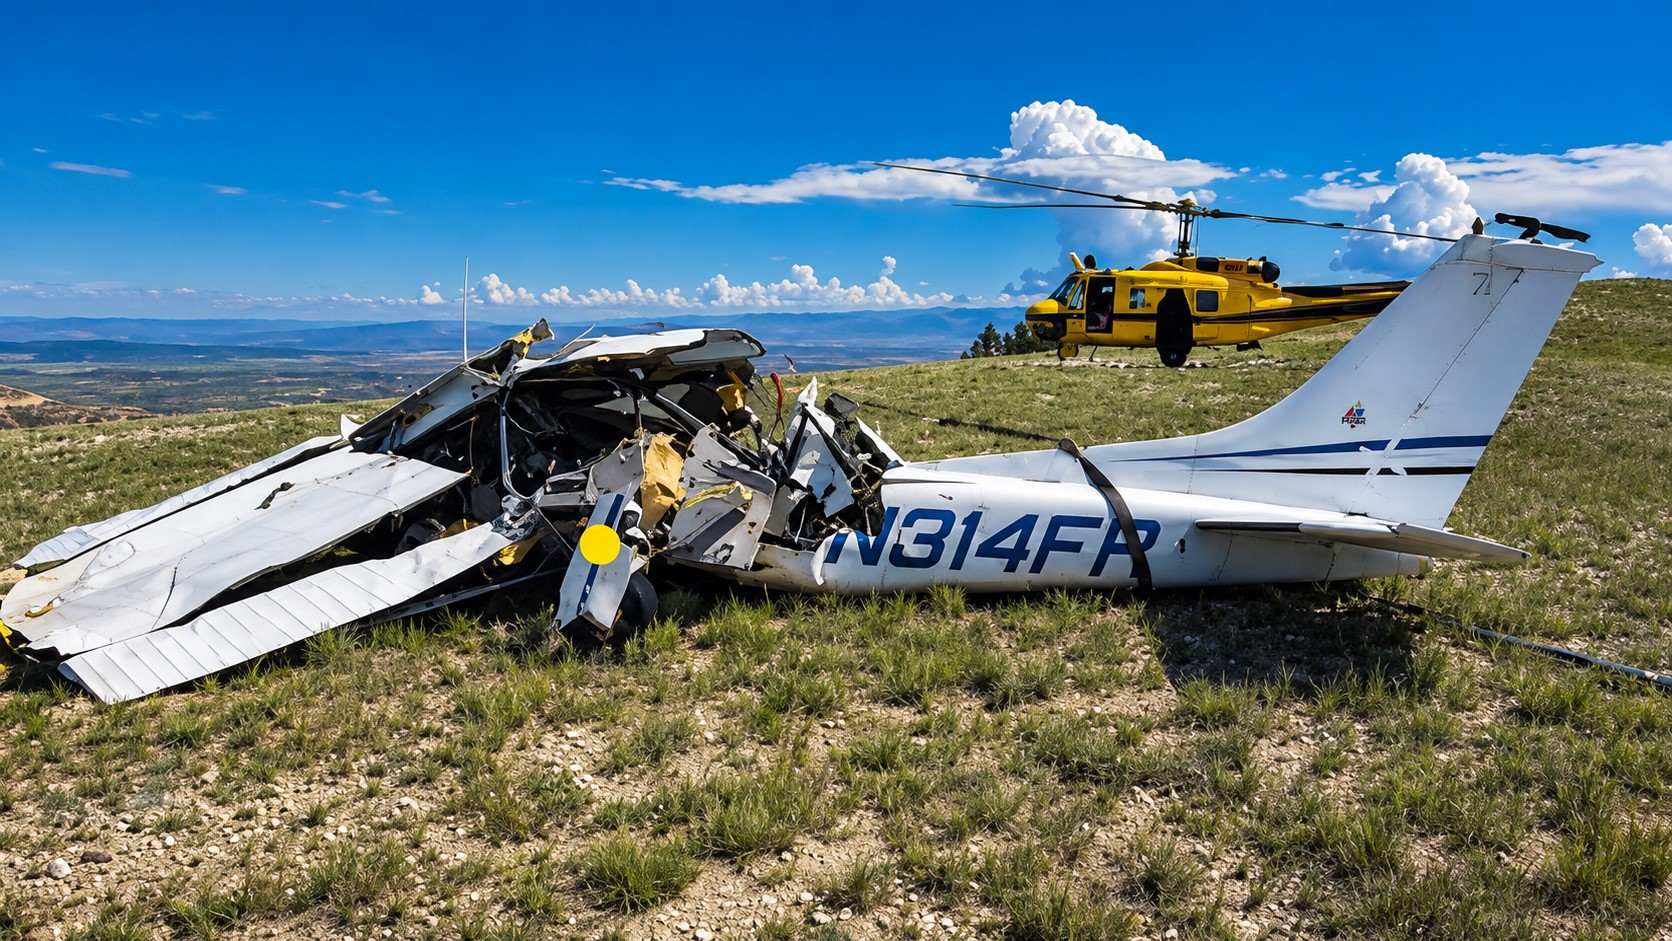
On May 14, 2026, a Beechcraft King Air C90 crashed in New Mexico, killing four crew members. The NTSB's preliminary report confirmed that military GPS jamming from White Sands Missile Range was active during the flight. The crew lost GPS navigation shortly after takeoff, leading to a disoriented descent into the Capitan Mountains. Air traffic control was overwhelmed by multiple aircraft affected by the same jamming, delaying assistance. The crash highlights vulnerabilities in civilian aviation due to military operations, raising concerns about the safety of GPS-dependent flights. The incident marks the first time military electronic warfare has been implicated in a fatal domestic aviation accident. The NTSB is investigating further to determine the probable cause.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Albuquerque Center in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…