 www.prnewswire.com
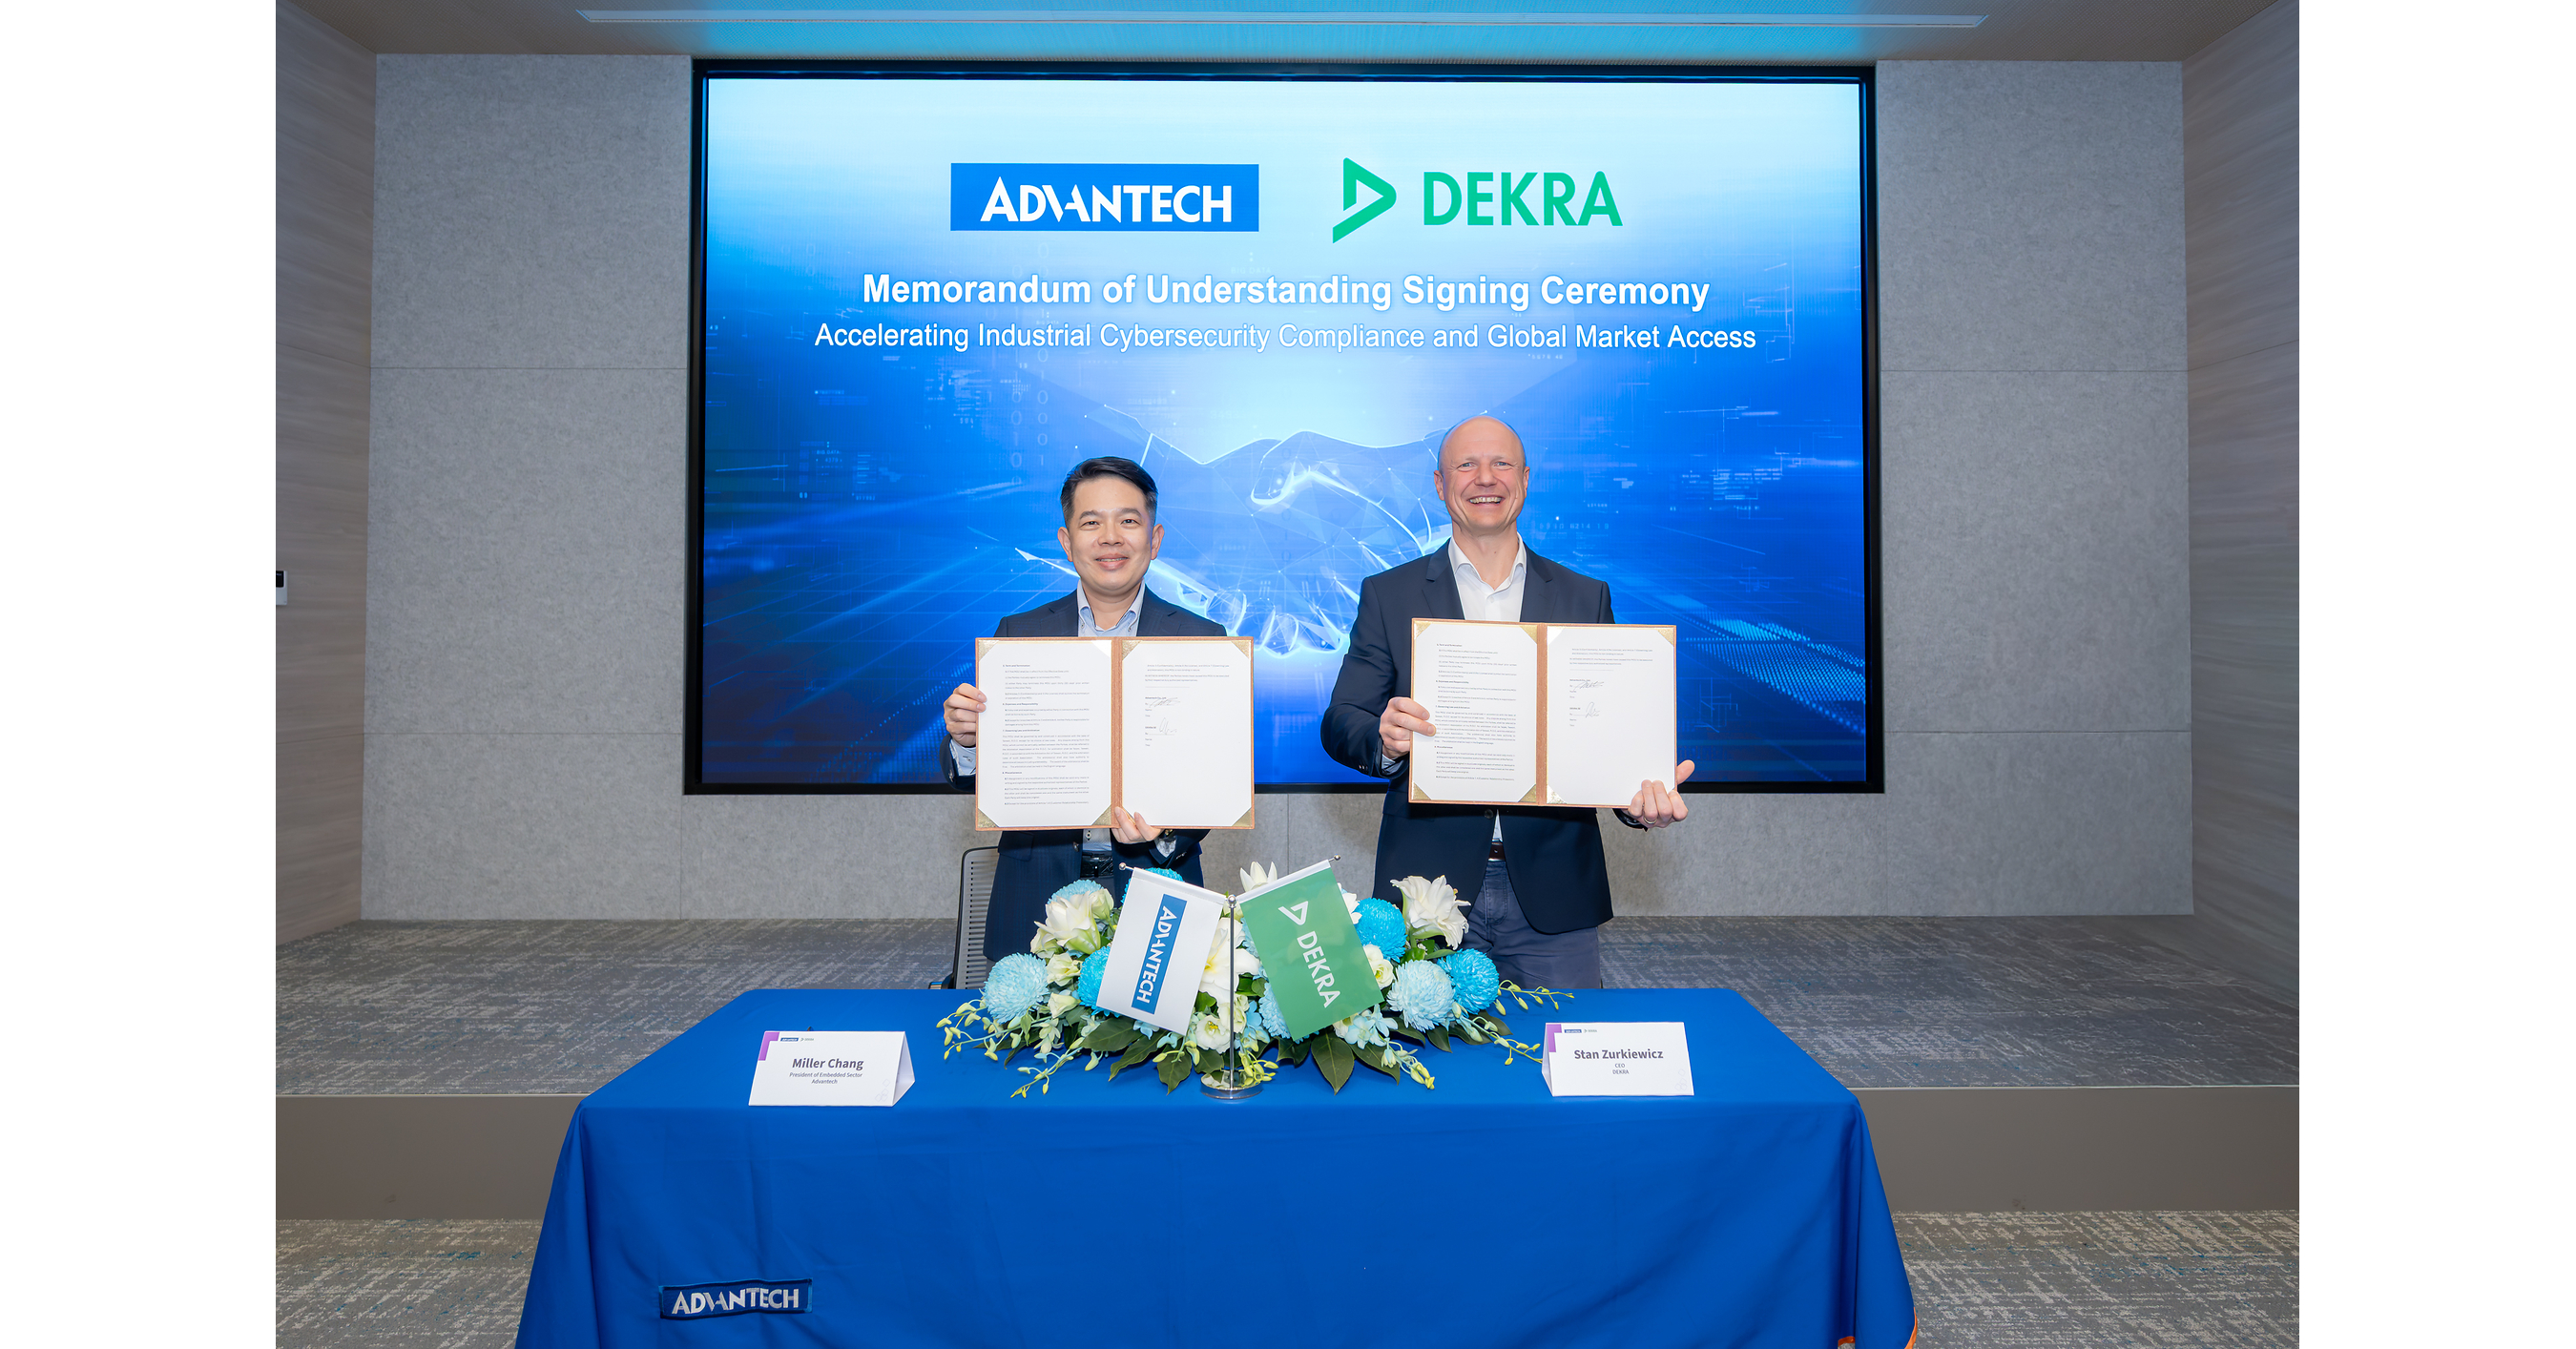
Advantech and DEKRA Collaborate on Cybersecurity Compliance for Edge AI
Article Content

- •Advantech and DEKRA's partnership focuses on cybersecurity compliance for Edge AI products.
- •The collaboration aims to integrate compliance from the product design phase to reduce risks and time-to-market.
- •Advantech's AFE-E630 has already achieved certification under IEC 62443-4-2 standards.
Advantech has signed a memorandum of understanding with DEKRA to enhance cybersecurity compliance for industrial equipment and Edge AI products in light of the EU Cyber Resilience Act (CRA). The partnership aims to integrate cybersecurity testing and certification into the product design phase, addressing compliance risks and reducing time-to-market for customers. Advantech's AFE-E630 industrial edge system has already received an IEC 62443-4-2 Certificate of Conformance, confirming its security functions meet relevant standards. This collaboration is essential as compliance requirements evolve from post-market certifications to prerequisites for market entry. The partnership will support various sectors, including robotics, drones, and energy, ensuring that customers can navigate regulatory requirements effectively.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Advantech in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the purpose of the Advantech and DEKRA partnership?
What certification has Advantech's AFE-E630 achieved?
How does this partnership affect product development timelines?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…