 www.reflectiz.com
AI Pentesting Checklist Highlights Vendor Gaps
Article Content

- •AI pentesting vendors may not perform well outside demo environments.
- •A critical vulnerability, CVE-2026-68982, was published on November 9, 2026.
- •A checklist with 15 questions is available to evaluate vendor capabilities.
On November 18, 2026, two articles discussed the importance of evaluating AI pentesting vendors for web applications. They emphasized that many vendors appear effective in demos but may fail to navigate real-world applications, particularly in login flows and vulnerability validation. The articles provided a checklist with 15 questions to assess vendor capabilities, including the ability to handle multi-factor authentication and validate exploitability. A notable CVE, CVE-2026-68982, was mentioned, which is a vulnerability with a CVSS score of 9.8, published on November 9, 2026. The articles stress the need for thorough testing and proof of findings to ensure production safety. Overall, the focus is on ensuring that AI pentesting tools deliver verifiable results in real-world scenarios.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track CVE-2026-68982 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What are the key checks for AI pentesting vendors?
How critical is CVE-2026-68982?
What should I look for in a pentesting vendor?
Continue Reading
 Of N-able Zero-Days for Crypto Mining A set of vulnerabilities in N-able N-central, tracked as 4EverAble2Shell, has been to deploy cryptocurrency miners on compromised servers. Attackers have successfully targeted 21 N-central servers across multiple countries, including the U.S., Canada, and several European nations. The vulnerabilities were disclosed on…
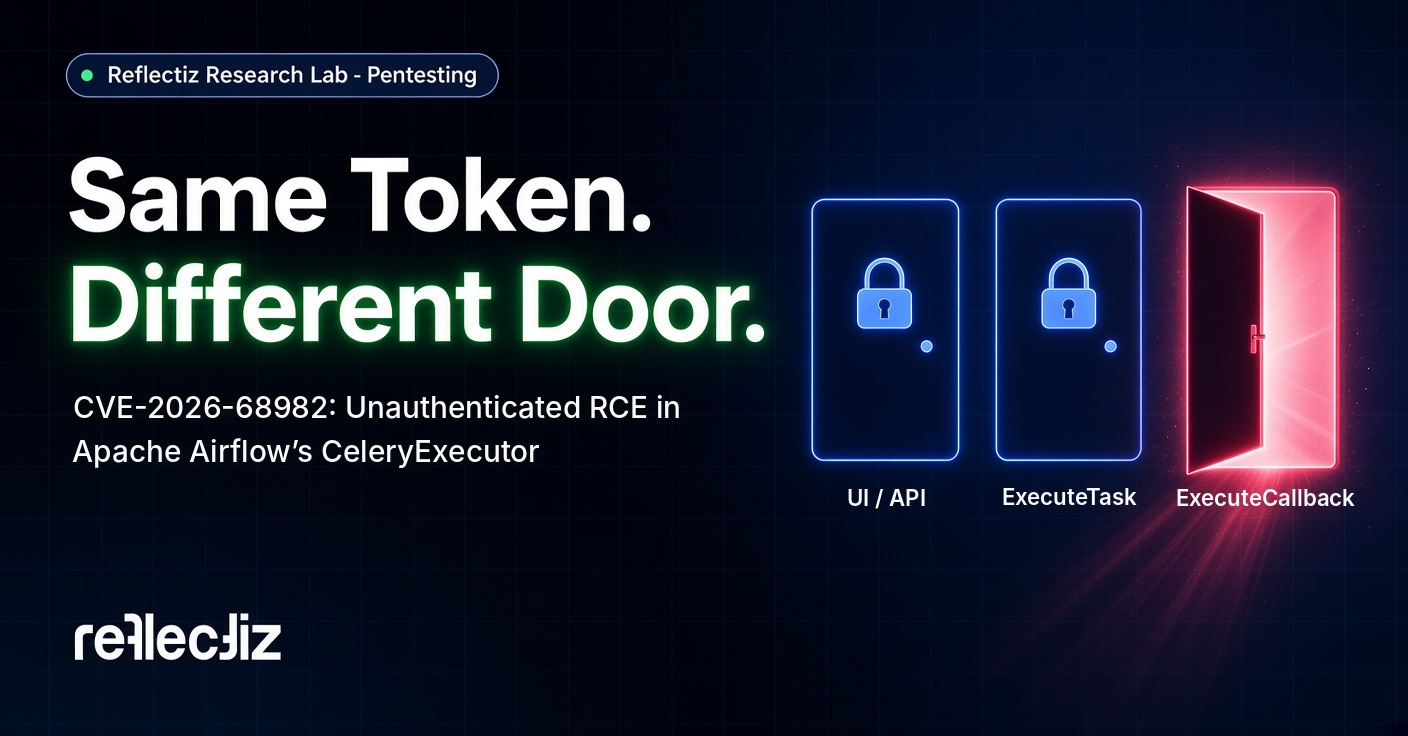 Critical Apache Airflow Flaw CVE-2026-68982 Enables Remote Code Execution A critical flaw in Apache Airflow, tracked as CVE-2026-68982, allows unauthenticated remote code execution on worker nodes through the CeleryExecutor. This vulnerability affects all Airflow versions prior to 3.4.0, enabling attackers with write access to the Celery broker to run arbitrary Python functions without…