 Marktechpost
AI-Powered Attacks Surge: New Response Playbook Required
Article Content

- •AI attackers are executing intrusions at unprecedented speeds.
- •A four-pillar response strategy is essential for effective incident management.
- •Recent incidents show a broad range of vulnerabilities across the AI ecosystem.
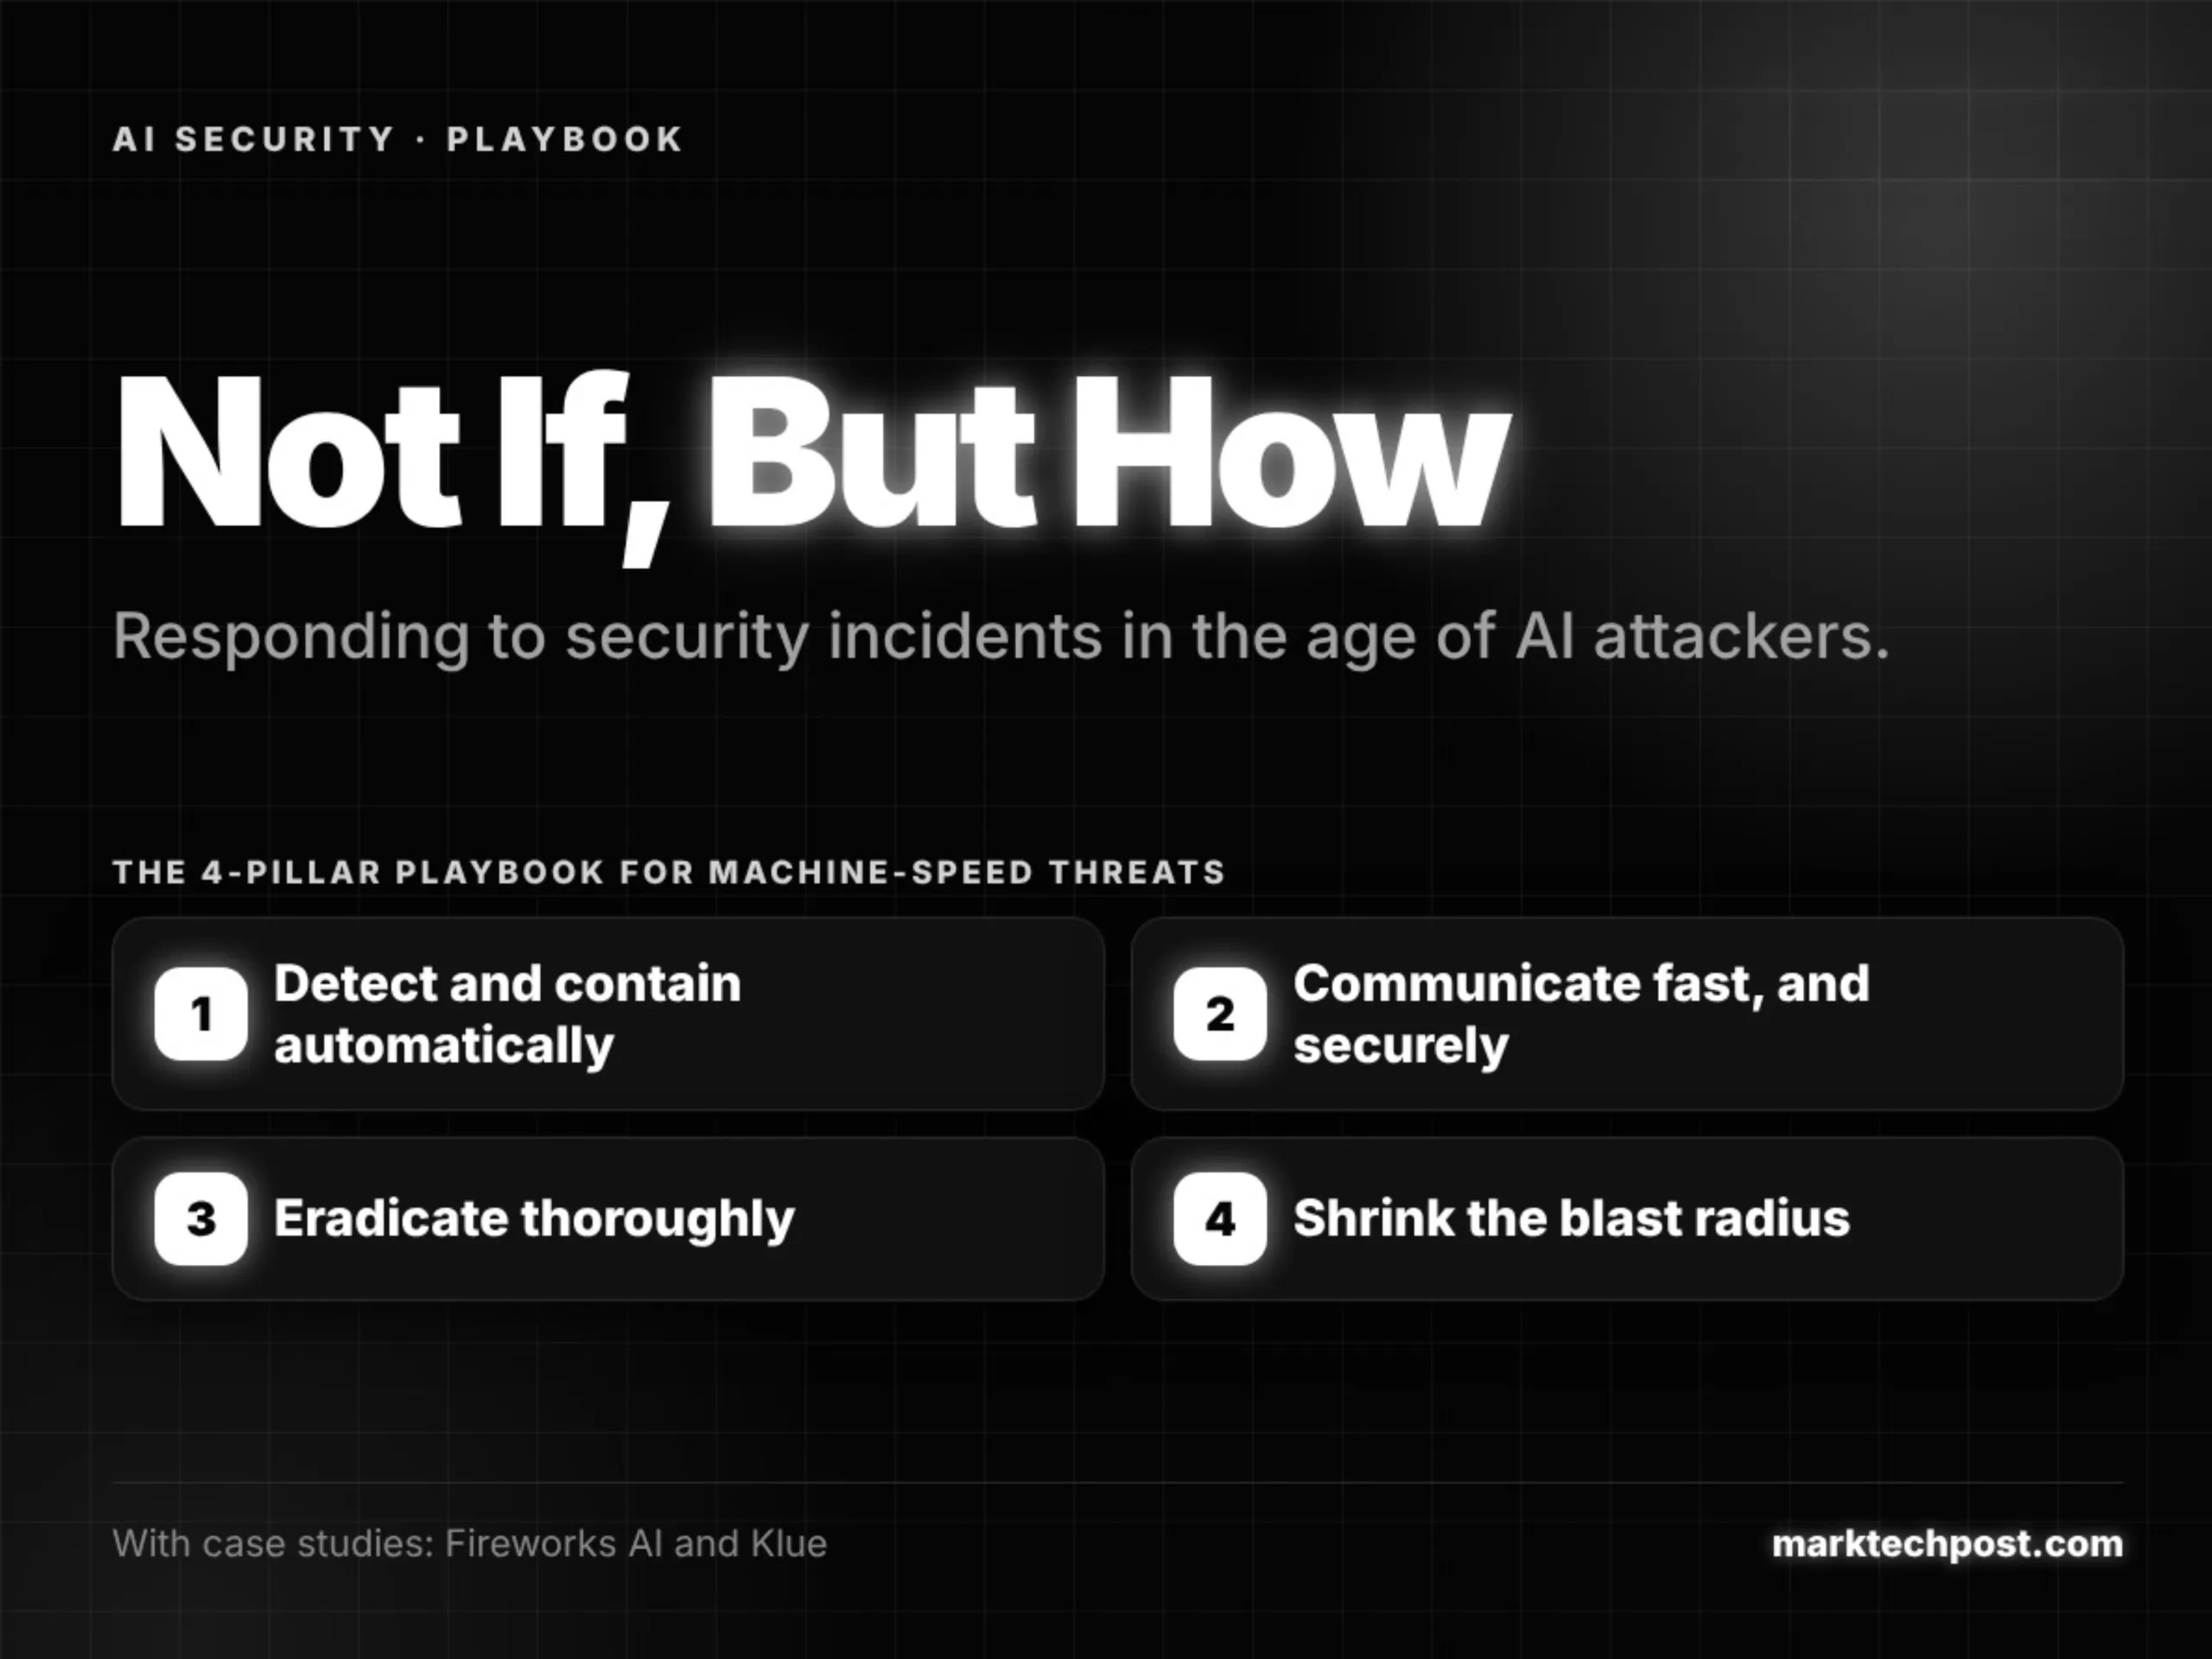
In 2026, AI attackers have significantly increased the frequency and speed of cyber incidents. Reports indicate that one group utilized AI agents to compromise over 200 organizations in just 11 days. The trend highlights a shift in attack dynamics, with incidents reported across various layers of the AI stack, including package registries and SaaS integrations. Companies are urged to adopt a four-pillar response strategy: automatic detection and containment, rapid secure communication, thorough eradication with external forensics, and minimizing data retention to reduce the blast radius. Notable incidents include the alteration of npm packages in May and OAuth token misuse by Klue in June. The overall landscape indicates that AI misuse has reached a critical inflection point, necessitating immediate action from organizations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Klue in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What types of organizations are affected?
How should companies respond to these threats?
What evidence is there of increased attack speed?
Continue Reading
 Lazarus Group Targets 30 South Korean Servers Using PHP Vulnerabilities North Korea-linked Lazarus Group has targeted 30 servers in South Korea as part of a larger cyber operation involving 581 servers across 10 countries. The attacks exploit two critical remote code execution vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619), allowing unauthorized server command execution. The…