 Asiae.Co.Kr
AI White-Hat Hacking Technology Gains Traction Amid Rising Cyber Threats
Article Content

- •AI white-hat hacking technology is becoming essential as cyber threats evolve.
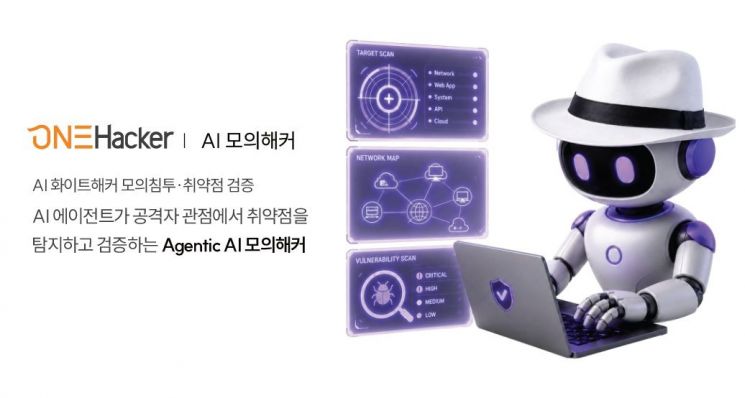
- •RaonSecure's OneHacker platform autonomously conducts penetration tests, outperforming human experts.
- •Concerns exist over the misuse of AI tools like ARTEX in unauthorized attacks.
As cyberattacks utilizing artificial intelligence (AI) become more advanced, AI white-hat hacking technology is emerging as a crucial defense mechanism. This technology continuously identifies system vulnerabilities and simulates attacks to validate security. South Korean company RaonSecure has launched OneHacker, an AI-driven penetration testing platform that autonomously devises and executes complex attack scenarios, significantly reducing testing time. However, concerns arise regarding the potential misuse of AI tools like ARTEX, which was initially developed for authorized testing but has been implicated in real-world attacks. RaonSecure emphasizes that its solutions focus on controlled environments and expert oversight to mitigate risks. The growing reliance on AI for both offensive and defensive cybersecurity strategies highlights the need for robust safeguards and continuous adaptation to evolving threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What is OneHacker?
What risks are associated with AI penetration tools?
How does AI improve penetration testing?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…