 Zawya
Al-Sager Discusses Cybersecurity and Resilience in Banking Sector
Article Content

- •Cybersecurity is a critical focus for the future of banking in Kuwait.
- •Resilience must be built before crises emerge, particularly in volatile geopolitical climates.
- •Sustainability and operational agility are essential for long-term financial stability.
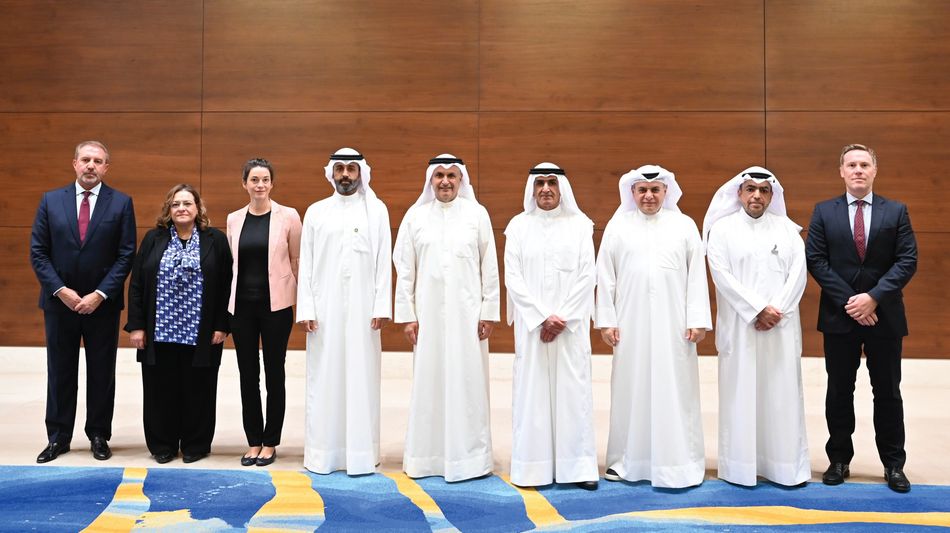
At the Kuwait Banking and Finance Roundtable, Isam Al-Sager, Vice Chairman of National Bank of Kuwait, emphasized the need for sustainability, operational resilience, and cybersecurity in the banking sector. He highlighted that resilience must be established before crises occur, particularly in light of geopolitical and economic volatility. Al-Sager noted that interconnected risks, including cyber threats, necessitate a comprehensive approach to risk management. He advocated for strong capital and liquidity, disciplined risk management, and operational agility to absorb shocks. The roundtable included discussions on the importance of integrating sustainability into financial practices and the role of banks in supporting economic growth. The event brought together key stakeholders, including the Central Bank of Kuwait and various bank CEOs, to address the challenges and structural shifts in the banking sector. Al-Sager called for enhanced cooperation among banks and regulators to strengthen institutional readiness.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (1)
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Citrix NetScaler Zero-Day Exploitation Confirmed Citrix has confirmed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, in its NetScaler ADC and Gateway products, both scoring 9.5 on the CVSS scale. These vulnerabilities are actively exploited in the wild, allowing unauthenticated attackers to execute arbitrary commands and potentially cause…