 En.Ilsole24Ore
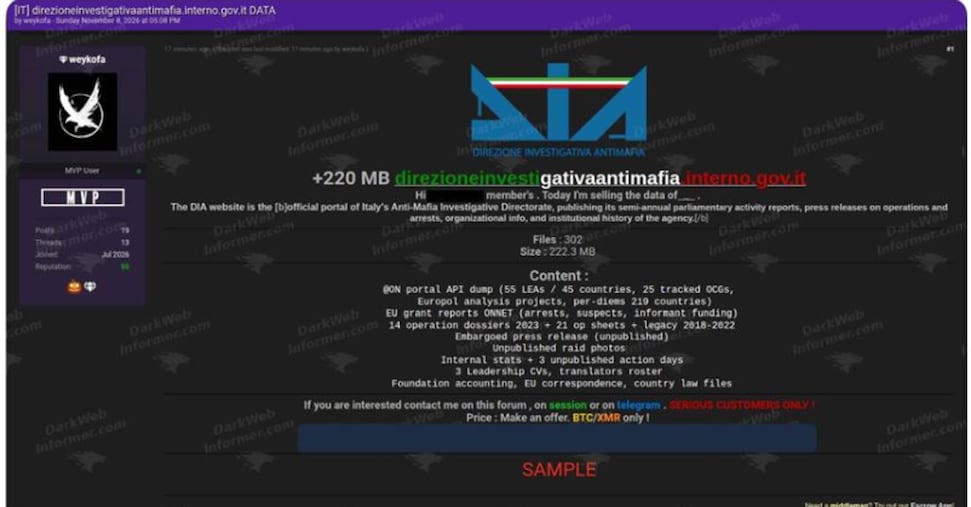
Alleged Anti-Mafia Files for Sale on Dark Web Following DIA Breach
Article Content

- •A seller claims to have stolen sensitive files from Italy's DIA.
- •The archive reportedly contains intelligence on 25 organized crime groups.
- •The authenticity of the breach and files remains unverified.
A seller named 'weykofa' claims to have stolen 302 files from Italy's Anti-Mafia Investigation Directorate (DIA), offering a 222 MB archive on the dark web. The files reportedly include sensitive intelligence on 25 organized crime groups, operational dossiers, and internal documents related to Europol. However, the authenticity of these claims remains unverified, as no official confirmation of the breach has been provided. The seller is accepting payments in Bitcoin and Monero, common cryptocurrencies in illicit transactions. The Dark Web Informer account first reported the sale on November 8, 2026, but emphasized the need for caution due to the potential for fraud in such listings. Without access to the files, independent verification of the claims is currently impossible.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Anti-Mafia Investigation Directorate in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What information is allegedly included in the stolen files?
Is there any confirmation of the breach?
How can I protect my organization from potential fallout?
Continue Reading
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…
 GitLab Issues Emergency Patch for Critical RCE Vulnerability GitLab has released emergency patches for a critical remote code execution vulnerability, CVE-2026-97229, affecting its Community and Enterprise Editions. This flaw, stemming from an integer overflow in the CI/CD regular expression compiler, allows unauthenticated attackers to execute arbitrary code via specially…