 Awazthevoice.In
Amit Shah Initiates Upgrade of Cyber Crime Helpline 1930 with AI Integration
Article Content

- •A national call centre for Cyber Crime Helpline 1930 will be established to handle unresolved complaints.
- •AI technology will be integrated to enhance complaint logging and call routing efficiency.
- •The initiative aims to improve the response to cyber financial fraud and ensure timely assistance to victims.
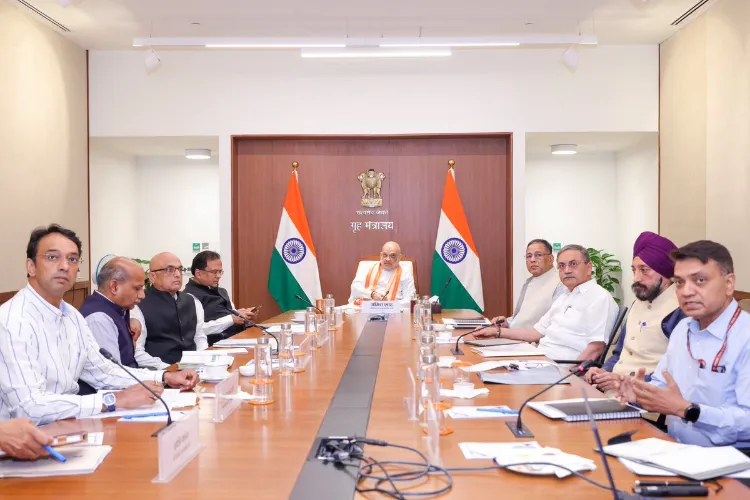
On June 17, 2026, Union Minister Amit Shah announced a national-level call centre to enhance the Cyber Crime Helpline 1930. This initiative aims to address unattended complaints from state-level centres, ensuring timely assistance for victims of cybercrime. The upgrade will incorporate advanced technologies, particularly artificial intelligence, for improved call routing and complaint management. Shah emphasized a zero-pendency approach, mandating that every citizen's call for help must be answered. The Ministry of Affairs will support the necessary technological enhancements, while states are expected to bolster staffing. The initiative also includes a review of the Citizen Financial Cyber Fraud Reporting and Management System (CFCFRMS), aimed at swiftly blocking fraudulent transactions. A Standard Operating Procedure (SOP) introduced in January 2026 will facilitate coordinated actions among banks and law enforcement to expedite the resolution of financial fraud cases.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…