Article Content
Browse articles 
Between July 2024 and February 2025, six suspicious DNG image files were uploaded to VirusTotal, targeting the Quram library used in Samsung devices. The investigation was initiated by a lead from Meta and conducted by the Google Threat Intelligence Group. On November 7, 2025, Unit 42 published a blog post detailing these exploits.
Ask AI about this cluster
Answers cite the sources they use
Updated 218d ago How this analysis works
More articles in this cluster (1)
Continue Reading
 Apple Patches CoreGraphics Zero-Day Exploited in Targeted Attacks Apple has released emergency updates for iOS, iPadOS, and macOS to address a critical zero-day vulnerability, CVE-2026-86950, in its CoreGraphics framework. This out-of-bounds write flaw can allow arbitrary code execution when a device processes a maliciously crafted file. The vulnerability was reportedly exploited in…
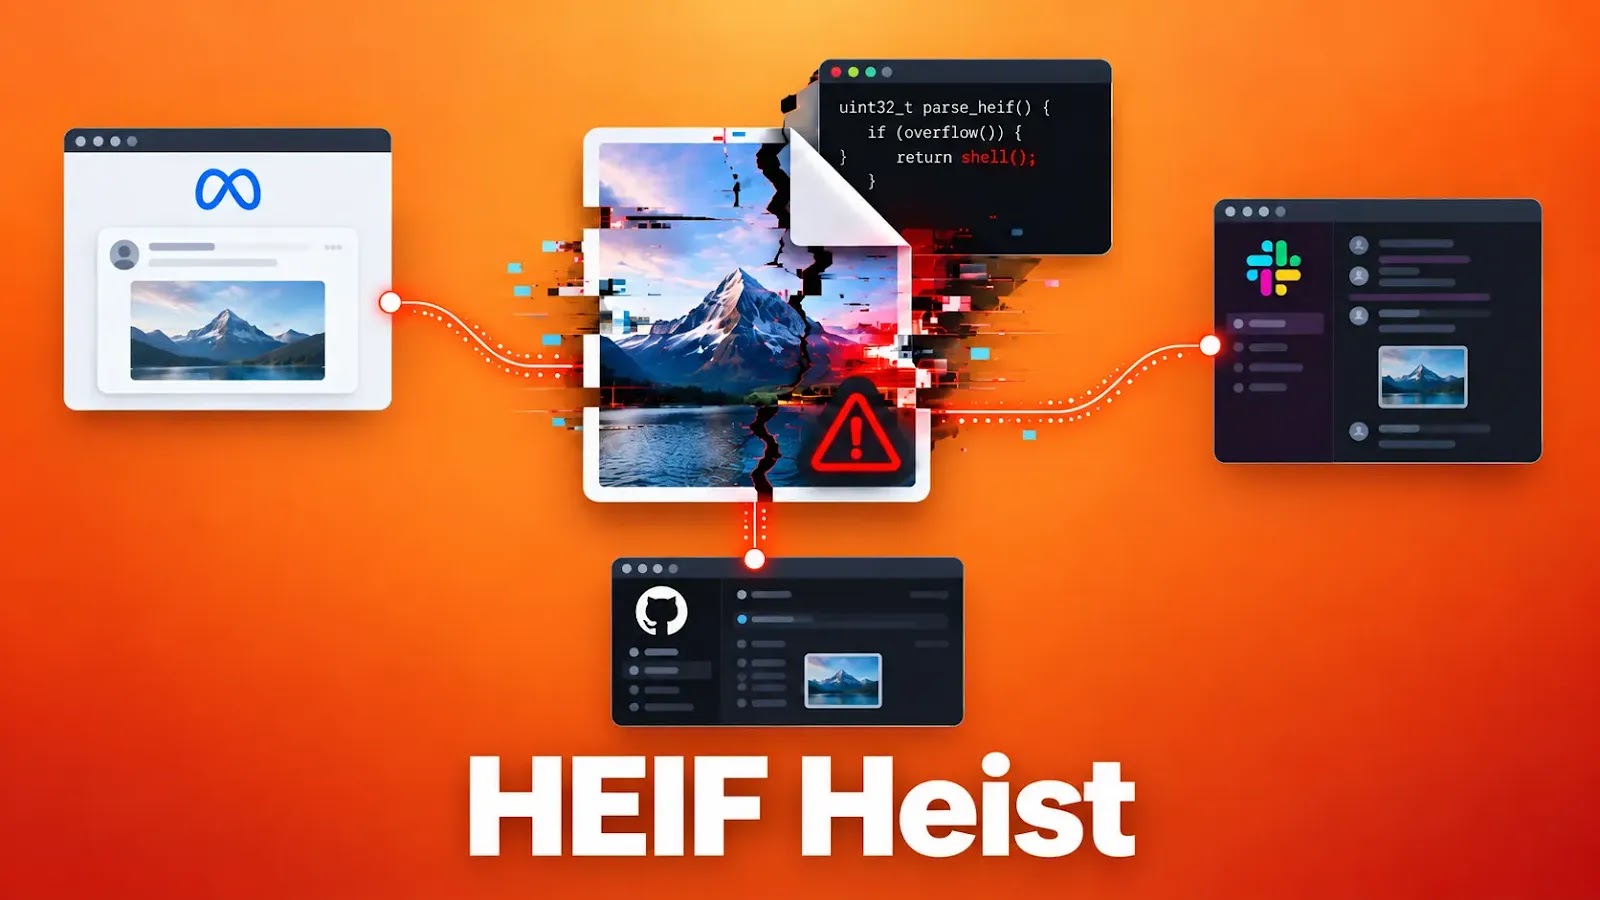 HEIF Heist: Remote Code Execution Vulnerabilities Exploited in Major Platforms The HEIF Heist refers to a class of vulnerabilities affecting image-processing libraries like libheif and libde265, allowing attackers to execute remote code through malicious HEIF, HEIC, or AVIF files. Disclosed by Hacktron, this issue impacts major platforms including Meta, Slack, and GitHub Enterprise, highlighting…