 Markets.Businessinsider
Asimily Launches Segmentation Orchestration to Combat AI-Driven Cyber Attacks
Article Content

- •Asimily launched Segmentation Orchestration to automate network policy enforcement.
- •The platform addresses the challenges posed by AI-driven attacks on connected devices.
- •Automation reduces manual effort and risk of disruption in network segmentation.
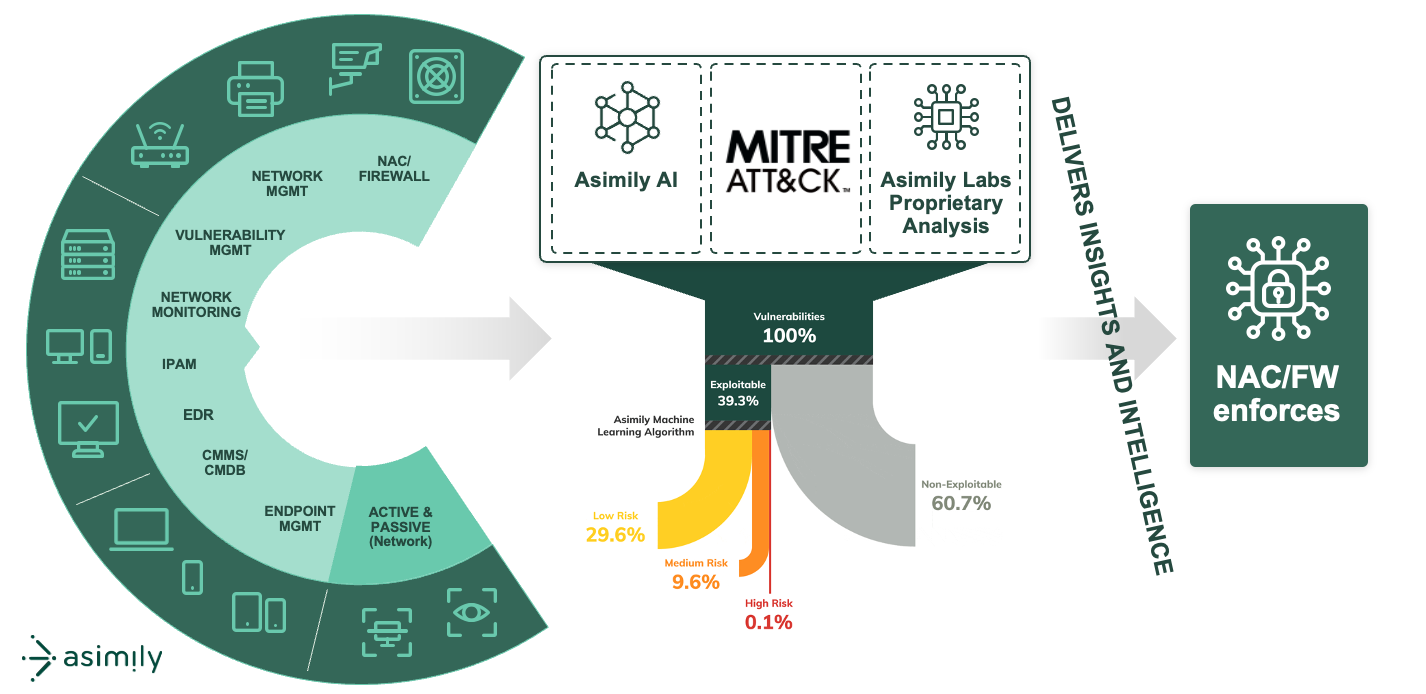
Asimily has introduced Segmentation Orchestration, a platform that automates the integration of connected-device risk intelligence into enforceable network policies. This innovation addresses the increasing sophistication and volume of AI-driven attacks targeting connected devices. CEO Shankar Somasundaram highlighted that traditional visibility tools and manual policies are insufficient against these threats. The platform combines asset visibility, vulnerability prioritization, and segmentation orchestration, enabling organizations to manage their network security more effectively. By automating the process from device discovery to dynamic policy deployment, Asimily aims to mitigate risks without disrupting operations. This solution is particularly relevant for IoT, OT, IoMT, and IT environments, where manual segmentation efforts have proven challenging. The launch is timely, as security teams face escalating attacks exploiting gaps in visibility and enforcement.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…