 civilnet.am
Azerbaijan's Cultural Revisionism Threatens Armenian Heritage in Nagorno-Karabakh
Article Content

- •Azerbaijan organized a tour promoting its narrative of Armenian heritage as Caucasian Albanian.
- •Over 120,000 Armenians were expelled from Nagorno-Karabakh in September 2023, raising ethnic cleansing concerns.
- •Armenia's government has not publicly responded to the Azerbaijani tour or its implications.
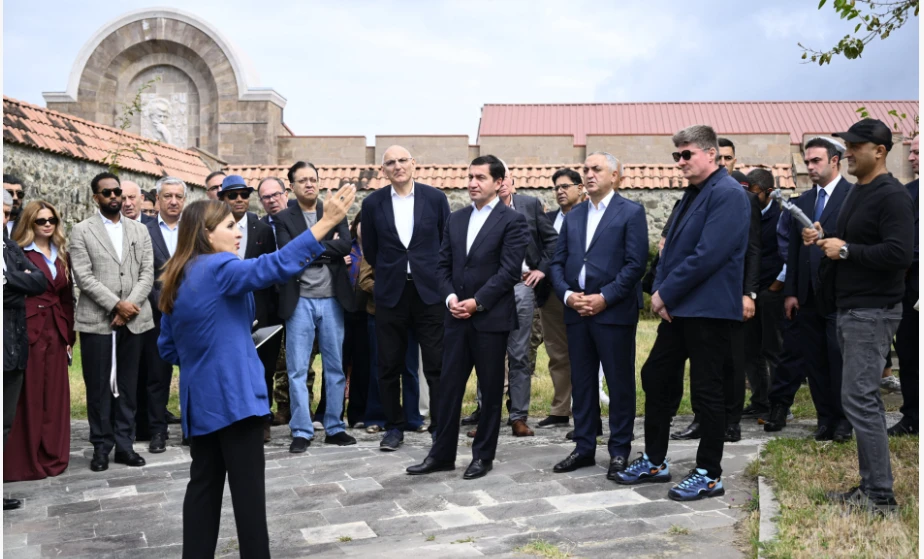
Azerbaijan recently hosted a tour for foreign diplomats to promote its narrative that Armenian cultural sites in Nagorno-Karabakh are actually Caucasian Albanian. This event, which included representatives from 58 countries, has drawn criticism from former Nagorno-Karabakh officials and Armenian scholars. The Azerbaijani government has been accused of using this tour to further its agenda of erasing Armenian heritage following the expulsion of over 120,000 Armenians from the region in September 2023, which many observers labeled as ethnic cleansing. Despite the significant implications for peace in the South Caucasus, Armenia's government has not publicly responded to these developments. The lack of engagement from Armenian state institutions raises concerns about the preservation of Armenian identity in the region. The systematic revisionism by Azerbaijan is seen as a direct threat to long-term stability and reconciliation efforts between Armenia and Azerbaijan.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What was the purpose of the Azerbaijani tour?
What happened to the Armenian population in Nagorno-Karabakh?
Has Armenia responded to Azerbaijan's actions?
Continue Reading
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…
 Critical Zero-Day Exploit Found in BeyondTrust Remote Support BeyondTrust disclosed a critical vulnerability, CVE-2026-102764, in its Remote Support product, exploited by the suspected China-linked group ARMORY CASTLE since August 2026. This flaw, with a CVSS score of 9.3, allows attackers to perform arbitrary file uploads and gain host-level control without requiring…