 www.kyivpost.com
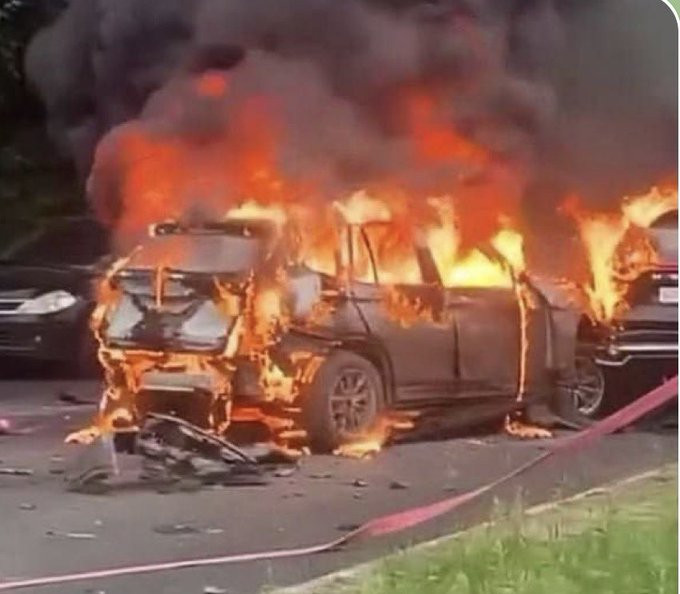
Car Bomb Kills Senior Russian General in Moscow Region
Article Content

- •Colonel Damir Davydov was killed in a car bomb attack in Balashikha, Moscow.
- •The explosion occurred at 5:30 AM on June 10, 2026, targeting a senior military logistics official.
- •A second car bomb was found and neutralized in southwest Moscow, indicating increased security threats.
A car bomb explosion in Balashikha, Moscow, killed Colonel Damir Davydov, head of the Russian military's missile and artillery supply. The attack occurred at approximately 5:30 AM on June 10, 2026, as Davydov was driving his BMW X3. This incident marks the latest in a series of targeted assassinations of Russian military officials amid ongoing conflict with Ukraine. A second car bomb was discovered and detonated by authorities in southwest Moscow, indicating heightened security concerns. Ukrainian authorities have not claimed responsibility for the attack, and there is currently no public evidence linking them to it. The Kremlin confirmed the explosion but did not disclose further details, citing an ongoing investigation. This assassination raises questions about the effectiveness of Russia's internal security measures to protect high-ranking officials.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Aughinish in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…