 Finance.Biggo
Cardano YouTube Channel Hacked for Deepfake Crypto Scam
Article Content

- •Cardano's YouTube channel was hacked to promote a deepfake scam.
- •The scam involved a fraudulent livestream claiming to double ADA holdings.
- •Users are warned against engaging with content from the compromised channel.
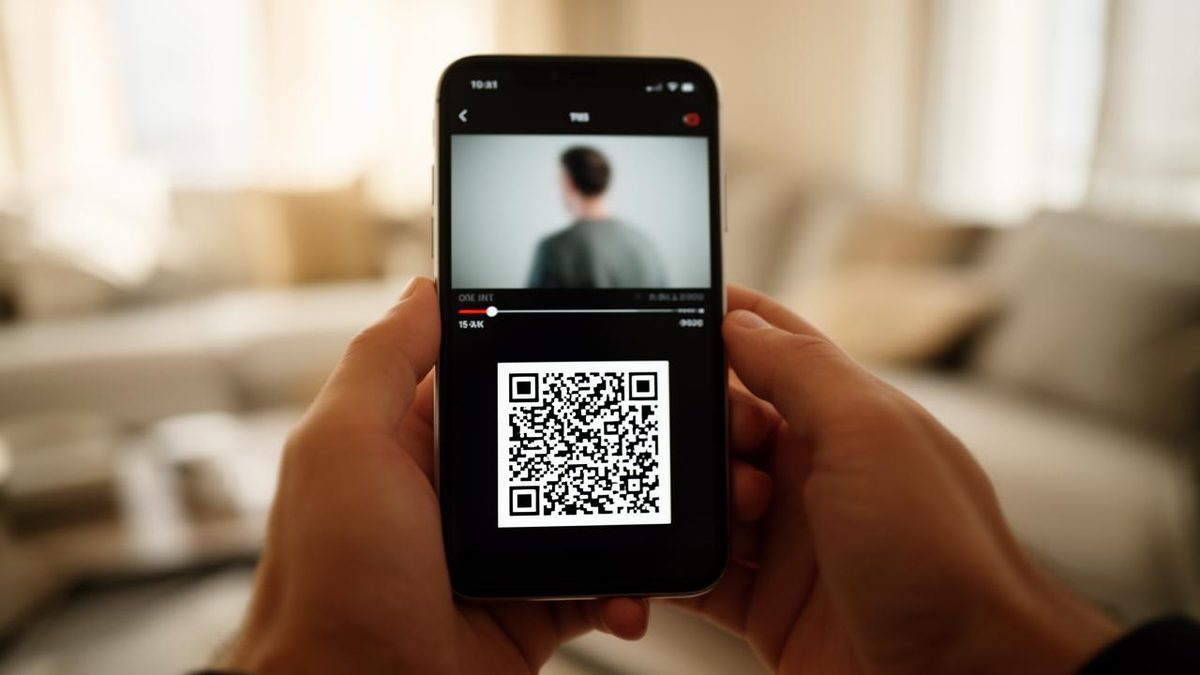
On September 18, 2026, the official YouTube channel of Input Output Global (IOG), the company behind Cardano, was hijacked to stream a deepfake video of founder Charles Hoskinson promoting a cryptocurrency giveaway scam. The fraudulent livestream, disguised as a Project Catalyst town hall, encouraged viewers to send ADA to a specified address via a QR code, falsely claiming they would double their holdings. Hoskinson confirmed the breach on X, warning users not to trust any content from the compromised channel. IOG is currently working to regain control of the account and remove the deceptive material. The incident highlights ongoing security concerns within the cryptocurrency community, as scams leveraging deepfake technology are becoming increasingly prevalent. Users are advised to avoid clicking links or scanning QR codes from the affected account, as cryptocurrency transactions are irreversible and funds sent to attacker-controlled wallets are difficult to recover.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Job Seeker, AI Stealer and Cardano in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical GitLab CVE-2026-85706 Exploited; Microsoft Issues Record 974 Patches A critical CVE-2026-85706 path-traversal vulnerability in GitLab (CVSS 10.0) was exploited in the wild just hours after its disclosure on September 12, 2026. Microsoft released its largest-ever patch batch, addressing 974 vulnerabilities, including several actively exploited Windows flaws. The GitLab flaw allows…