 www.cardlab.com
CardLab to Present Passwordless Biometric Security at Cyber Security Festival 2026
Article Content

- •CardLab will exhibit its biometric authentication technology at the Cyber Security Festival 2026.
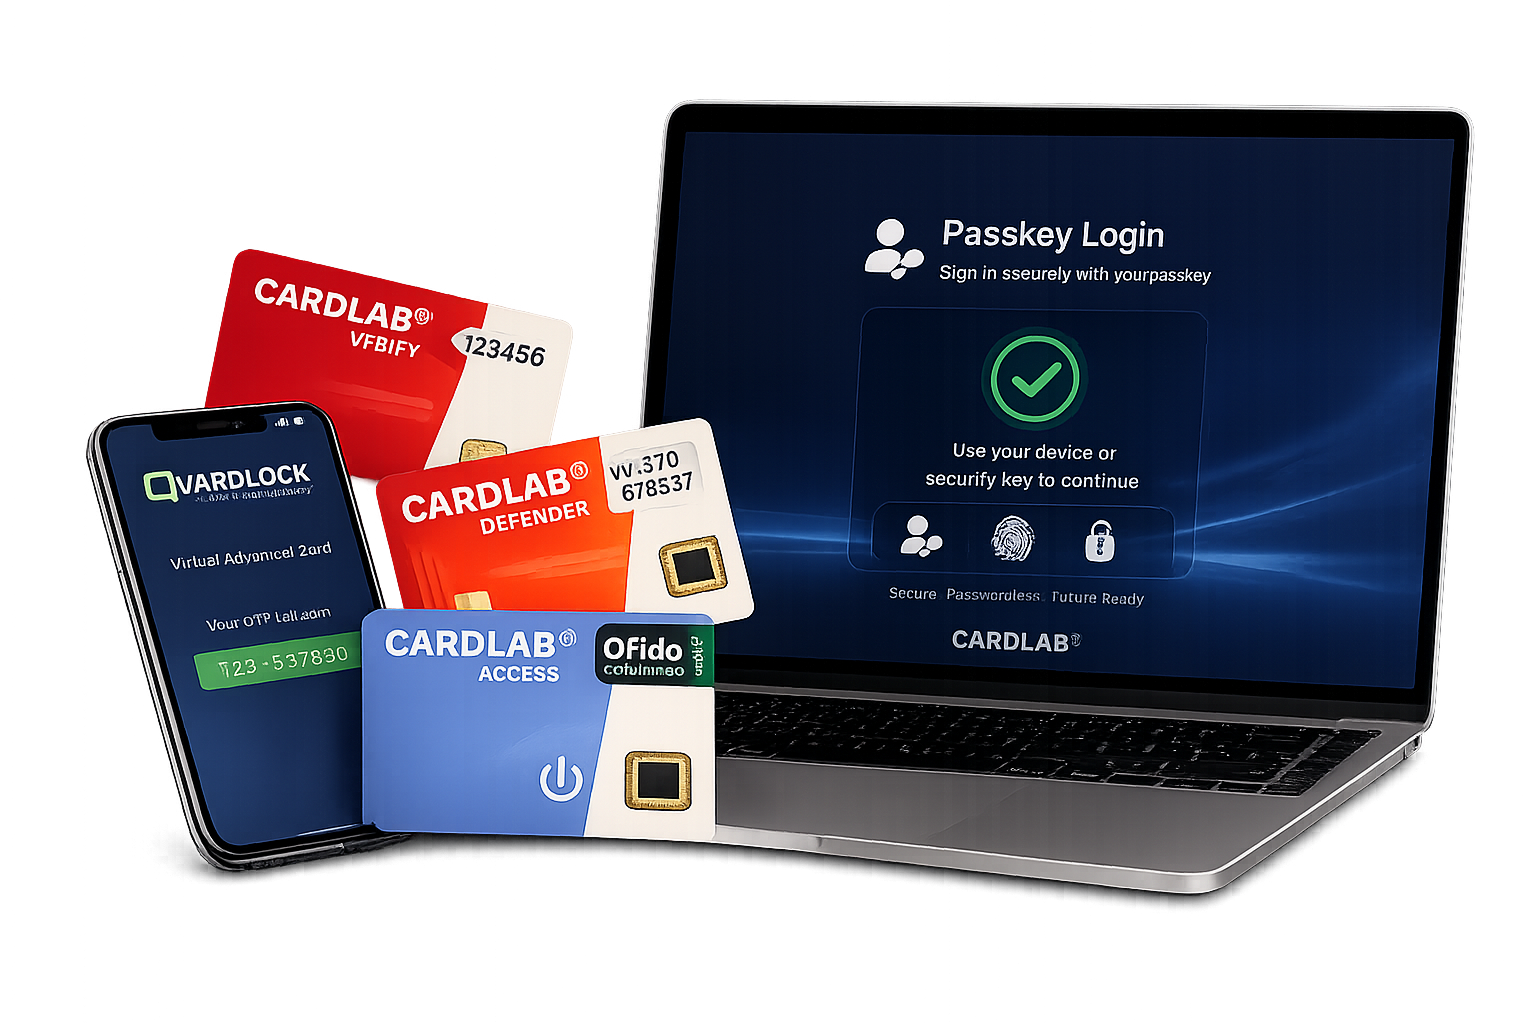
- •The Access FIDO biometric card combines fingerprint recognition with FIDO2 authentication.
- •CardLab's solutions aim to eliminate password reliance and enhance security across various sectors.
CardLab is set to showcase its biometric authentication technology at the Cyber Security Festival 2026 in Copenhagen on October 18-19. The Danish company will demonstrate its Access FIDO biometric card, which integrates fingerprint recognition with FIDO2 authentication to enhance security against unauthorized access. This technology aims to eliminate the reliance on passwords, addressing vulnerabilities associated with phishing and identity fraud. CardLab's solutions cater to various sectors, including healthcare, government, and remote work, emphasizing secure access management. The event will provide an opportunity for attendees to engage with CardLab's team and learn about advancements in biometric security solutions. The company was founded in 2006 following the founder's experience with credit card data theft, driving a focus on robust digital security.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track CardLab in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the Access FIDO biometric card?
How does CardLab's technology enhance security?
Where can I see CardLab's demonstration?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…