 www.diariandorra.ad
CASS Warns of Fraudulent SMS Campaign Targeting Citizens
Article Content
Browse articles 
- •CASS warns of fraudulent SMS impersonating their identity.
- •Messages claim imminent expiration of health cards and include phishing links.
- •CASS advises citizens to delete suspicious messages and contact them directly.
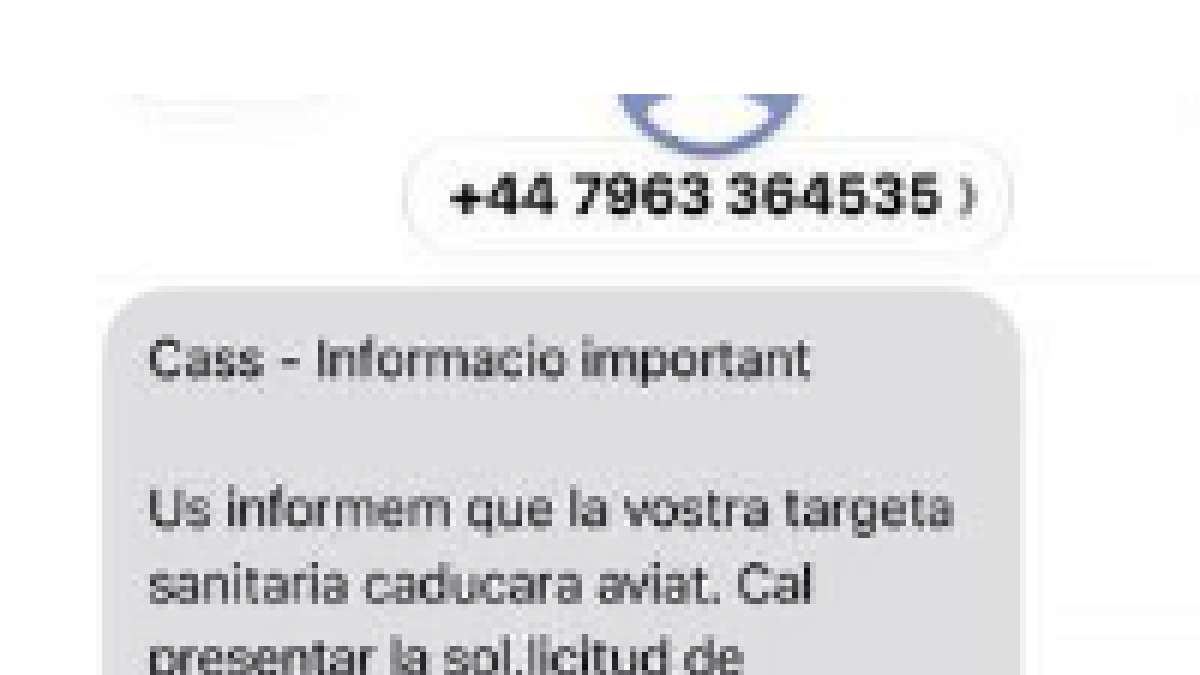
The Caixa Andorrana de Seguretat Social (CASS) has issued a warning regarding a fraudulent SMS campaign impersonating their identity. The messages claim that the health card is about to expire and include a link for renewal. CASS emphasizes that they never request personal data via text messages and advises recipients to avoid clicking on links or providing personal information. Citizens are encouraged to delete the messages and contact CASS directly through official channels if in doubt. The organization is actively working to prevent such fraud attempts and protect users from digital scams.
Ask AI about this cluster
Answers cite the sources they use
Updated just now How this analysis works
Timeline
2026-10-12
CASS issues warning about fraudulent SMS
CASS alerts the public about a campaign of fraudulent SMS messages impersonating their identity to collect personal data.
Diari d'Andorra2026-10-12
CASS advises against clicking links
CASS reminds citizens that they do not request personal information via text and advises against clicking links in suspicious messages.
Bon DiaMore articles in this cluster (2)
Common questions
What should I do if I receive one of these messages?
Do not click any links or provide personal information; delete the message and contact CASS directly.
How can I verify if a message is legitimate?
Contact CASS through their official channels to confirm any requests for information.
What measures is CASS taking against these scams?
CASS is actively working to prevent fraud and protect users from digital scams.
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…