 Pasqualepillitteri.It
Cellebrite Reveals LOKI: Zero-Day Boot ROM Exploit for Apple Devices
Article Content

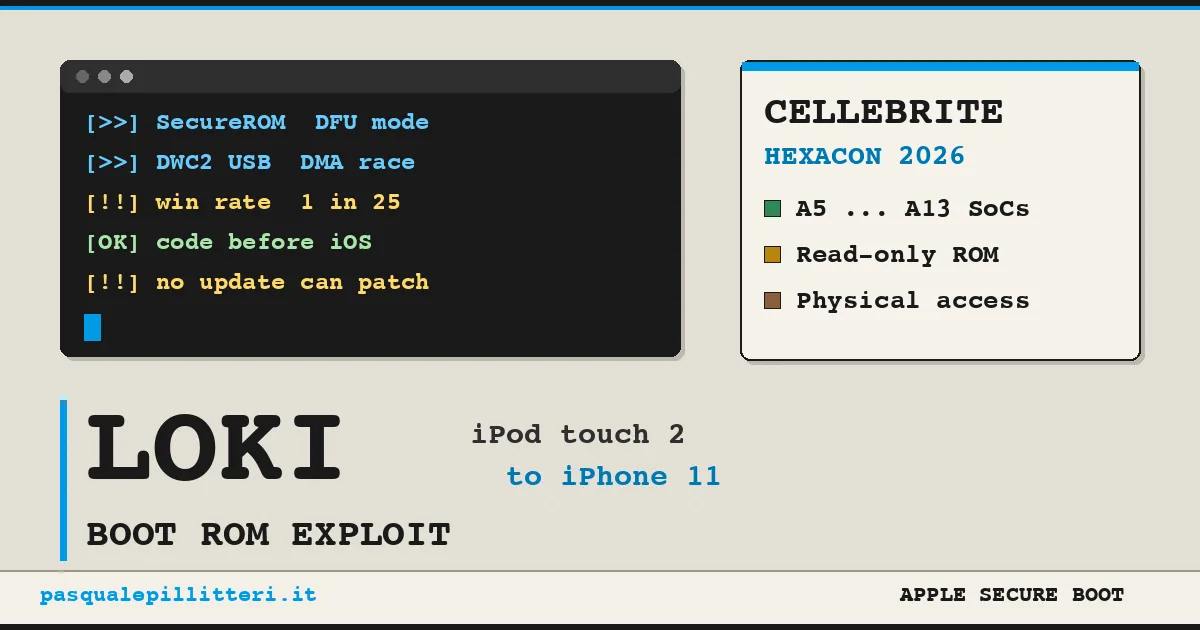
- •Cellebrite's LOKI exploit targets Apple boot ROMs from iPod touch 2 to iPhone 11.
- •The exploit requires physical access and operates in DFU mode via USB.
- •Early proofs of concept show a low success rate of 1 in 25 attempts.
Cellebrite has unveiled a zero-day exploit named LOKI at the Hexacon conference, targeting the boot ROM of Apple chips from the iPod touch 2 to the iPhone 11. This exploit, which requires physical access to the device via USB in DFU mode, takes advantage of a timing race condition, with early proof-of-concept builds achieving a success rate of only 1 in 25 attempts. The boot ROM is immutable and cannot be patched through software updates, making this a significant vulnerability. The exploit leverages a DMA bug in the Synopsys DesignWare USB controller, potentially affecting a decade's worth of Apple SoCs from A5 to A13. The session was presented by Steven De Franco, a known researcher from Cellebrite. The implications of this exploit are serious for users of older Apple devices, as it allows for data extraction before any operating system defenses are activated.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Apple in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Which Apple devices are affected by LOKI?
What is the method of exploitation?
Is there a patch available for this exploit?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 Silent Lynx Targets CIS Governments via WinRAR Exploit The threat actor Silent Lynx has launched a series of attacks against government organizations in the Commonwealth of Independent States (CIS) from June 2025 to August 2026. These attacks exploit a vulnerability in WinRAR (CVE-2025-8088) to deploy reverse shells, including FoalShell and PickleShell, facilitating…