 Insurancetimes
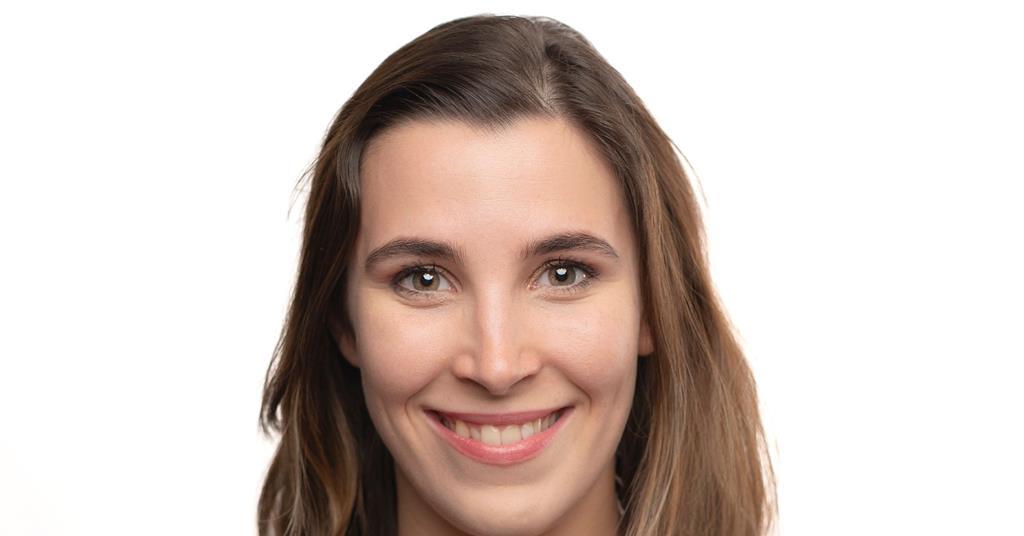
CFC Appoints Isabel Finn as Head of Cyber Exposure and Proactive Risk
Article Content

- •Isabel Finn appointed to lead CFC's cyber exposure and proactive risk efforts.
- •Role aims to translate complex cyber risk data into actionable insights for brokers and clients.
- •CFC responds to increasing demand for clearer cyber risk communication in the insurance market.
CFC has appointed Isabel Finn to a newly created role as head of cyber exposure and proactive risk. This position aims to enhance the understanding and management of cyber risk across the insurance lifecycle. Finn's responsibilities include translating real-world incident data and threat intelligence into actionable insights for brokers and clients. She will collaborate with CFC's underwriting and incident response teams to ensure that exposure insights inform underwriting assessments and claims strategies. Finn's previous experience includes roles at Canopius, FTI Consulting, and Darktrace, where she focused on cyber risk mitigation. The appointment reflects a growing demand for clearer insights into cyber exposure from brokers and clients. CFC's initiative is part of a broader trend in the insurance industry to improve the communication of cyber risk data. The company aims to provide more structured dialogue on cyber exposure data and its practical applications.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…