 Defenseone
China Dominates US Cyber Threat Landscape Amid Rising AI Concerns
Article Content

- •China is identified as the most active cyber threat to U.S. infrastructure.
- •AI is recognized as a defining technology that poses significant strategic challenges.
- •The U.S. must prepare for potential cyber attacks linked to conflicts over Taiwan.
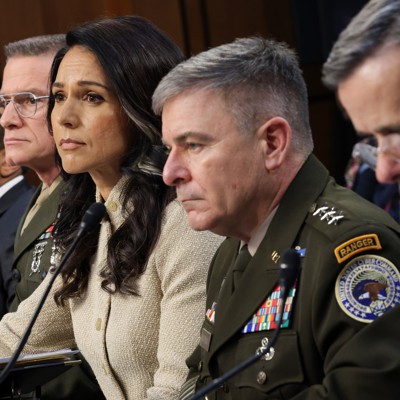
The U.S. Intelligence Community's 2026 Annual Threat Assessment identifies China as the most significant cyber threat to U.S. networks, emphasizing its persistent pre-positioning strategies. The report highlights China's capability to compromise critical infrastructure, particularly in the context of potential conflicts over Taiwan. In addition, the assessment elevates artificial intelligence (AI) as a major global threat, noting its use in combat and misinformation campaigns, with China being the leading competitor in AI development. The report warns that AI could be exploited by authoritarian regimes for mass surveillance and disinformation. The assessment reflects a shift in focus towards AI's strategic implications, indicating that it is reshaping the threat landscape. The U.S. must enhance its defenses against both state-sponsored cyber threats and the implications of AI in warfare and misinformation. The report does not provide specific attack methods or incidents but emphasizes the ongoing risks posed by these nation-state actors.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Stryker in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…