 Fdd
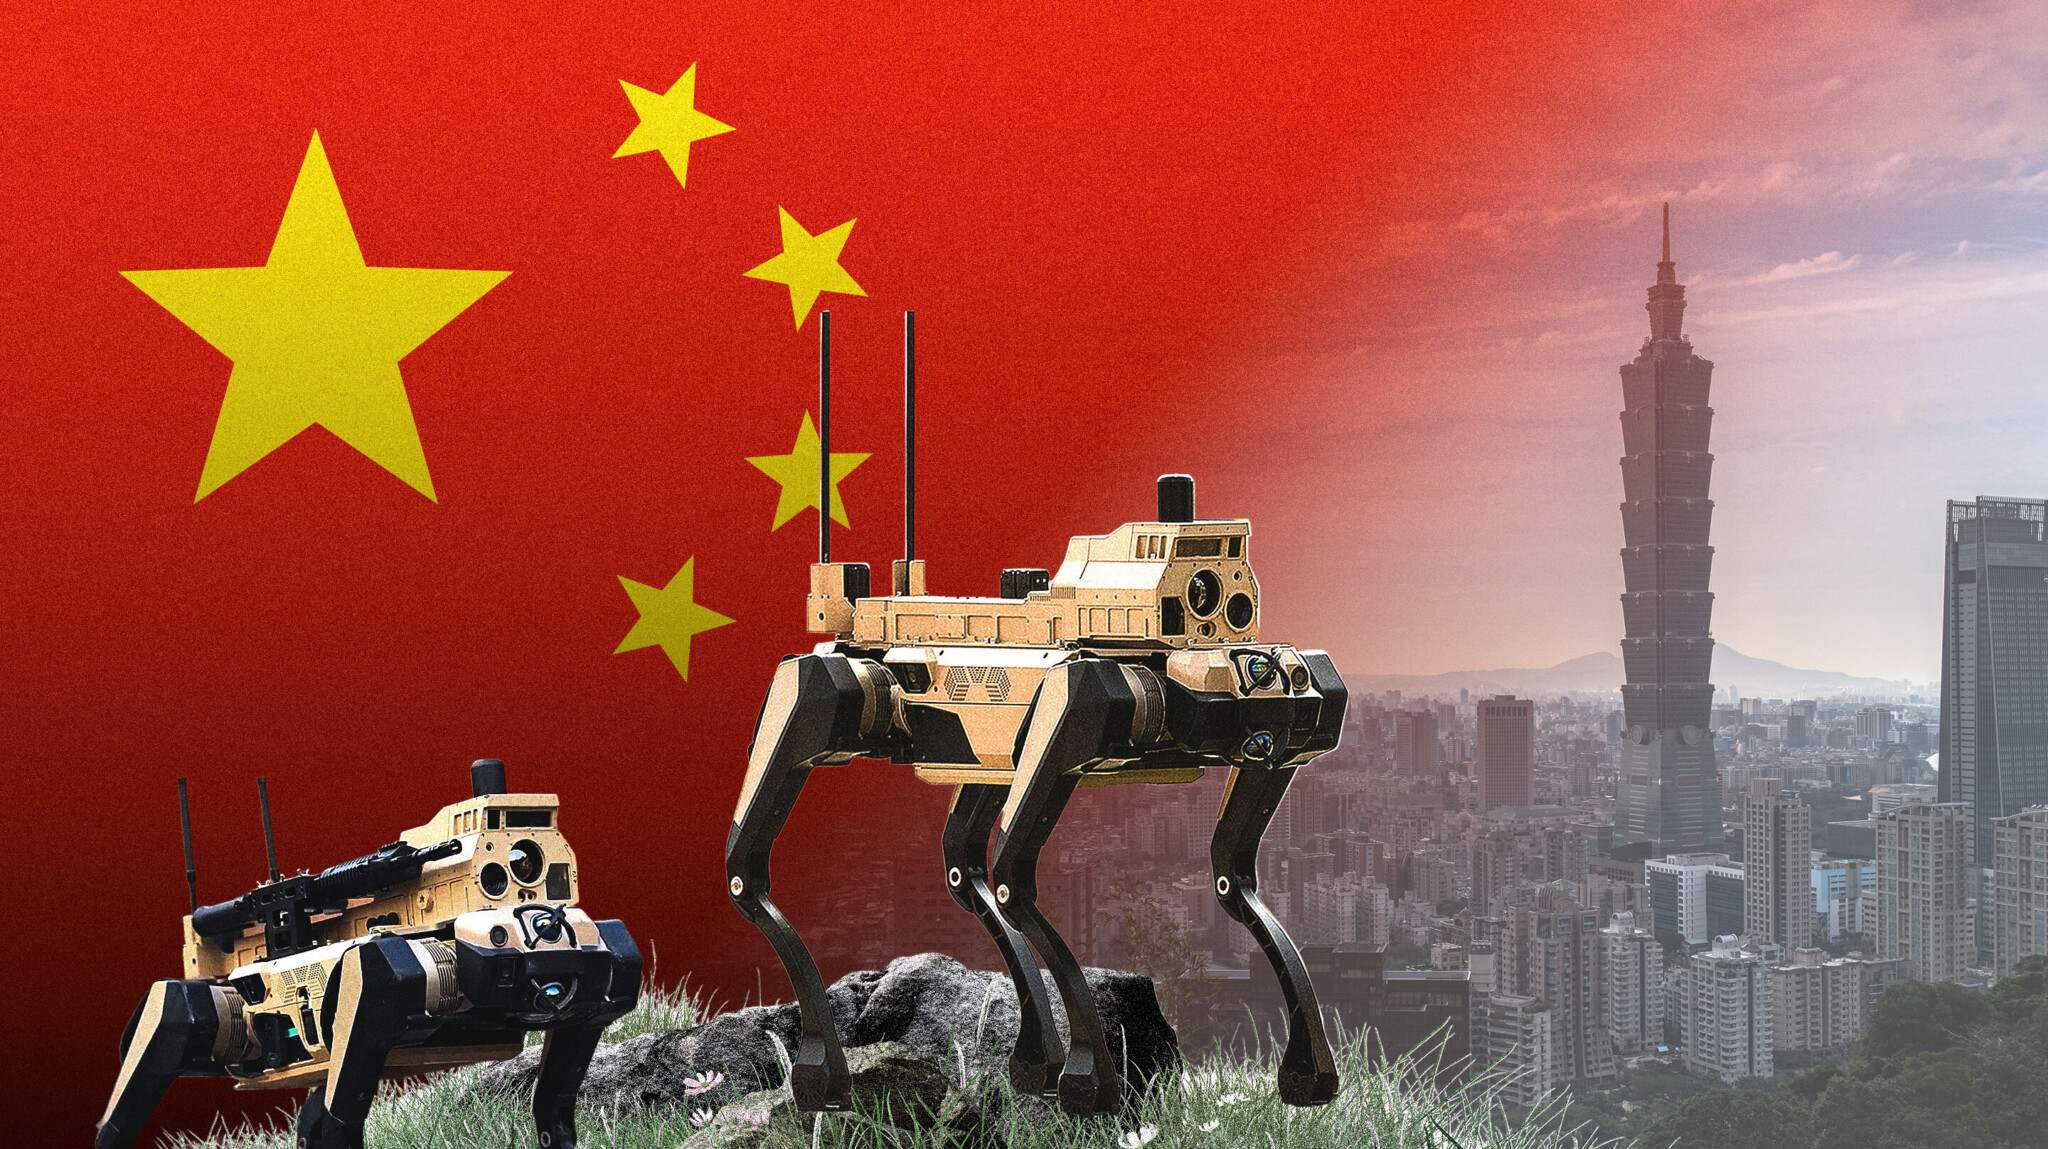
China's AI-Enabled Robotic Wolves Target Taiwan Conflict
Article Content

- •China is developing AI-driven robotic 'wolf packs' for military operations.
- •The PLA's focus on Taiwan highlights the strategic implications of these technologies.
- •U.S. policymakers need to adapt strategies to counter China's military advancements.
China is advancing its military capabilities by integrating AI and robotics into its warfare strategy, particularly focusing on a potential conflict with Taiwan. The People's Liberation Army (PLA) is developing quadruped robots, referred to as 'robotic wolves,' designed for reconnaissance, supply, and combat support. These systems are part of China's 'intelligentized warfare' approach, aiming to enhance operational effectiveness in challenging environments. The PLA's strategy includes using these robotic units to absorb losses and maintain momentum during initial combat phases. Analysts warn that this shift could lower the political and military costs for Beijing in a Taiwan invasion scenario. The U.S. is urged to reassess its response strategies to counter the PLA's advancements. The report highlights the importance of addressing vulnerabilities in China's military-civil fusion efforts and developing counter-robotics strategies. The rapid development of these systems raises concerns about their potential deployment in future conflicts.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (5)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…