 Indiatoday.In
China's Gwadar Port Faces Strategic Retreat Amid Security and Economic Challenges
Article Content

- •China's Gwadar Port is facing significant security and economic challenges.
- •The Baloch Liberation Army has escalated attacks on Chinese interests in the region.
- •China may downscale Gwadar from a commercial hub to a fortified naval station.
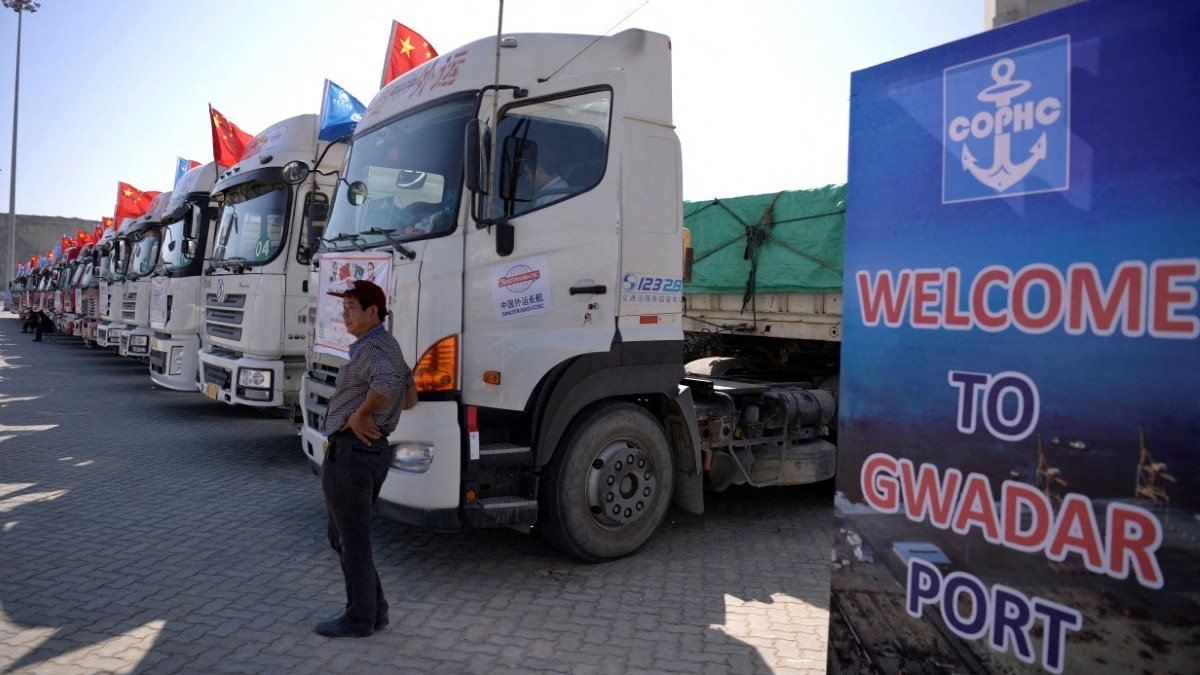
China's Gwadar Port, part of the China-Pakistan Economic Corridor (CPEC), is reportedly facing significant challenges that may lead to a strategic retreat. Security threats from insurgent groups, particularly the Baloch Liberation Army (BLA), have made the area increasingly dangerous for Chinese personnel and investments. The port was initially envisioned as a crucial maritime shortcut to bypass the Malacca Strait, but geographical difficulties and local insurgencies have hindered its commercial viability. Analysts suggest that instead of a bustling trade hub, Gwadar may be downscaled to a fortified naval refueling station. The BLA has escalated its attacks, shifting from guerrilla tactics to suicide operations aimed at maximizing casualties among Chinese workers. The Pakistani government has had to deploy special security forces to protect Chinese interests, but attacks continue, raising costs and complicating operations. As a result, China may restructure its lease and reduce its operational footprint at Gwadar, reflecting a shift in its investment strategy in Pakistan.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Hangeng Trade Company in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…
 Critical Zero-Day Vulnerability in F5 BIG-IP APM Exploited for Remote Code Execution F5 Networks has reported a critical vulnerability in its BIG-IP Access Policy Manager (APM), tracked as CVE-2026-94127, which is being actively exploited in the wild. The flaw allows unauthenticated attackers to execute remote code on systems configured with both an APM access policy and an OAuth profile. This…