 Foxnews
Chinese Technology Risks: Espionage Threats in Drones and Vehicles
Article Content

- •British naval drones were found transmitting data to China during a cybersecurity assessment.
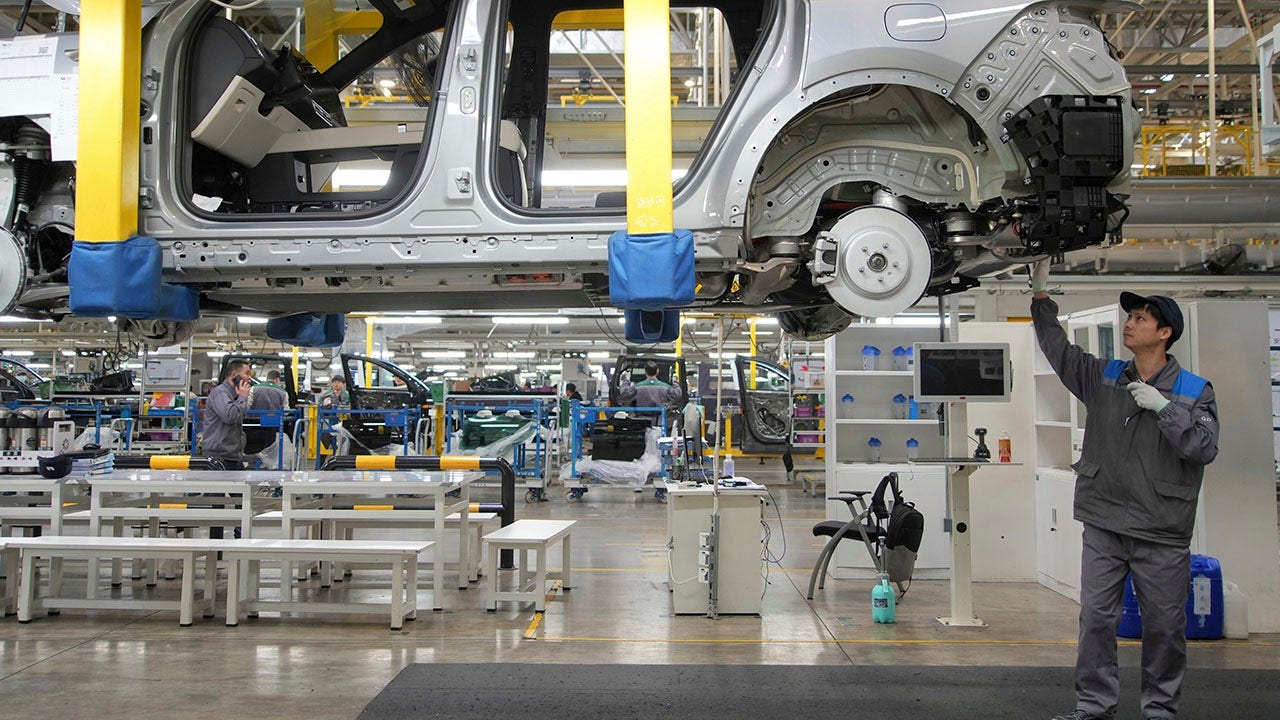
- •Chinese technology poses significant risks in both military and civilian sectors, particularly in vehicles.
- •U.S. lawmakers are urged to take action to prevent vulnerabilities from Chinese automotive technologies.
Recent reports highlight vulnerabilities in British naval drones that were found to be transmitting data to China, raising alarms about the risks associated with Chinese technology. The U.K. Ministry of Defence's cybersecurity assessment revealed that a component in its naval drones was secretly sending data to China. This incident reflects broader concerns regarding Chinese espionage tactics, particularly in the automotive sector, where Chinese companies are increasingly involved in connected vehicle technologies. Lawmakers in the U.S. are urged to act to prevent similar vulnerabilities in American vehicles, which could be exploited for surveillance or sabotage. The articles emphasize that while the risks from Chinese technology are significant, similar scrutiny should also be applied to American tech firms. The ongoing geopolitical tensions and the race for technological supremacy exacerbate these risks, making it critical for policymakers to address these vulnerabilities proactively.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track FBI in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…