 Securityweek
Chrome and Edge Extensions Found Tracking Users and Exploiting Vulnerabilities
Article Content
Browse articles 
Recent reports indicate that certain Chrome and Edge extensions have been tracking users by profiling them and accessing cookie data to create unique identifiers. These extensions have been executing malicious payloads using browser API access, raising significant security concerns for users of these browsers.
Ask AI about this cluster
Answers cite the sources they use
Updated 202d ago How this analysis works
More articles in this cluster (2)
Following this threat?
Track Hacking Team Spyware in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
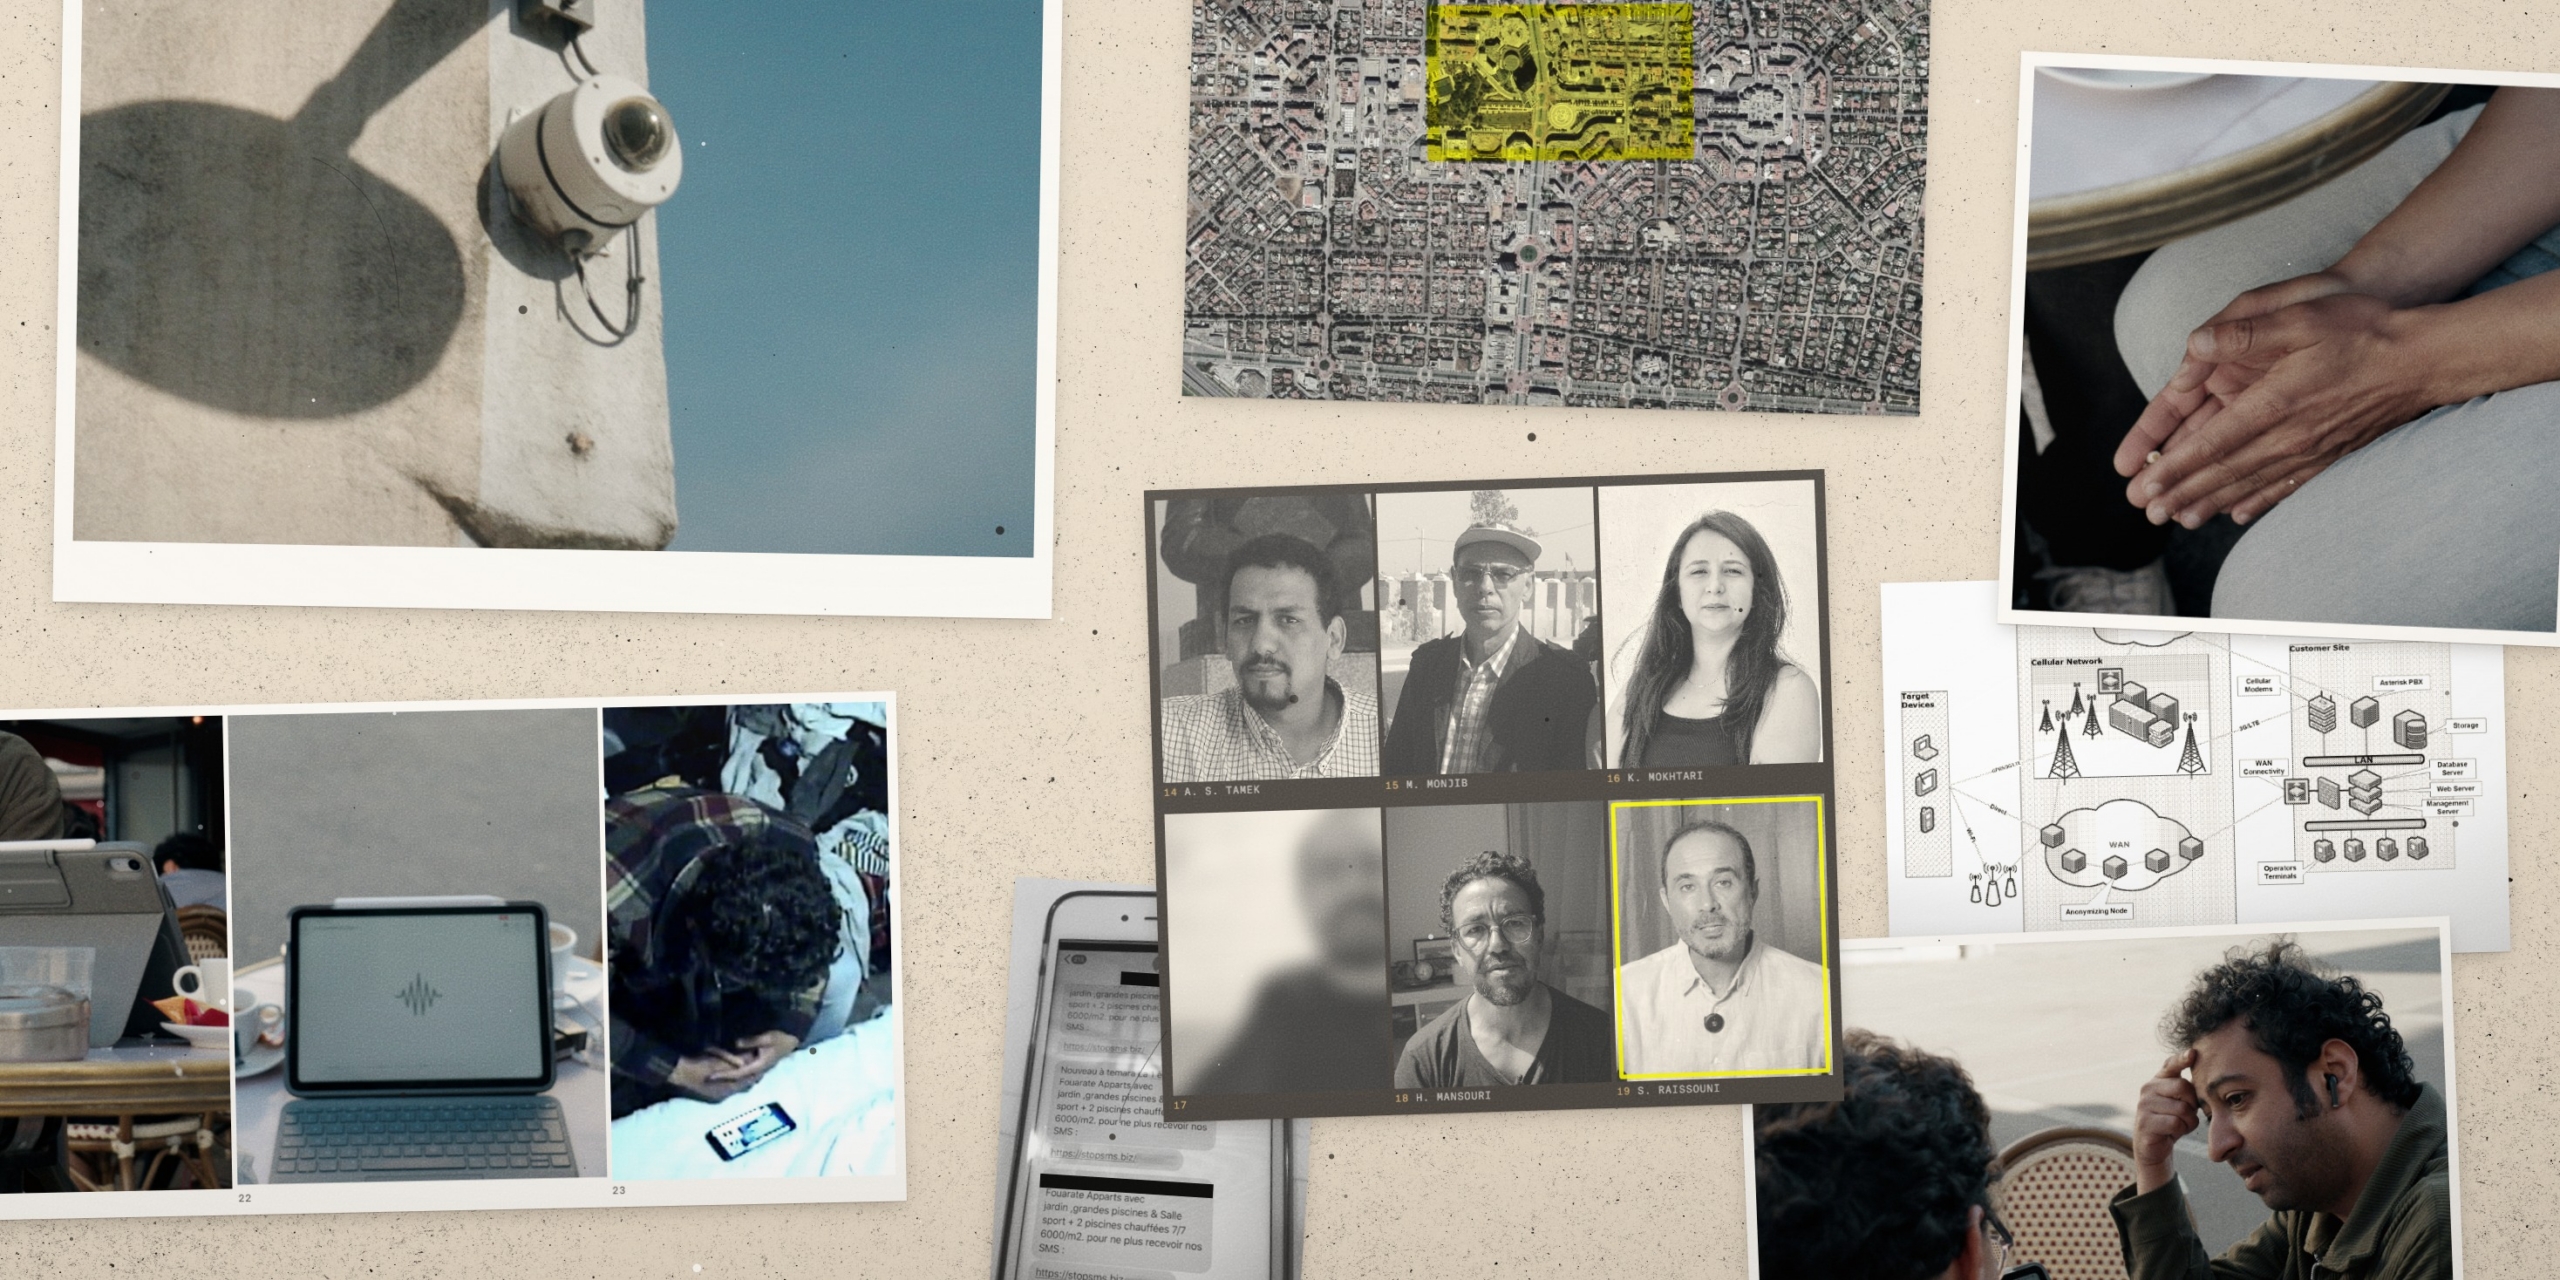 Morocco's Surveillance Network Targets Journalists and Activists Amnesty International has released a report detailing Morocco's extensive surveillance operations aimed at silencing journalists and human rights defenders. The report highlights the use of Pegasus spyware, which has targeted at least 103 phone numbers, including 65 civil society members and 22 journalists. The…
 Critical Zero-Day Exploits Target F5 and Check Point Products F5 Networks released emergency hotfixes for a critical zero-day vulnerability, CVE-2026-94127, in its BIG-IP Access Policy Manager on September 22, 2026, after confirming active exploitation. This flaw allows unauthenticated remote code execution (RCE) and has a CVSS score of 9.8. Concurrently, Check Point disclosed…