 Cbsnews
Coast Guard and FBI Investigate Cyber Threat on Texas-Bound Oil Tanker
Article Content

- •The VL Prosperity oil tanker was boarded due to suspected cyber compromise.
- •Iranian media reported the vessel lost communications and faced system manipulations.
- •The Coast Guard confirmed no operational disruptions or environmental impacts so far.
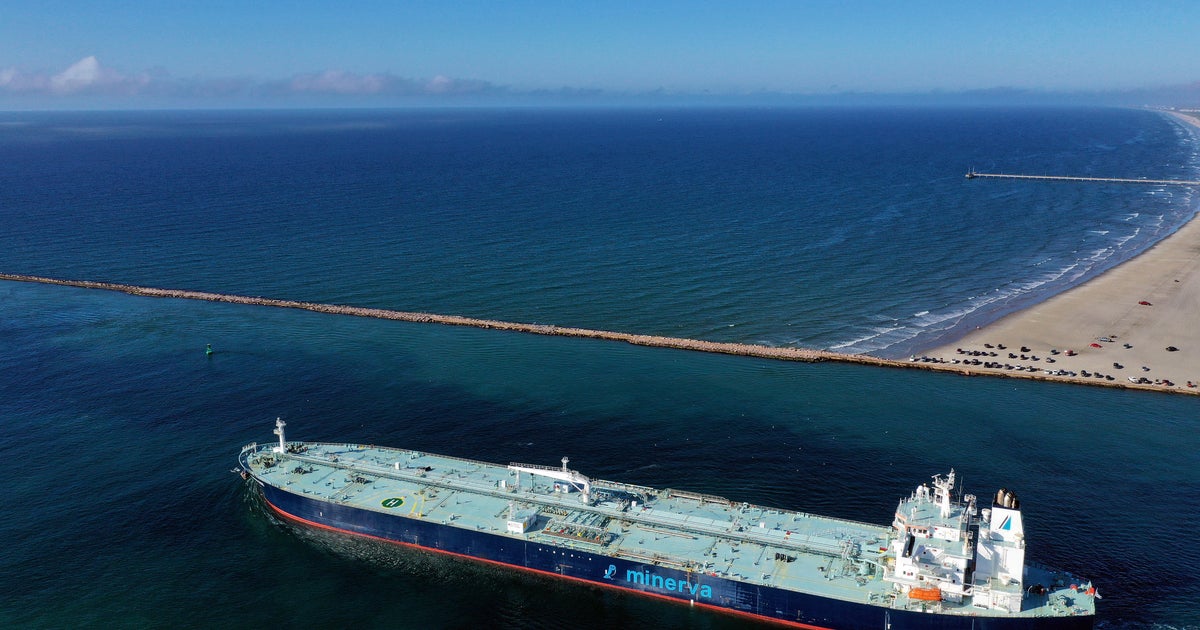
In August 2026, the U.S. Coast Guard and FBI boarded a foreign-flagged oil tanker, VL Prosperity, suspected of being compromised by foreign hackers while crossing the Atlantic. The boarding occurred on August 21 after the ship's network showed signs of a breach. Iranian media claimed the vessel lost communications for 30 hours and alleged that attackers manipulated critical systems, including engine controls. The U.S. has not confirmed the identity of the attackers but indicated a potential foreign state involvement. Currently, there are no reports of operational disruptions or environmental impacts. The Coast Guard is investigating the extent of the breach, which could allow attackers to control the vessel remotely. The incident highlights the vulnerabilities of modern tankers that rely on interconnected operational technology. No specific cyber vulnerabilities or tools have been disclosed yet.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Continue Reading
 Critical Cisco FMC Vulnerabilities Under Active Exploitation Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass authentication and… Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…