 gizmodo.com
Cold War Spy Satellite Explosion Creates Debris Threat in Low Earth Orbit
Article Content

- •USA-32 (FARRAH III) exploded on September 13, 2026, creating a debris cloud in low Earth orbit.
- •The satellite was part of a Cold War reconnaissance program aimed at intercepting Soviet communications.
- •No immediate threats to other satellites have been reported, but the situation is being closely monitored.
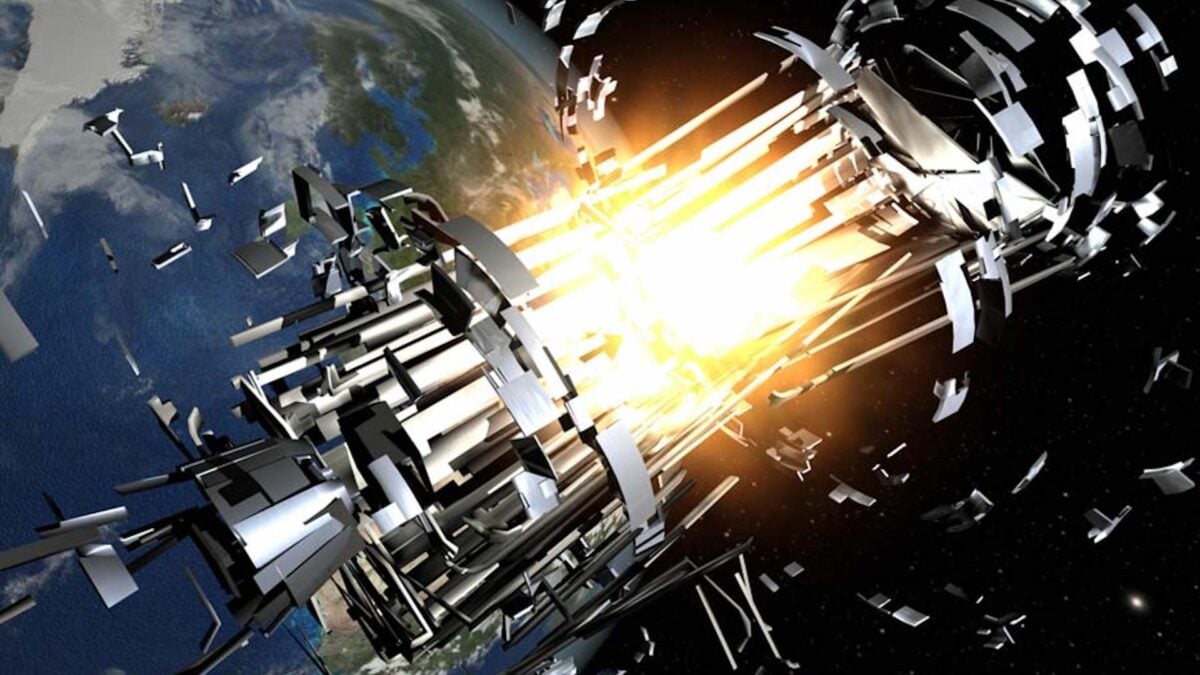
A Cold War-era spy satellite, USA-32 (FARRAH III), exploded in low Earth orbit on September 13, 2026, creating a significant debris cloud. The satellite, launched in 1988, was part of a reconnaissance program aimed at intercepting Soviet communications. The cause of the explosion remains unknown, but experts suggest it may have resulted from the degradation of components over time. The U.S. Space Force confirmed the fragmentation event, which could pose a threat to other operational satellites in the crowded orbital region. As of now, no immediate danger to active satellites has been reported, but tracking systems are monitoring the debris. The incident highlights ongoing concerns about space debris and its impact on satellite operations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track U.S. Space Force in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What caused the satellite explosion?
Is there a risk to other satellites?
What was the mission of USA-32?
Continue Reading
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…
 Lazarus APT Launches Operation FlashHole Using AI and Post-Quantum Cryptography Kaspersky has identified a cyberespionage campaign, dubbed Operation FlashHole, attributed to the Lazarus APT group, active since July 2025. The campaign has targeted at least three organizations in South Korea's construction, software, and wire-communication sectors. Attack methods include spear-phishing emails…