 Latimes
Congress to Investigate DHS and ICE Abuses Post-Election
Article Content

- •Democrats control both chambers of Congress after the November 2026 elections.
- •Investigations will focus on alleged abuses by DHS and ICE under the Trump administration.
- •Human Rights Watch urges Congress to prioritize human rights and restore oversight mechanisms.
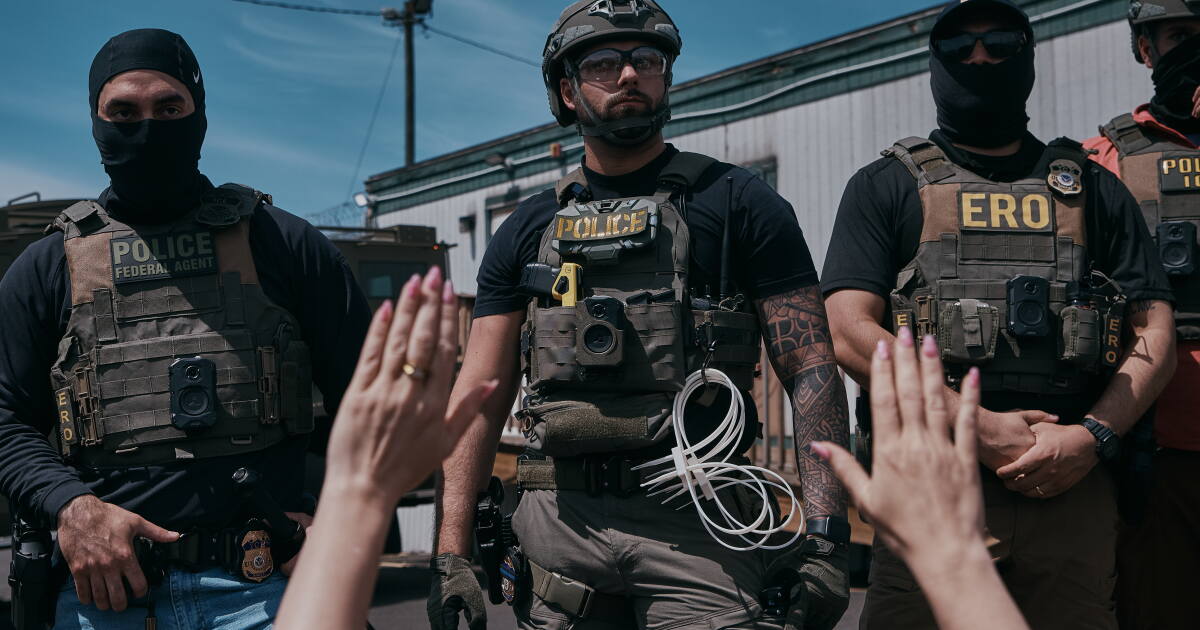
Following the November 3, 2026 midterm elections, Democrats gained control of both the House and Senate, prompting plans for investigations into the Department of Homeland Security (DHS) and Immigration and Customs Enforcement (ICE) regarding alleged abuses. House Homeland Security Committee Democrats have signaled their intent to hold accountable officials from the Trump administration, particularly focusing on immigration enforcement practices that have reportedly led to arbitrary detentions and human rights violations. Rep. Robert Garcia, set to lead the House Committee on Oversight and Government Reform, emphasized the need for accountability for DHS abuses. Human Rights Watch has called for the new Congress to prioritize human rights protections and restore oversight mechanisms that were weakened during the Trump administration. The incoming Congress is expected to challenge the continuation of aggressive immigration policies and seek reforms to ensure humane treatment of individuals in the immigration system.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What specific abuses are being investigated?
How will the new Congress affect immigration policy?
What actions can we expect from Congress?
Continue Reading
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…
 GitLab Issues Emergency Patch for Critical RCE Vulnerability GitLab has released emergency patches for a critical remote code execution vulnerability, CVE-2026-97229, affecting its Community and Enterprise Editions. This flaw, stemming from an integer overflow in the CI/CD regular expression compiler, allows unauthenticated attackers to execute arbitrary code via specially…