 Horizon3.Ai
Critical RCE Vulnerabilities in AhsayCBS Exploited
Article Content

- •CVE-2026-105133 allows unauthenticated access to sensitive operations.
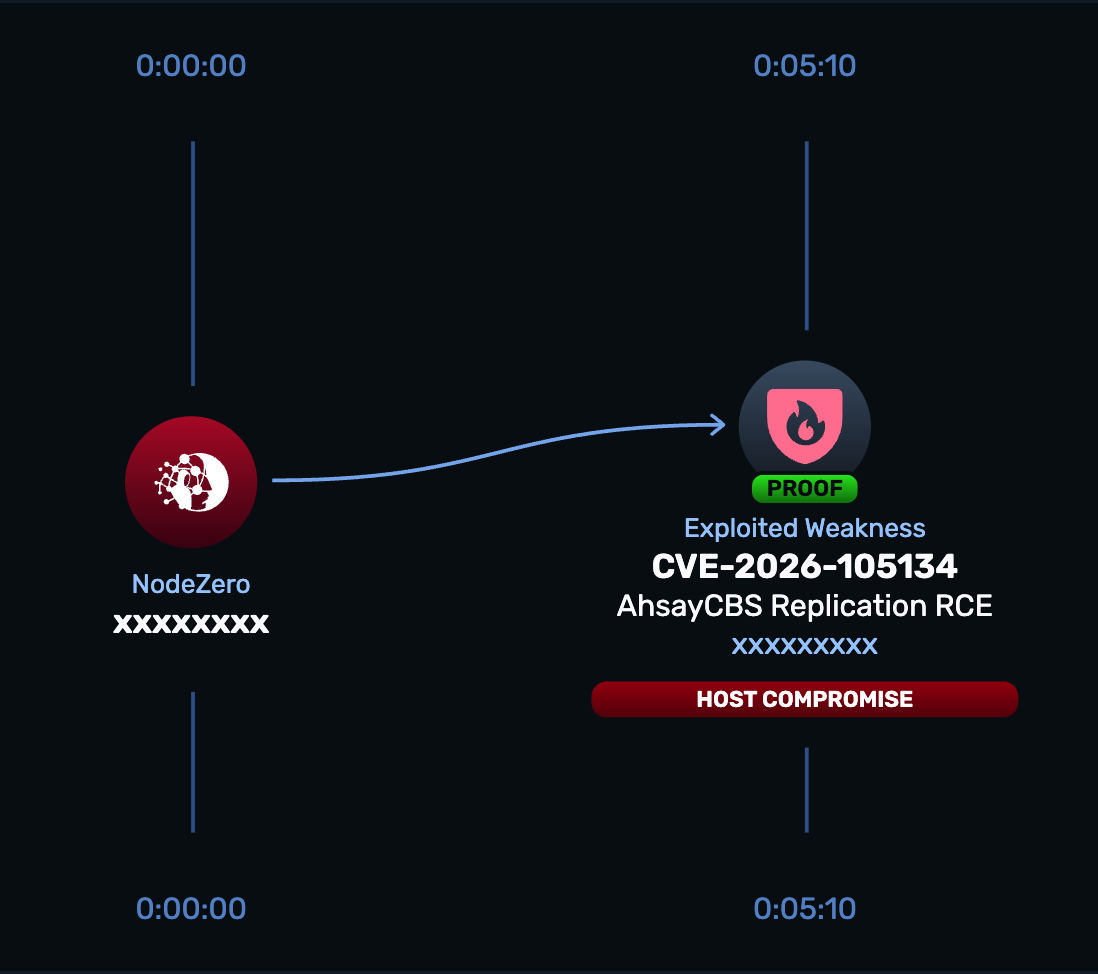
- •CVE-2026-105134 enables critical remote code execution via path traversal.
- •Both vulnerabilities are actively exploited, with confirmed attacks reported.
CVE-2026-105133 and CVE-2026-105134 affect AhsayCBS (Cloud Backup Server), allowing attackers to bypass authentication and execute code on exposed servers. CVE-2026-105133, with a CVSS score of 7.3, enables unauthenticated access to the JSON API, while CVE-2026-105134, rated 10.0, allows remote code execution through a path traversal vulnerability. Both vulnerabilities were confirmed to be, with attackers using JSP webshells and cryptocurrency miners. The vulnerabilities were added to the CISA KEV list on 2026-10-14, indicating ongoing exploitation. AhsayCBS versions 10.3.4 and earlier are affected, and immediate patching is recommended to mitigate risks.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track CVE-2026-105133 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Which AhsayCBS versions are affected?
What is the current exploitation status?
What immediate actions should be taken?
Continue Reading
 Ivanti Connect Secure Zero-Day CVE-2026-104935 Exploited in the Wild On October 13, 2026, Ivanti disclosed a high-severity zero-day vulnerability tracked as CVE-2026-104935, affecting its Connect Secure (ICS) VPN appliances. This authentication bypass flaw allows unauthenticated attackers to execute arbitrary commands, with exploitation confirmed since at least October 1. The…
 Critical AhsayCBS Vulnerabilities Exploited for RCE and Crypto Mining Cybersecurity firm Huntress has reported of two critical vulnerabilities in AhsayCBS, a cloud backup server management console used by managed service providers. The vulnerabilities, CVE-2026-105133 and CVE-2026-105134, were disclosed on October 4, 2026, and allow unauthenticated remote code execution (RCE) by…