 Dw
Cuba's Drone Acquisition Raises Concerns Over Potential Attacks on U.S. Targets
Article Content

- •Cuba has acquired over 300 drones from Russia and Iran, raising security concerns.
- •U.S. officials are monitoring discussions of potential drone attacks on U.S. military targets.
- •Cuban officials deny the allegations, claiming they are fabrications by the U.S. government.
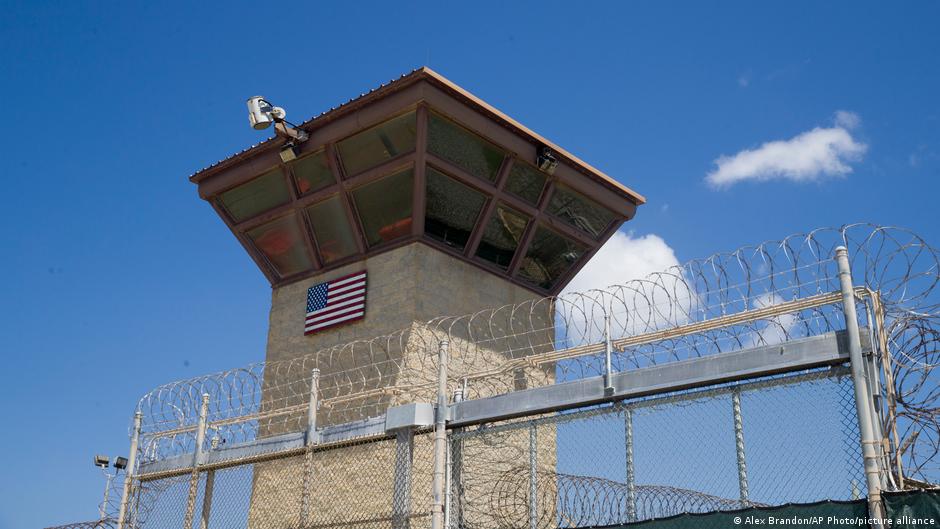
Cuba has reportedly acquired over 300 military drones from Russia and Iran, with discussions of potential attacks on U.S. military installations, including the Guantanamo Bay naval base and Key West. U.S. intelligence indicates that Cuban officials are exploring military options amid deteriorating relations with Washington. Cuban Foreign Minister Bruno Rodríguez has dismissed these reports as U.S. propaganda aimed at justifying economic sanctions and military aggression. The U.S. government, while acknowledging the proximity of these capabilities, does not currently view Cuba as an immediate military threat. However, the presence of Iranian military advisors in Cuba and the strategic implications of drone warfare are causing significant concern among U.S. officials. The situation is further complicated by the U.S. indictment plans against former Cuban leader Raul Castro, which could escalate tensions further.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (11)
Continue Reading
 Critical WSO2 API Manager Vulnerability Under Active Exploitation A critical vulnerability (CVE-2026-5430) in WSO2 API Manager is being actively exploited, allowing unauthenticated attackers to forge admin tokens via JWT authentication bypass. This flaw, which has a CVSS score of 10.0, affects multiple WSO2 products including API Manager, Universal Gateway, Traffic Manager, and API…
 Critical Linux Kernel Vulnerability CVE-2025-39682 Under Active Exploitation A critical vulnerability (CVE-2025-39682) in the Linux kernel allows remote code execution through mishandling of zero-length TLS records. This flaw affects kTLS-enabled hosts running vulnerable kernel versions, exposing them to attackers without authentication. CISA added this vulnerability to its Known Exploited…