 Glitchwire
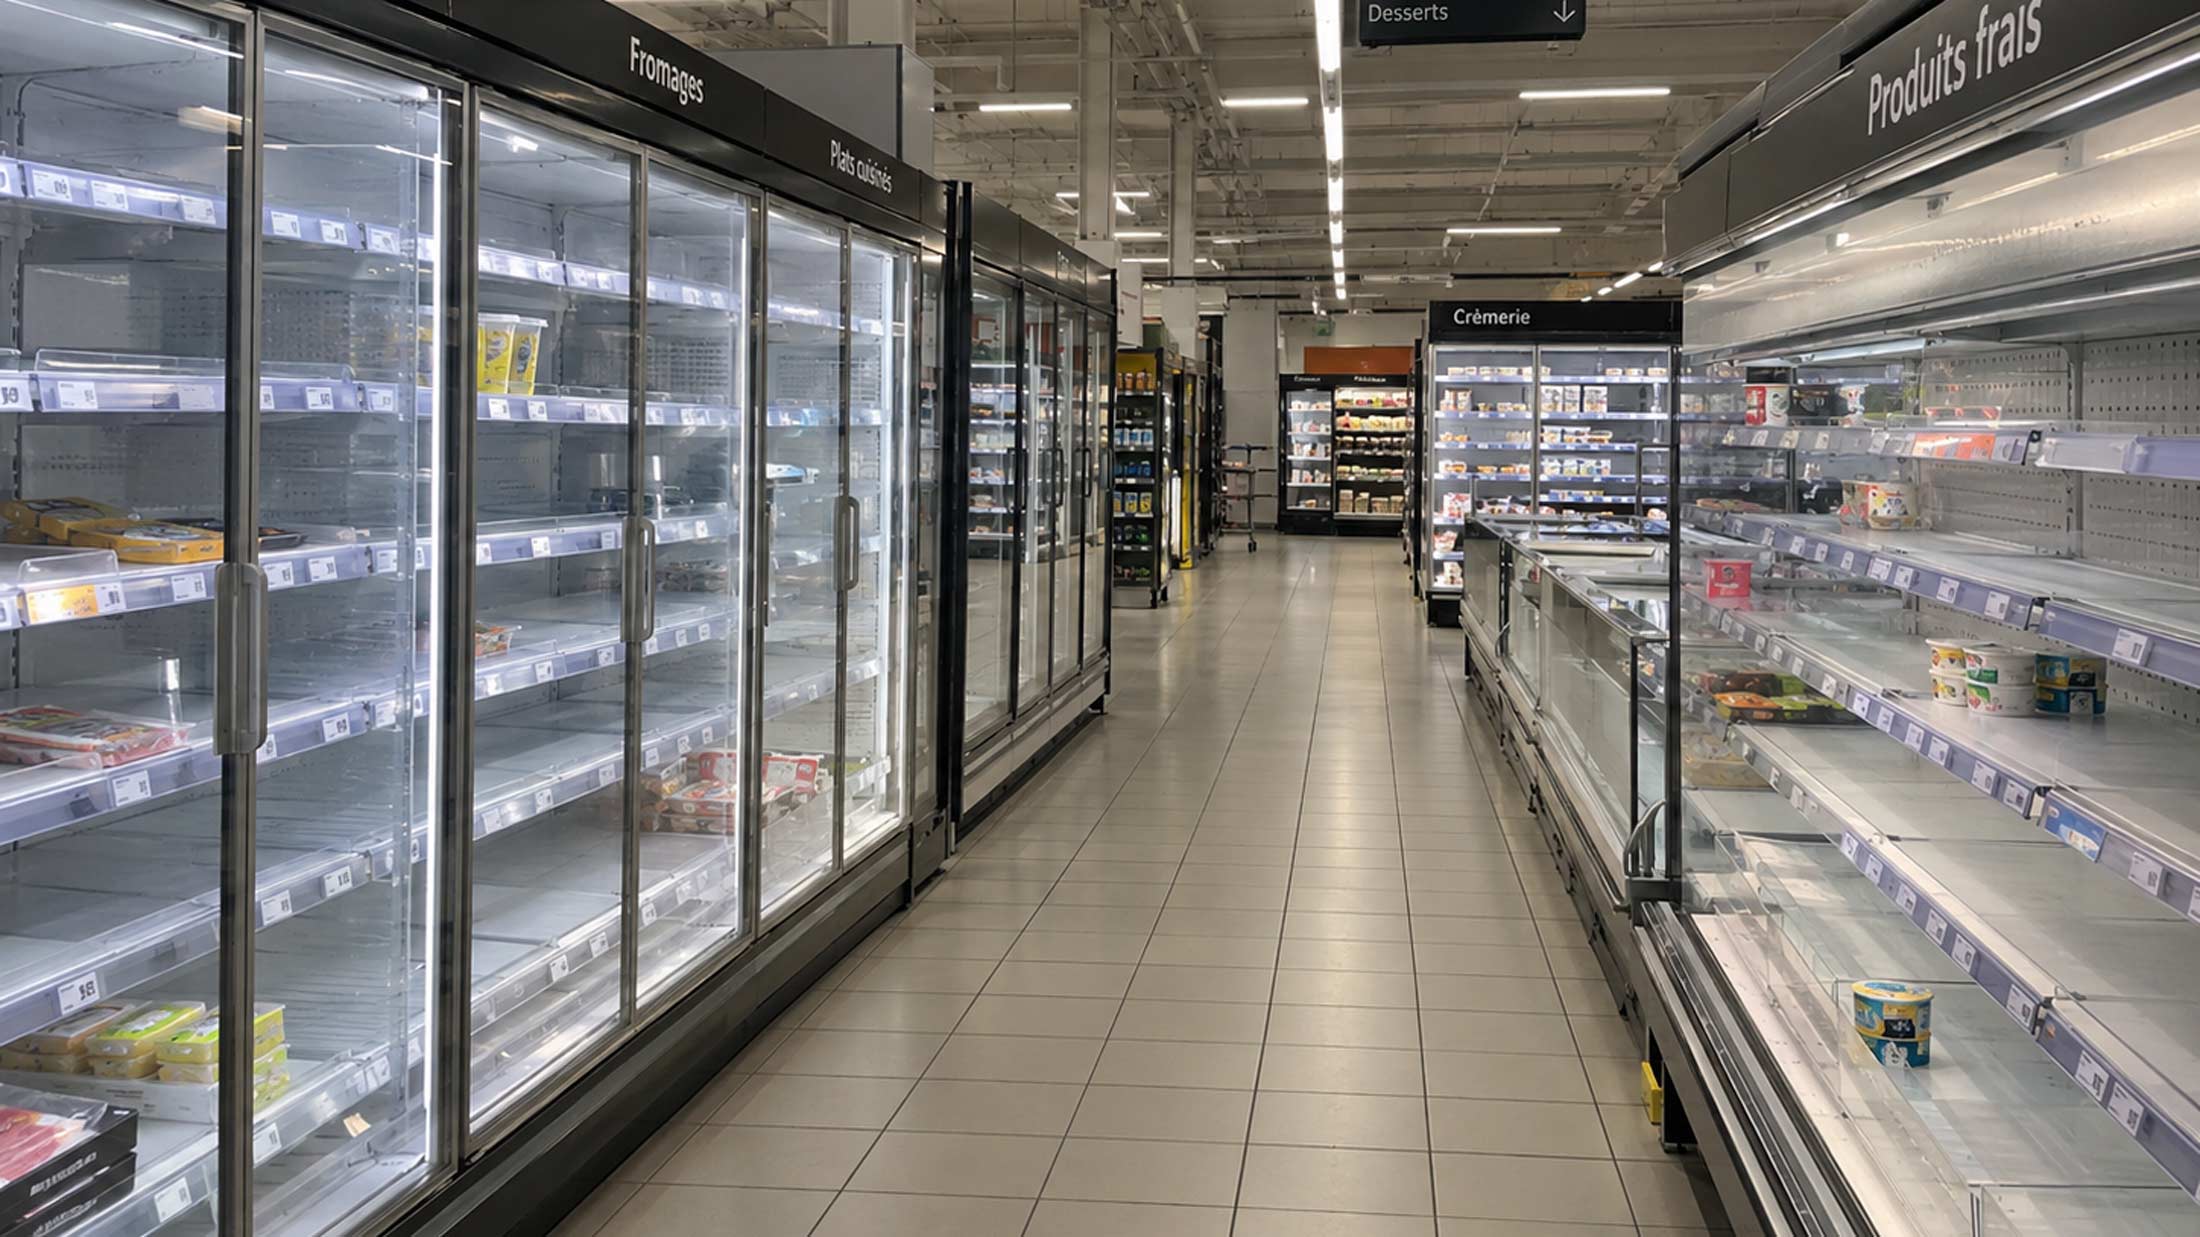
Cyberattack Spoils Food at Hundreds of French Supermarkets
Article Content

- •Hackers targeted refrigeration systems of major French supermarkets, causing massive food spoilage.
- •The attack exploited known vulnerabilities in outdated Danfoss software, with critical CVEs identified.
- •French authorities have opened an investigation into the unprecedented cyberattack.
On October 12, 2026, a cyberattack targeted the refrigeration systems of several major French supermarket chains, including Coopérative U and Intermarché. The attackers exploited outdated software from Danish provider Danfoss, remotely triggering defrost cycles that raised temperatures in refrigeration units to 50°C (122°F). This incident affected approximately 150 to 200 Intermarché stores and nearly 100 Coopérative U outlets, leading to significant food spoilage and estimated losses in the millions of euros. The attack is described as unprecedented, with French authorities opening an investigation. Vulnerabilities in Danfoss's software had been publicly documented prior to the attack, including CVE-2023-25915, which has a CVSS score of 9.9, indicating critical severity. The identity of the attackers remains unknown, and the affected companies are working to restore operations.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track Carrefour and CVE-2023-25915 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What vulnerabilities were exploited?
How many stores were affected?
What actions are being taken?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…