 Insurancejournal
Cyber Incident Disrupts LNG Tanker Carrying US Gas to Europe
Article Content

- •The Vivit Africa LNG tanker experienced a suspected cyber incident while en route to Italy.
- •This is the third suspected cyberattack on tankers in a month, raising concerns about maritime cybersecurity.
- •Investigations are ongoing, with authorities monitoring nearly 20 ships for similar threats.
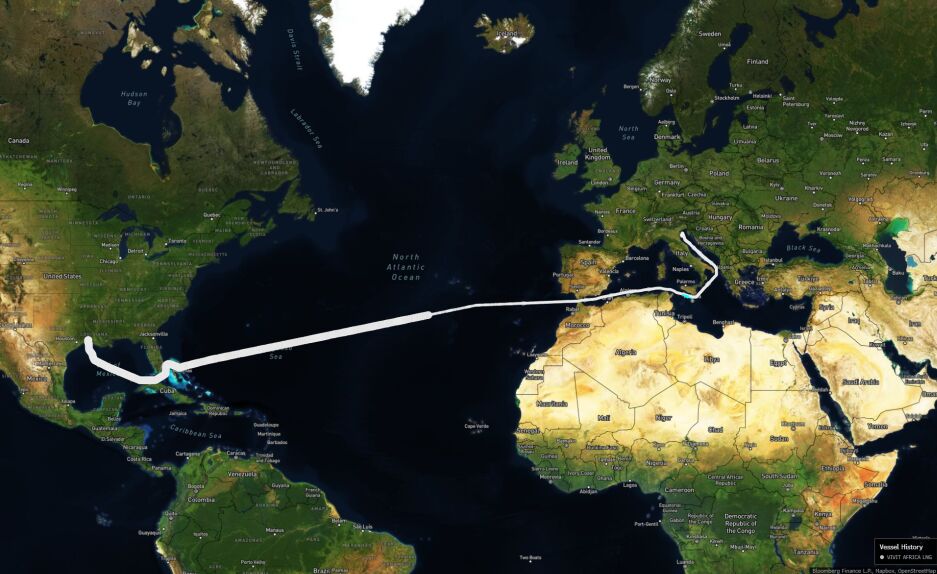
The LNG tanker Vivit Africa, transporting American liquefied natural gas to Italy, experienced a systems failure that the crew suspects may be a cyberattack. The incident occurred while the vessel was navigating the Mediterranean Sea in early September, causing it to halt its journey and head back towards Spain. The crew reported being unable to access internal control systems, prompting an investigation by the Korean Register, which advises the ship on technical matters. The vessel, owned by South Korea's H-Line Shipping and chartered by Vitol, has been idling off the Italian coast without discharging its cargo. This incident marks the third suspected cyber-related disruption to tankers in a month, following two similar incidents off the US coast in late August. Authorities are monitoring nearly 20 ships globally for potential cyber threats. The cause of the failure remains undetermined, and the investigation is ongoing.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Vitol Group in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical GitLab CVE-2026-85706 Exploited; Microsoft Issues Record 974 Patches A critical CVE-2026-85706 path-traversal vulnerability in GitLab (CVSS 10.0) was exploited in the wild just hours after its disclosure on September 12, 2026. Microsoft released its largest-ever patch batch, addressing 974 vulnerabilities, including several actively exploited Windows flaws. The GitLab flaw allows…