 Resiliencemedia.Co
Cyberattack Disrupts Supermarkets' Refrigeration Systems Across Europe
Article Content

- •Cyberattack on refrigeration systems affected supermarkets in at least nine European countries.
- •Temperatures in freezers were manipulated, leading to significant food spoilage.
- •The attacks highlight vulnerabilities in outdated, internet-connected refrigeration controllers.
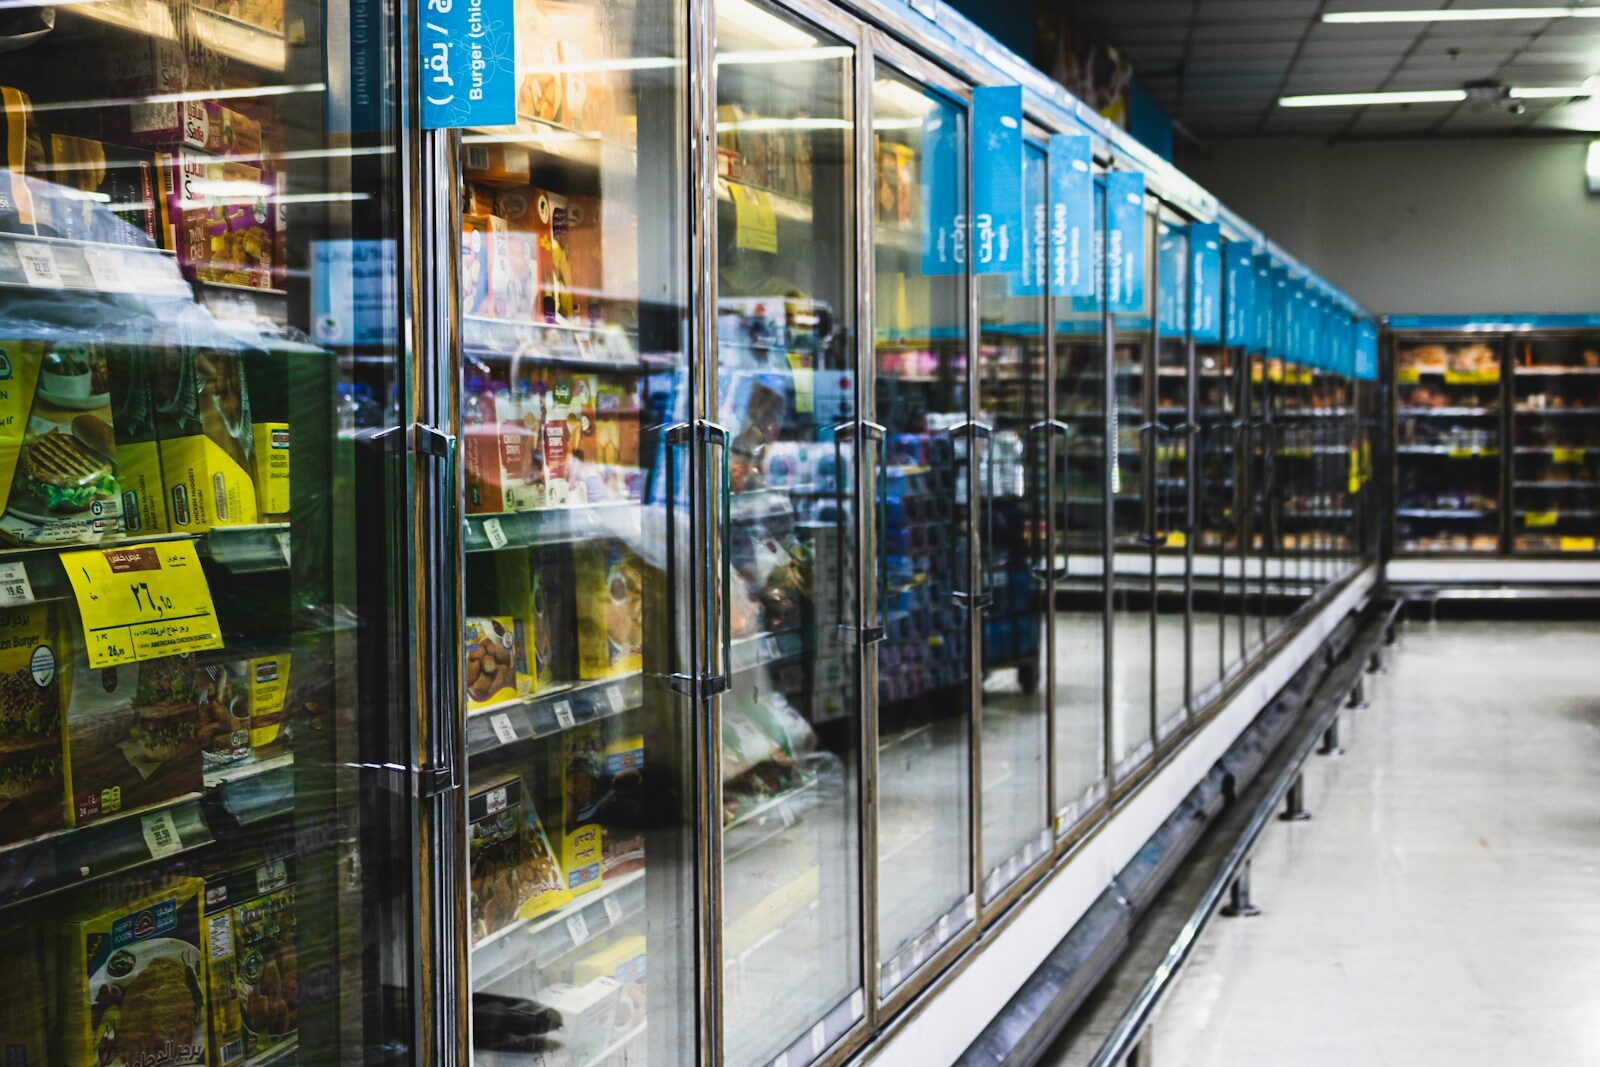
On November 3, 2026, a cyberattack targeted refrigeration systems in supermarkets across at least nine European countries, including Belgium, Sweden, and Ireland, causing significant food spoilage. The attack followed a similar incident in France three weeks prior, where around 700 supermarkets were affected. Retailers like Carrefour and Coop reported that temperatures in freezers were manipulated to as high as 50 degrees Celsius, leading to the disposal of perishable goods. The attack exploited vulnerabilities in internet-connected refrigeration controllers, which are often outdated and lack proper security measures. EU officials have deemed these incidents a deliberate attempt to disrupt the food supply chain. No group has claimed responsibility for the attacks, and investigations are ongoing. The situation has raised alarms about the security of critical infrastructure and the potential for further attacks on food supply chains and other civilian infrastructure.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Carrefour in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
Which countries were affected by the cyberattack?
What was the attack method?
Are there any known vulnerabilities exploited?
Continue Reading
 Volt Typhoon's Silent Train Network Targets US Critical Infrastructure The Chinese state-sponsored hacking group Volt Typhoon has been linked to a covert network called Silent Train, which has exploited at least four zero-day vulnerabilities over three years. This network utilizes rapidly rotating chains of compromised SOHO routers, IoT devices, and enterprise infrastructure to access…
 GitLab Issues Emergency Patch for Critical RCE Vulnerability GitLab has released emergency patches for a critical remote code execution vulnerability, CVE-2026-97229, affecting its Community and Enterprise Editions. This flaw, stemming from an integer overflow in the CI/CD regular expression compiler, allows unauthenticated attackers to execute arbitrary code via specially…