 Theregister
Cybercriminals Exploit Supply Chain Attacks in Self-Reinforcing Ecosystem
Article Content
Browse articles 
Cybercriminals are increasingly utilizing supply chain attacks, creating a self-reinforcing ecosystem of breaches, credential theft, and ransomware, according to a report by Group-IB. This interconnected approach allows attackers to compromise multiple vendors and service providers, impacting a wide range of businesses. Notable incidents include the Shai-Hulud NPM worm and the Salesloft breach.
Ask AI about this cluster
Answers cite the sources they use
Updated 213d ago How this analysis works
Timeline
Recent
Cybercriminals enhance methods for breaching vendors
Date unknown
Group-IB report released on supply chain attack trends
Date unknown
Shai-Hulud NPM worm incident
Date unknown
Salesloft breach incident
More articles in this cluster (16)
Following this threat?
Track Shai-hulud and Oracle in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
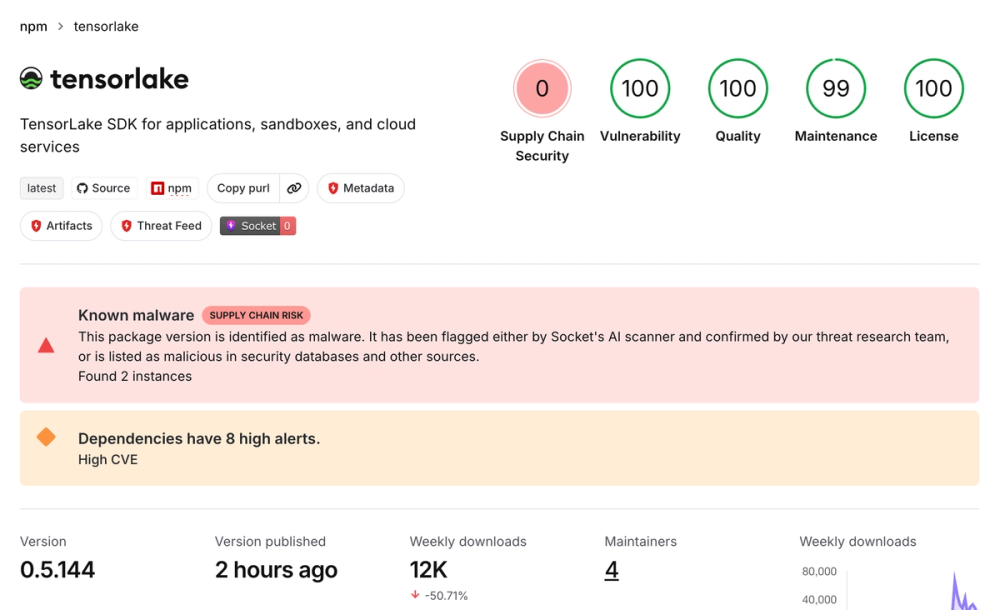 Tensorlake npm Package Compromised by Shai-Hulud Worm On October 8, 2026, the Tensorlake npm package version 0.5.144 was compromised, delivering a credential-stealing worm known as Shai-Hulud. The malware, which was published through a compromised maintainer account, executes a preinstall hook that runs an obfuscated loader to harvest credentials from local files and CI…
 Rise of Malicious npm Packages Threatens Developer Trust As of Q2 2026, Sonatype Research logged 1.8 million malicious packages, with npm accounting for 96.6% of this total. The quarter saw a surge in repository abuse, trojan-class malware, and maintainer compromises, indicating a shift towards targeting trusted developer workflows. ReversingLabs reported a specific…