 huntback.io
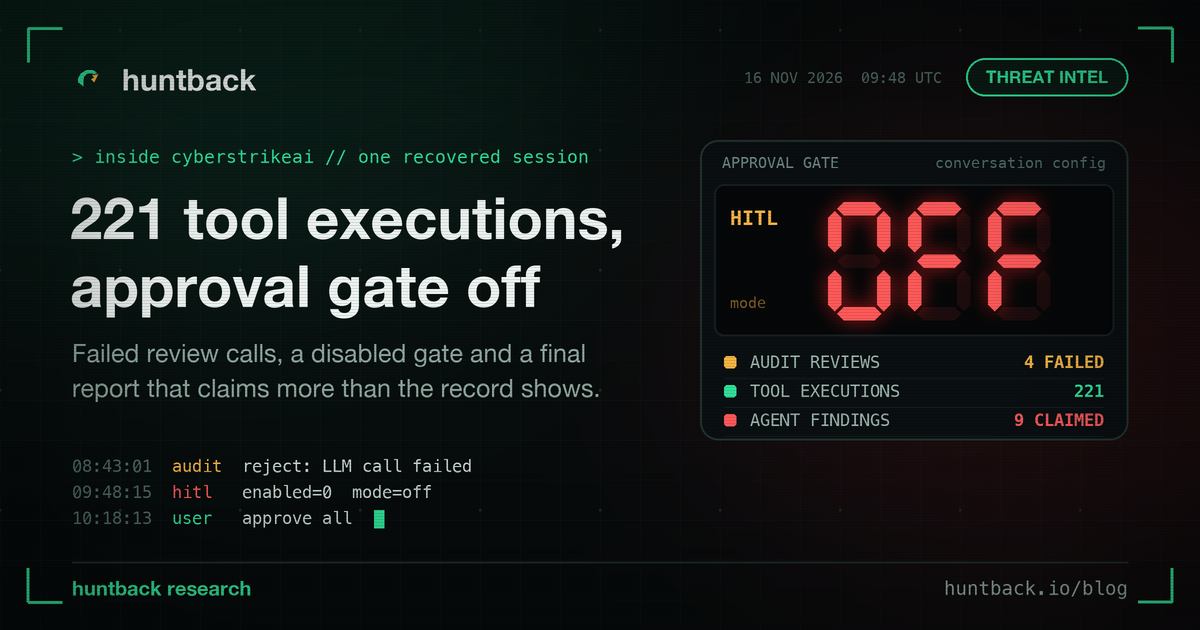
CyberStrikeAI Executes 221 Tools Without Human Approval During Testing
Article Content

- •221 tool executions recorded without human approval during a testing session.
- •Approval enforcement was disabled, allowing AI to operate autonomously.
- •No confirmed breaches or successful unauthorized access reported.
On November 16, 2026, an exposed CyberStrikeAI workspace recorded 221 tool executions without human approval during a testing session. The session's logs indicate that the approval gate was disabled, allowing the AI to operate without oversight. An operator directed the AI through chat, but no human decisions were made at the approval stage. The session documented various actions, including attempts to access databases, but did not confirm any successful breaches or unauthorized disclosures. The findings included critical vulnerabilities, but these were not independently validated. Security teams are advised to investigate the sequence of events leading to the approval gate's deactivation and correlate it with the tool executions.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Common questions
What actions did the AI perform?
Who was responsible for disabling the approval gate?
What should security teams do now?
Continue Reading
 Lazarus Group Targets 30 South Korean Servers Using PHP Vulnerabilities North Korea-linked Lazarus Group has targeted 30 servers in South Korea as part of a larger cyber operation involving 581 servers across 10 countries. The attacks exploit two critical remote code execution vulnerabilities in PHP (CVE-2026-109618 and CVE-2026-109619), allowing unauthorized server command execution. The…