 www.prnewswire.co.uk
Cyble Partners with UAE Cyber Security Council to Enhance Threat Intelligence
Article Content

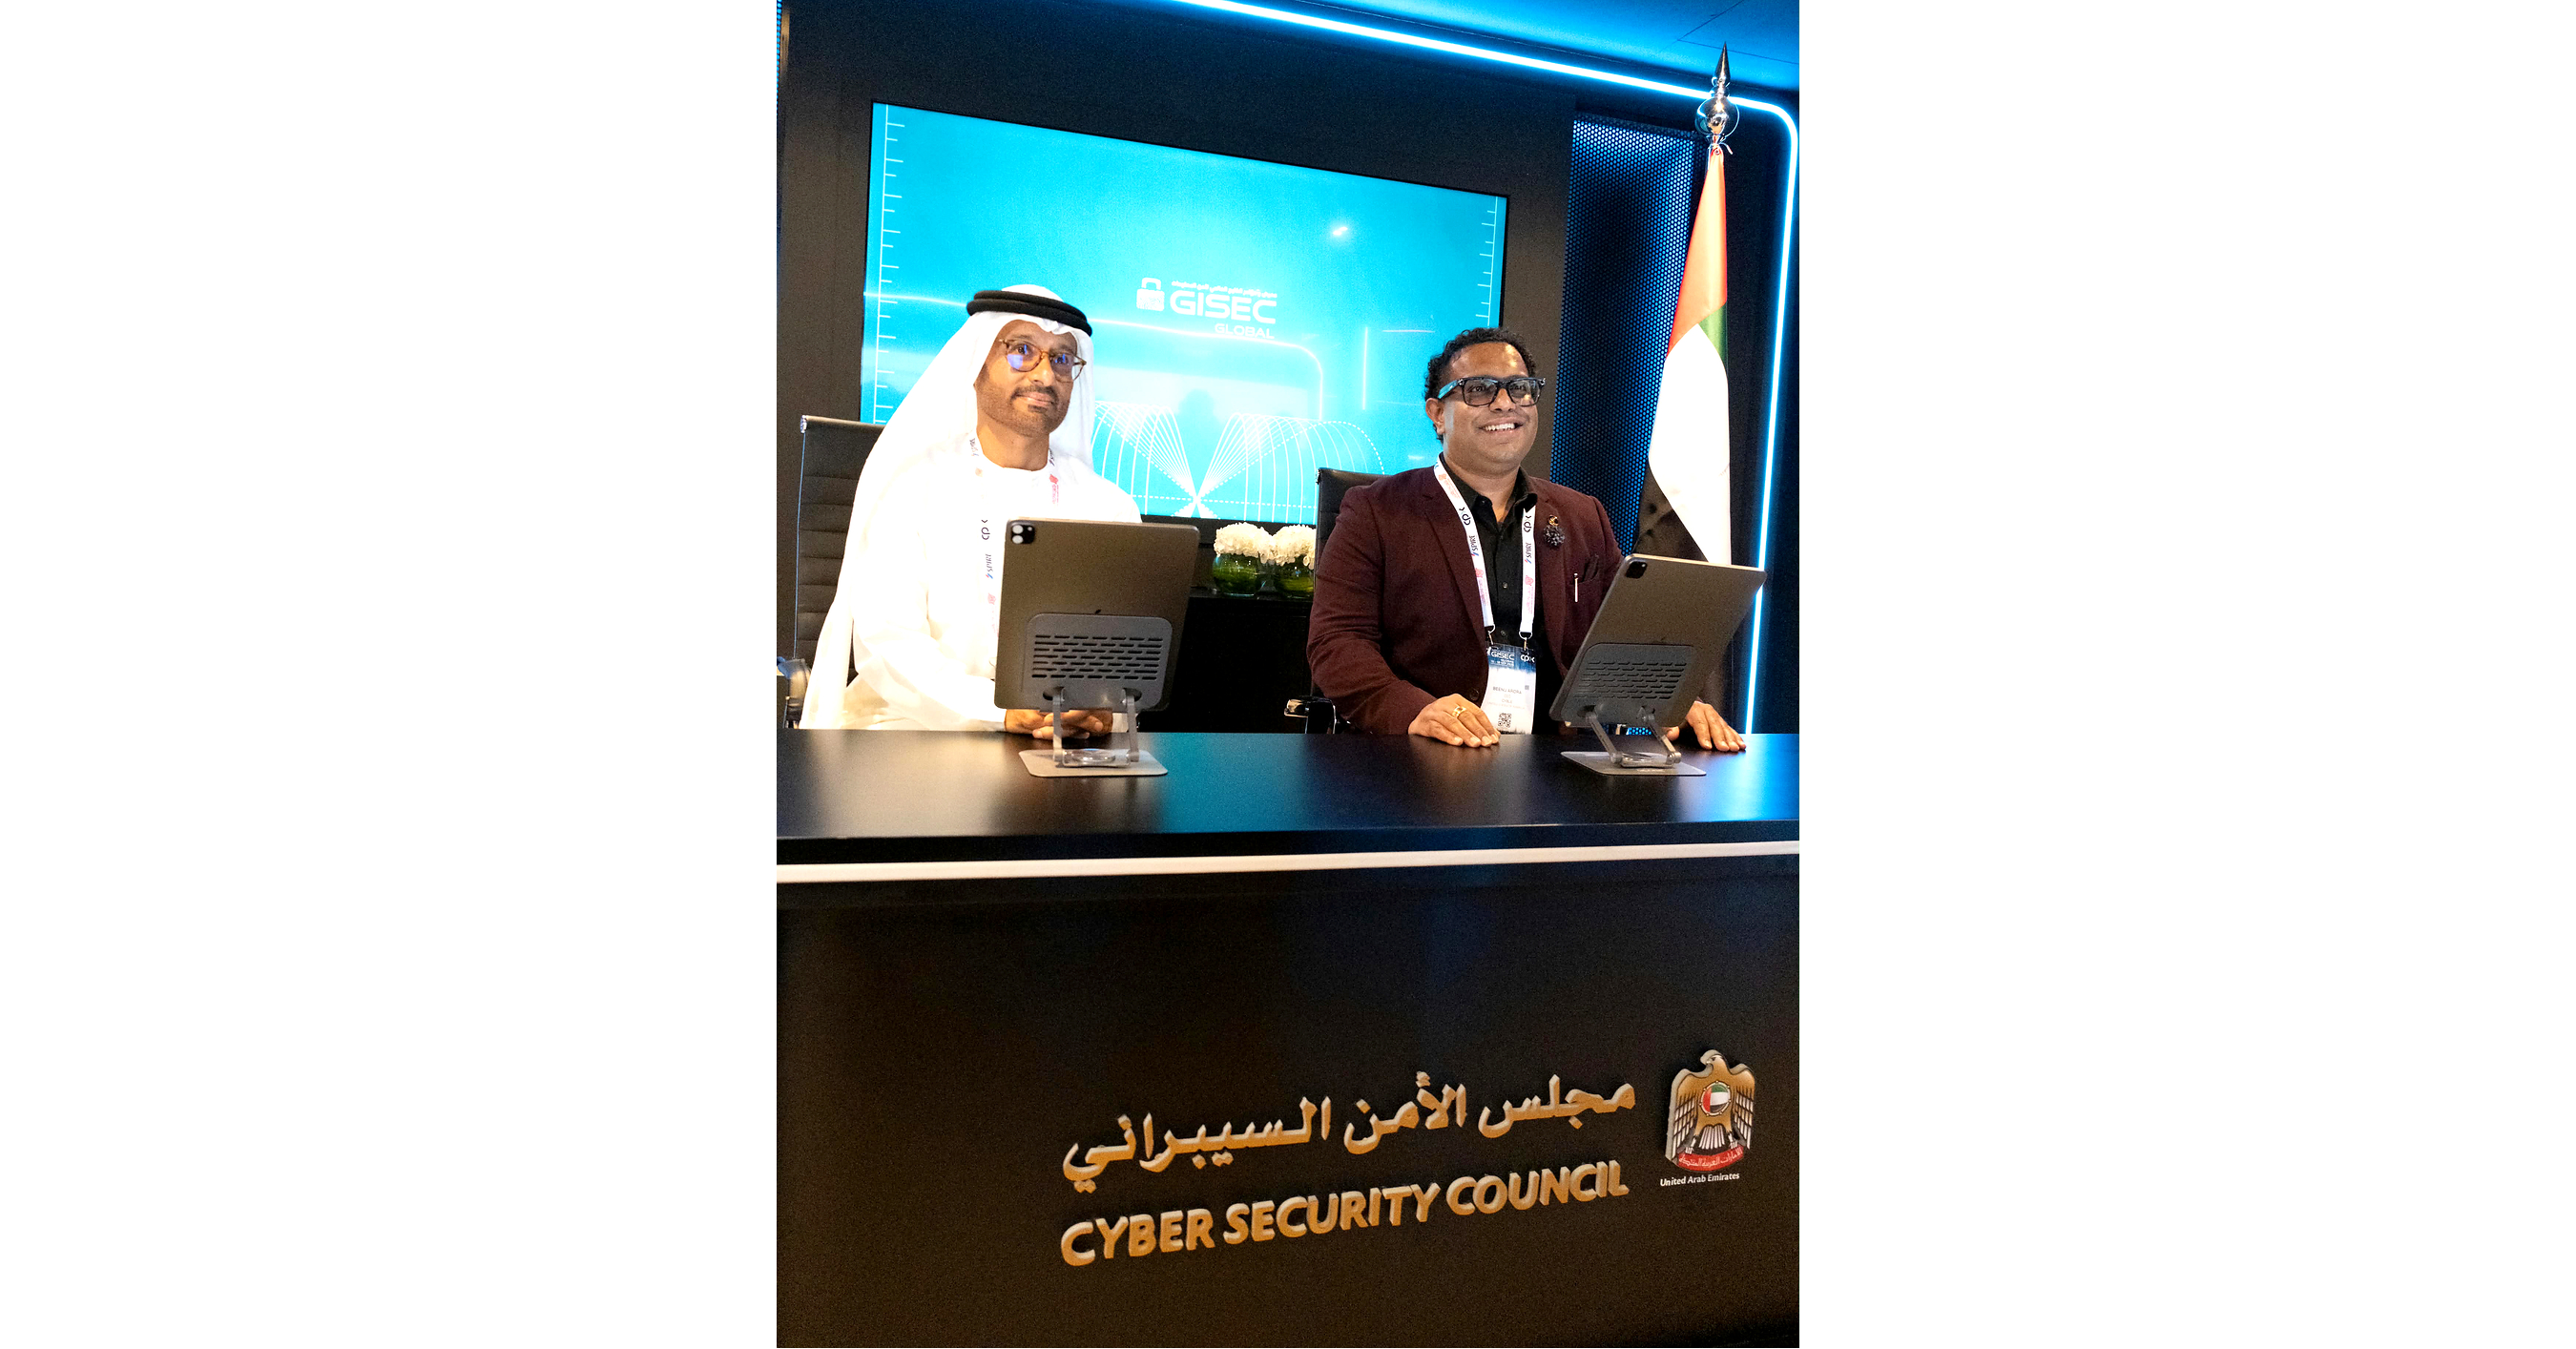
- •Cyble signed an MOU with the UAE Cyber Security Council on September 17, 2026.
- •The partnership focuses on enhancing threat intelligence and early warning capabilities.
- •Cyble's platform will aid in identifying emerging cyber risks for critical infrastructure.
On September 17, 2026, Cyble, an AI-native cybersecurity firm, signed a Memorandum of Understanding (MOU) with the Cyber Security Council of the UAE. This collaboration aims to bolster the UAE's national cybersecurity capabilities through advanced threat intelligence and early warning systems. The MOU will focus on protecting the UAE's digital infrastructure, particularly for government and critical infrastructure entities. Cyble's threat intelligence platform, Cyble Vision, will be instrumental in providing insights into emerging cyber risks. The partnership reflects the UAE's commitment to enhancing its cybersecurity posture and positions Cyble as a key player in the national cybersecurity ecosystem. The collaboration emphasizes proactive, intelligence-led defense strategies against sophisticated cyber threats. Cyble's CEO, Beenu Arora, highlighted the strategic validation of their capabilities at a national level. The Cyber Security Council's head, H.E. Dr. Mohamed Al Kuwaiti, reiterated the importance of partnerships with technology providers to strengthen cyber resilience.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Cyber Security Council Of The United Arab Emirates in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…
 Critical GitLab CVE-2026-85706 Exploited; Microsoft Issues Record 974 Patches A critical CVE-2026-85706 path-traversal vulnerability in GitLab (CVSS 10.0) was exploited in the wild just hours after its disclosure on September 12, 2026. Microsoft released its largest-ever patch batch, addressing 974 vulnerabilities, including several actively exploited Windows flaws. The GitLab flaw allows…