 kotaku.com
DDoS Attack Disrupts The Cutting Room Floor Wiki Following AI User Ban
Article Content

- •The Cutting Room Floor was targeted by a DDoS attack on August 27, 2026.
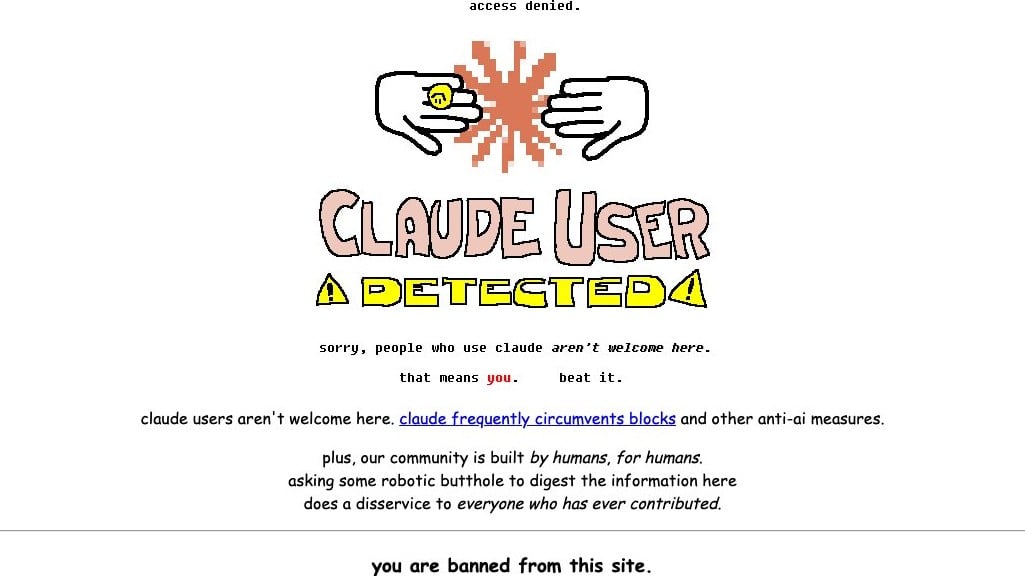
- •The attack was linked to a user banned for using AI tools, specifically Claude.
- •TCRF's anti-AI measures may have provoked the attack, leading to significant downtime.
On August 27, 2026, The Cutting Room Floor (TCRF) experienced a DDoS attack that rendered the site offline. The attack was reportedly triggered by a user banned for using an AI tool, Claude, who attempted to evade the ban and subsequently launched the attack. This DDoS attack aimed to saturate the server's network connection with overwhelming garbage traffic, forcing TCRF's hosting provider, Linode, to null-route the server's connection. The attack lasted approximately half an hour, significantly impacting the site's accessibility. TCRF has a strong anti-AI stance, which may have contributed to the incident. Currently, the site remains offline until the DDoS traffic subsides, with no specific timeline for restoration provided.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (4)
Following this threat?
Track anubis and The Cutting Room Floor in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical RCE Vulnerability in Confection WordPress Plugin (CVE-2026-115252) A critical vulnerability, CVE-2026-115252, has been identified in the Confection WordPress Cable plugin, affecting versions 0.4.0 to 0.4.7. This flaw allows unauthenticated attackers to execute arbitrary PHP code on the server by writing unmodified settings into a PHP file without proper checks. The vulnerability has…
 Critical RCE and LPE Vulnerabilities in Quest Foglight for Databases On November 3, 2026, the Zero Day Initiative disclosed multiple critical vulnerabilities in Quest Foglight for Databases, including six remote code execution (RCE) flaws and two local privilege escalation (LPE) vulnerabilities. The most severe RCE vulnerabilities, CVE-2026-92189 and CVE-2026-92190, allow…