 Theregister
Passenger Allegedly Jams Delta Flight Wi-Fi, Sets Up Rogue Network After DEF CON
Article Content

- •A passenger on Delta Flight 591 allegedly jammed the in-flight Wi-Fi and created a rogue network.
- •The incident involved a possible deauthentication attack aimed at phishing passengers' credentials.
- •Delta confirmed no aircraft systems were compromised, and safety was never in question.
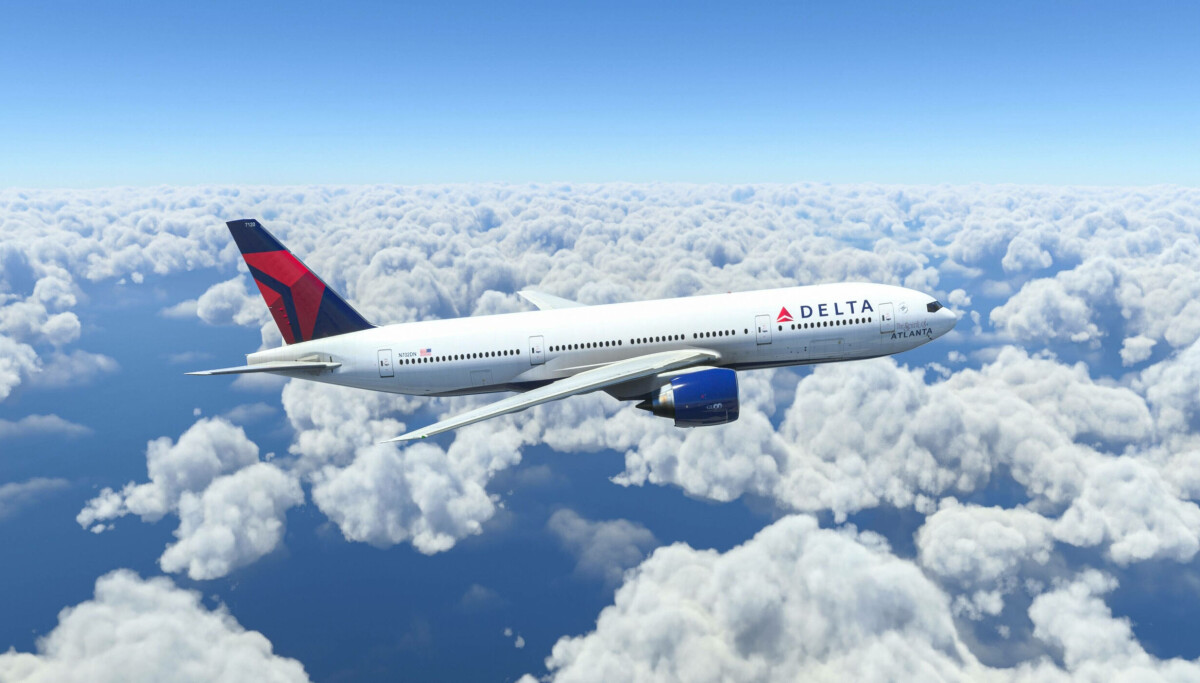
On August 10, 2026, a Delta Air Lines flight from Las Vegas to Atlanta experienced a cybersecurity incident where a passenger allegedly jammed the in-flight Wi-Fi and set up a rogue network named 'Delta WiFi Fast.' This unauthorized network aimed to phish for personal credentials from other passengers. Delta confirmed that the flight's safety was never compromised, and no aircraft systems were hacked. The cabin crew deactivated the Wi-Fi for approximately 30 minutes in response to the incident. Federal authorities were alerted and boarded the aircraft upon landing to investigate. The incident occurred shortly after the DEF CON 34 hacker conference, raising concerns about the potential use of deauthentication attacks, a method where attackers disconnect users from legitimate networks to redirect them to malicious ones. Delta is collaborating with federal law enforcement for a thorough investigation.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (13)
Following this threat?
Track Delta Air Lines in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…