 www.newcivilengineer.com
DfT Withholds Information on Cosco Shipping's UK Port Operations Amid Surveillance Allegations
Article Content

- •DfT refused to disclose Cosco Shipping's UK port facilities due to security concerns.
- •US officials allege Cosco aids Beijing in spying on military communications.
- •Increased scrutiny on foreign operators in critical infrastructure is anticipated.
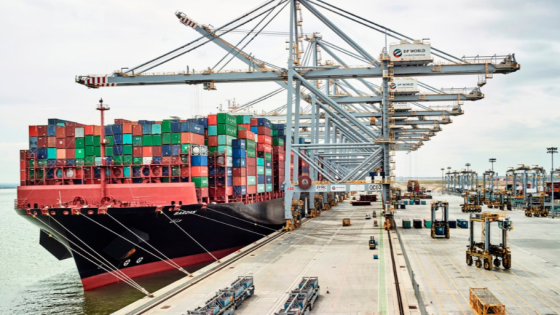
The UK Department for Transport (DfT) has declined to disclose information regarding the facilities operated by Chinese state-owned Cosco Shipping in the UK, following allegations from US officials that the company aids Beijing in monitoring US military communications. The DfT cited exemptions under the Freedom of Information Act, stating that releasing such information could harm UK interests. Cosco Shipping is known to have a presence at UK ports, including Felixstowe, and operates various logistics facilities. The refusal to disclose details raises concerns about the potential risks associated with foreign control of critical infrastructure. Security assessments for port upgrades and foreign operator vetting are expected to be intensified as a result. The situation reflects a broader trend of increasing scrutiny on foreign involvement in UK transport infrastructure.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
What information did the DfT withhold?
What are the implications of this decision?
How does this relate to US allegations?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…