 Discoveryalert.Au
Drone Attack on Kuwait's Shuwaikh Oil Complex Highlights Energy Security Risks
Article Content

- •A drone attack on Kuwait's Shuwaikh oil complex occurred on April 6, 2026.
- •The attack highlights vulnerabilities in energy infrastructure security against drone threats.
- •Market volatility is expected due to the psychological impact of the attack on petroleum prices.
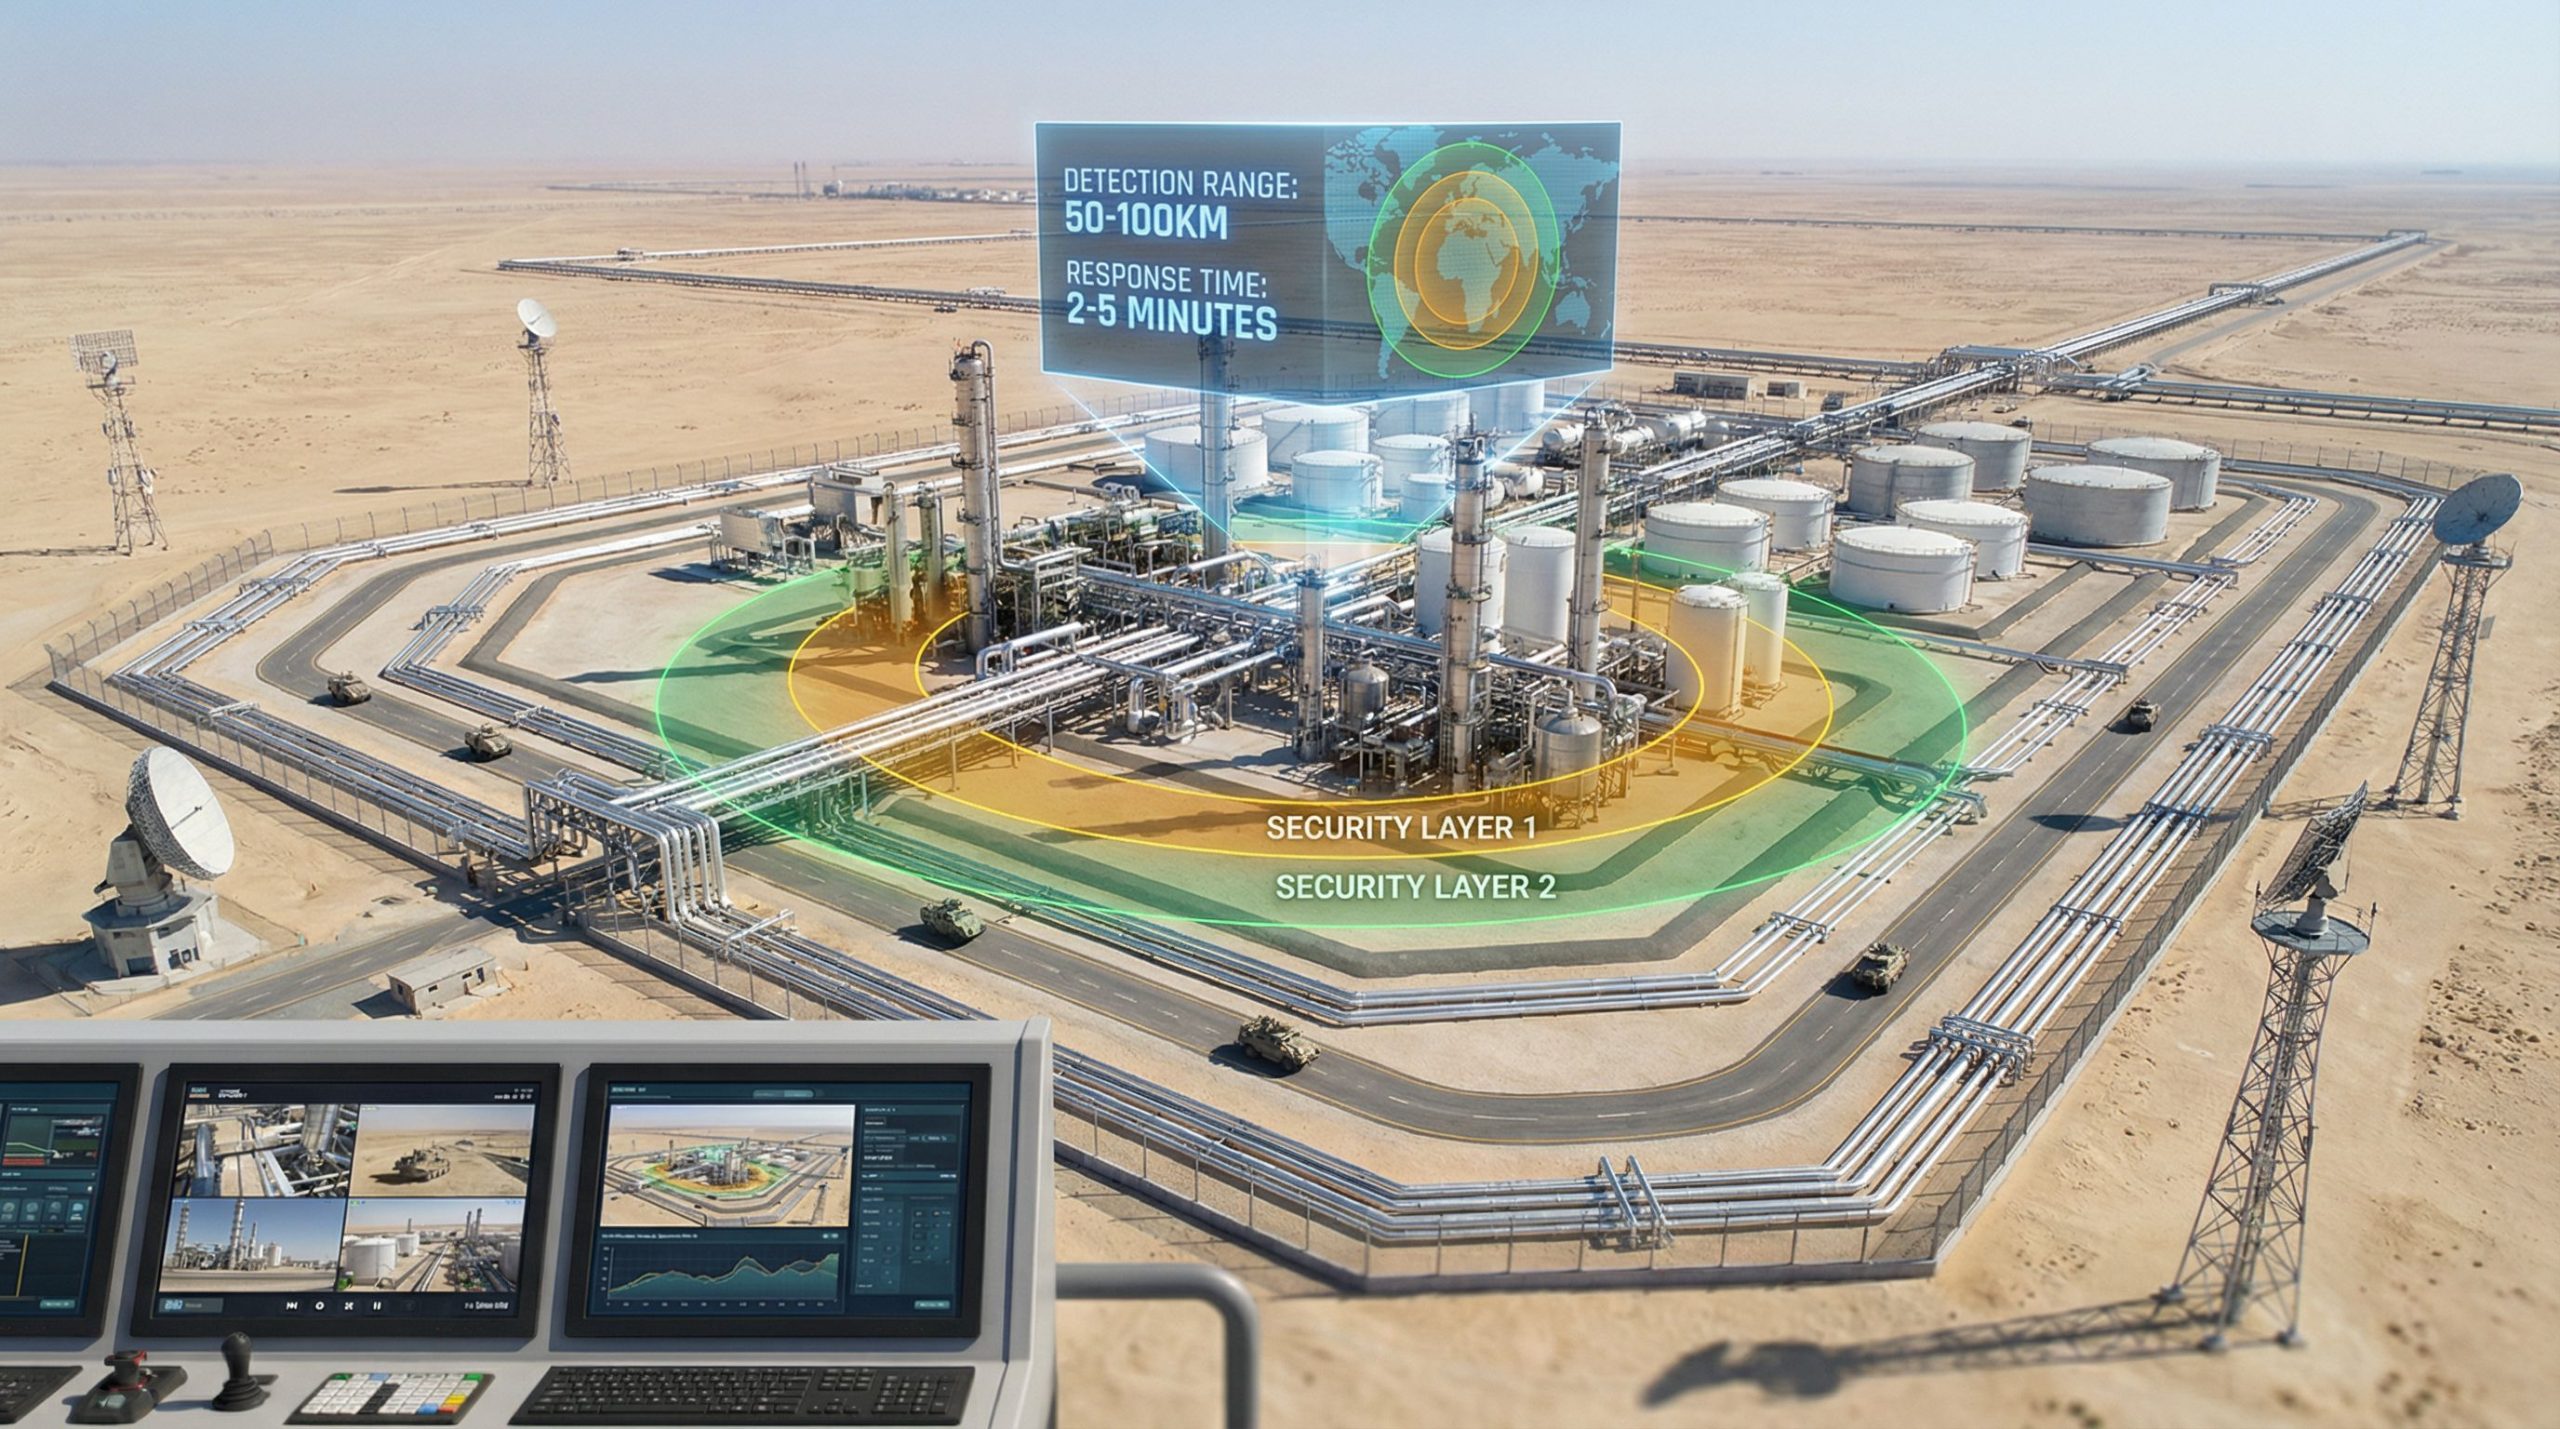
On April 6, 2026, a drone attack struck the Shuwaikh oil sector complex in Kuwait, causing a fire and highlighting vulnerabilities in energy infrastructure security. The attack utilized unmanned aerial systems, which have become a significant threat to critical facilities designed for petroleum processing and distribution. This incident underscores the challenges faced by traditional security measures against low-cost drone technologies that can penetrate established defenses. The interconnected nature of petroleum processing facilities means that disruptions can have cascading effects, potentially impacting supply chains across the region. The psychological impact of such attacks often leads to significant market volatility, with price speculation and hedging behaviors observed following the incident. The attack exemplifies the urgent need for comprehensive security overhauls in the Gulf region's energy sector. Current assessments indicate that the incident has raised concerns over the resilience of energy infrastructure against similar future threats.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Saudi Aramco in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…