 Ukrinform
Drone Attack Targets Major Russian Titanium Production Facility
Article Content

- •Drones attacked AVISMA plant, a major titanium supplier for Russian military.
- •Five employees were injured, with three hospitalized due to the drone strike.
- •The attack is part of ongoing Ukrainian operations targeting Russian defense infrastructure.
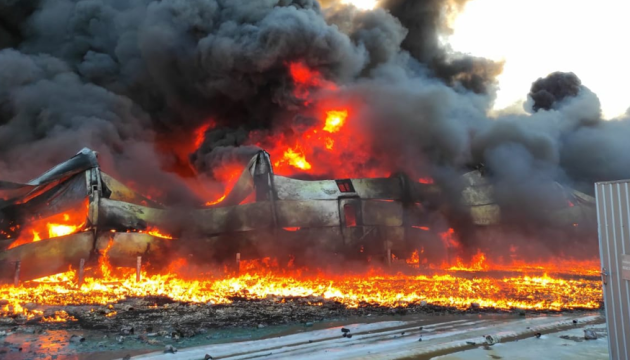
On October 25, 2026, drones struck the AVISMA chemical and metallurgical plant in Berezniki, Russia, a key supplier of titanium for military aircraft and missile systems. The attack resulted in minor damage to the facility, with five employees injured, three requiring hospitalization. Perm region Governor Dmitry Makhonin confirmed the incident, noting that Russian air defenses intercepted 11 drones. The plant, part of VSMPO-AVISMA, produces titanium sponge for the production of various military aircraft, including Su-34 and Su-35 fighter jets. This strike follows previous Ukrainian attacks on Russian defense facilities on October 24, targeting locations linked to missile production. The facility continues to operate despite the attack, according to local authorities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (6)
Following this threat?
Track Avisma in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What is the current status of the AVISMA plant?
How many employees were injured in the attack?
What is the significance of the AVISMA plant?
Continue Reading
 .NET Vulnerability CVE-2026-111497 Requires Immediate Action On October 25, 2026, Microsoft released out-of-band security updates for.NET addressing CVE-2026-111497, a vulnerability in the Brotli decompression algorithm that allows unauthorized attackers to elevate privileges over a network. The flaw affects.NET versions 8, 9, 10, and 11, particularly in applications that…
 Critical BeyondTrust 9.3 Vulnerability Actively Exploited by Threat Actor A critical vulnerability (CVE-2026-102764) in BeyondTrust Remote Support has been discovered and is actively being exploited by the threat group ARMORY CASTLE, reportedly linked to China. The vulnerability, which has a CVSS score of 9.3, allows unauthenticated attackers to upload files and potentially compromise host…