 Ifj
Drone Attacks Pose Severe Threat to Journalists in Ukraine
Article Content

- •Drone attacks have become a major threat to journalists in Ukraine, with 28 incidents reported in 2026.
- •At least five media workers were injured, and three journalists were killed in 2025 due to drone strikes.
- •Existing safety protocols and protective technologies are inadequate to address the evolving drone threat.
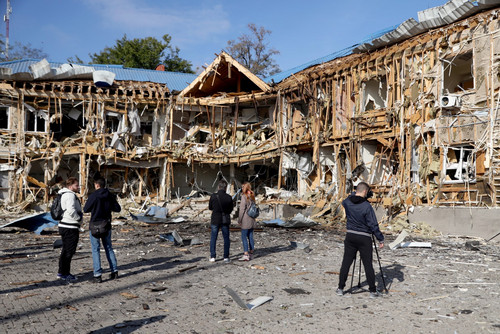
In 2026, drone attacks have emerged as a significant threat to journalists in Ukraine, with the National Union of Journalists of Ukraine (NUJU) documenting 28 verified incidents from January to August. At least five media workers were physically injured, and there were fatalities in 2025, including three journalists killed in separate drone attacks. Recent incidents include a drone attack on a vehicle used by journalists in Sloviansk on 24 September, which destroyed their equipment. The evolving threat includes FPV drones attacking journalists far from the front lines, and existing protective technologies are inadequate. NUJU's report emphasizes the need for improved safety protocols and international support for journalist protection. The report also notes that traditional PRESS markings are no longer effective in all situations, as evidenced by attacks on marked journalists. The situation continues to evolve, with ongoing risks to media infrastructure and personnel.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Common questions
How many journalists have been affected?
What types of drones are being used in attacks?
What can be done to improve journalist safety?
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Sets Oct. 11 Deadline for Patching Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog after they were exploited by the China-linked group Flax Typhoon. Federal agencies must patch or retire the affected software by October 11, 2026. The vulnerabilities…