 Euronews
Drone Strike Sinks Turkish Cargo Ship in Black Sea, Two Dead
Article Content

- •A drone strike sank the Turkish cargo ship Royad Mammadov, killing two sailors.
- •Ukrainian President Zelenskyy blamed Russia for the attack, citing it as an act of terror.
- •Eleven crew members were rescued, while one remains missing; ongoing rescue operations are in progress.
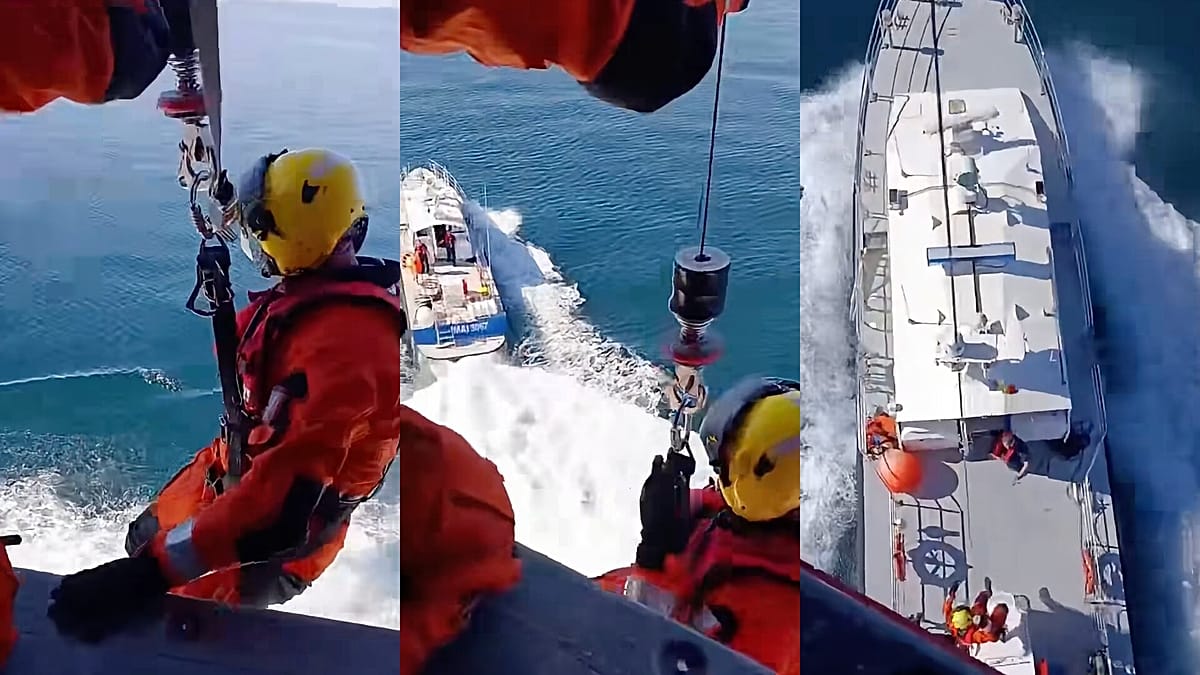
A drone strike reportedly sank the Turkish cargo ship Royad Mammadov in the Black Sea, resulting in two fatalities and injuries to several crew members. The ship, carrying grain from Ukraine to Italy, was attacked shortly after departing from the port of Izmail. Ukrainian President Volodymyr Zelenskyy attributed the attack to Russian drones, condemning it as an act of terror against civilian vessels. Eleven crew members were rescued, while one remains missing. The incident occurred approximately nine nautical miles from Romania's Pescăruș offshore platform. Romanian authorities have not yet named a suspect but are conducting ongoing rescue operations. The attack adds to a series of drone incursions in the region, raising tensions among NATO member states. Zelenskyy called for international pressure to ensure maritime security and restore global food supply chains.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track MG Shipping 5 in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What was the cargo of the ship?
How many crew members were on board?
What actions are being taken by authorities?
Continue Reading
 Critical Citrix NetScaler Zero-Day Vulnerabilities Exploited Citrix disclosed two critical zero-day vulnerabilities, CVE-2026-88771 and CVE-2026-88772, affecting NetScaler ADC and Gateway systems, which are being actively exploited. Both vulnerabilities have a CVSS score of 9.5 and allow unauthenticated attackers to execute arbitrary commands remotely. CVE-2026-88771 arises…
 Critical Authentication Bypass in Cisco Catalyst SD-WAN Manager Exploited On September 30, 2026, Cisco disclosed a critical vulnerability (CVE-2026-76504) in the Catalyst SD-WAN Manager that allows unauthenticated remote attackers to bypass authentication and gain admin-level access to the system. This flaw stems from improper handling of URI encoding in HTTP requests, enabling attackers to…