 Kyivpost
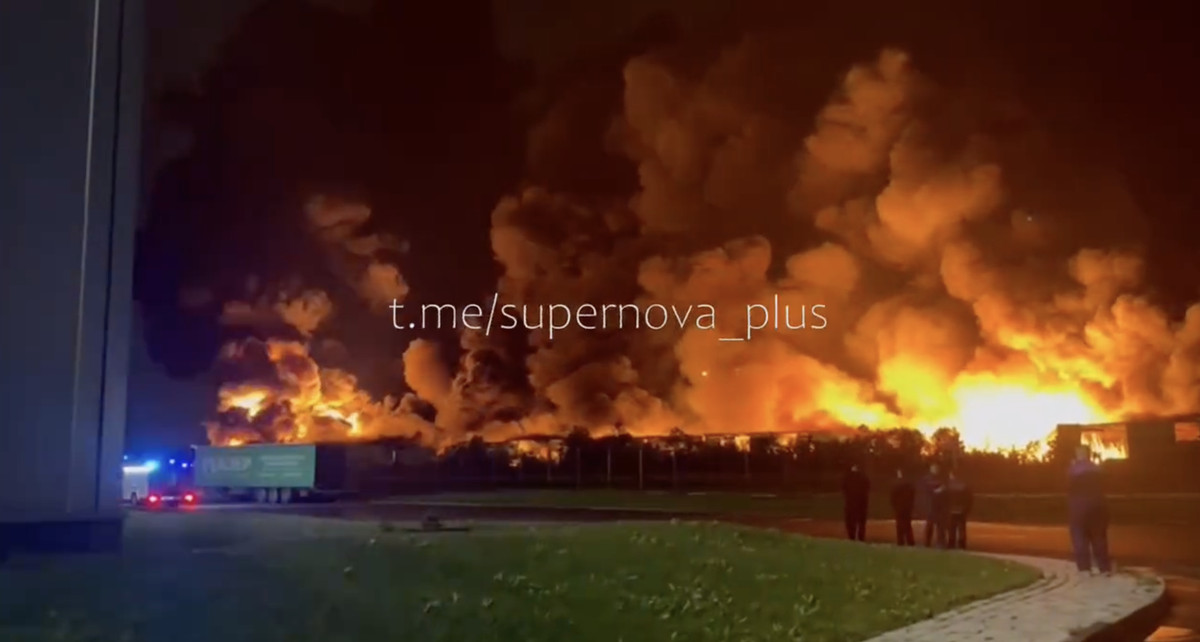
Drone Strikes Ignite Major Fires at Russian Logistics and Industrial Sites
Article Content

- •Drone strikes on Ozon facilities in Orenburg and St. Petersburg caused extensive fires.
- •Over 300 employees were evacuated from the Ozon logistics center in Orenburg.
- •The attacks are part of a sustained campaign against Russian logistics infrastructure.
On August 22 and 23, drone strikes targeted multiple Russian logistics and industrial facilities, causing significant fires. In Orenburg, a drone attack on an Ozon fulfillment center led to the evacuation of over 300 employees. Concurrently, a fire engulfed the Izhora industrial site in St. Petersburg, affecting a Logistera warehouse. The strikes are part of a broader campaign against Russian logistics infrastructure, with previous attacks reported on the Novokuybyshevsk oil refinery and other Ozon facilities. The Orenburg site, opened in 2024, was a major investment for Ozon, while the St. Petersburg site is crucial for heavy industry. The Russian Ministry of Emergency Situations managed to extinguish the fires, but the impact on logistics operations is substantial, with Ozon suspending deliveries and canceling orders. The coordinated nature of these attacks indicates a strategic targeting of logistics capabilities.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Novokuybyshevsk Oil Refinery in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 CVE-2015-3306 Exploited in ProFTPD FTP Servers CVE-2015-3306, a vulnerability in ProFTPD 1.3.5, allows remote attackers to read and write arbitrary files using the SITE CPFR and SITE CPTO commands. This exploit can lead to unauthorized access and potential remote code execution, as the commands are executed with the privileges of the ProFTPD service. Active…
 CISA Mandates Urgent Patching of Five Critical Flaws Exploited by Flax Typhoon The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has ordered federal agencies to patch five critical vulnerabilities by October 11, 2026, following exploitation by the China-linked hacking group Flax Typhoon. The vulnerabilities, added to CISA's Known Exploited Vulnerabilities (KEV) catalog, include…