 Malwarebytes
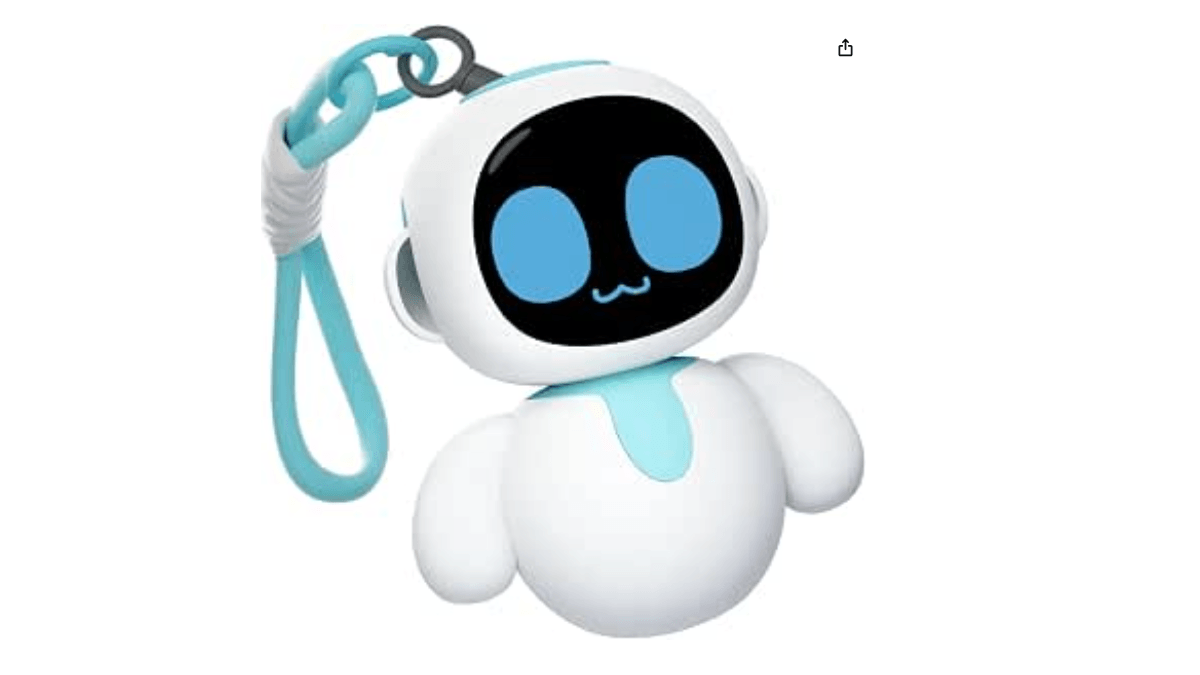
Eiliko Robot Exposes Millions of Private Conversations to Hackers
Article Content

- •Eiliko robot exposes 13 million conversations to unauthorized access.
- •Sensitive user data, including emotional profiles, is stored insecurely.
- •Remote manipulation of the robot's behavior is possible.
The Eiliko robot toy, manufactured by Energize Lab, has been found to have severe security vulnerabilities that expose private conversations and allow remote manipulation of the device. Researcher Sammy Azdoufal accessed 13 million conversations and the entire fleet of 68,000 robots, primarily used by children in the U.S. The service collects sensitive user data, including names, ages, and emotional profiles, which could be exploited by scammers. Despite attempts to contact Energize Lab, the company has not provided substantial responses regarding the security flaws. Users are advised to disconnect their devices from Wi-Fi until the issues are resolved.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (2)
Following this threat?
Track Energize Lab in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Common questions
What data is exposed?
Can the robot be manipulated remotely?
What should users do now?
Continue Reading
 Critical Zero-Day Exploited in BeyondTrust Remote Support by China-linked Group A critical vulnerability in BeyondTrust Remote Support, tracked as CVE-2026-102764 with a CVSS score of 9.3, has been exploited by the China-linked espionage group Armory Castle since August 29, 2026. This flaw allows unauthenticated remote attackers to perform file operations, gaining root control and access to…
 CISA Warns of Exploited Vulnerabilities in ProFTPD, ONLYOFFICE, Strapi, and More The U.S. Cybersecurity and Infrastructure Security Agency (CISA) added five vulnerabilities to its Known Exploited Vulnerabilities (KEV) catalog, including critical flaws in ProFTPD, ONLYOFFICE Docs, Strapi, Apache Struts, and ISC BIND. These vulnerabilities are being by Chinese actors for cyber espionage, targeting…