 Zimperium
Emerging Threat of MFA Fatigue Attacks on Mobile Users
Article Content
Browse articles 
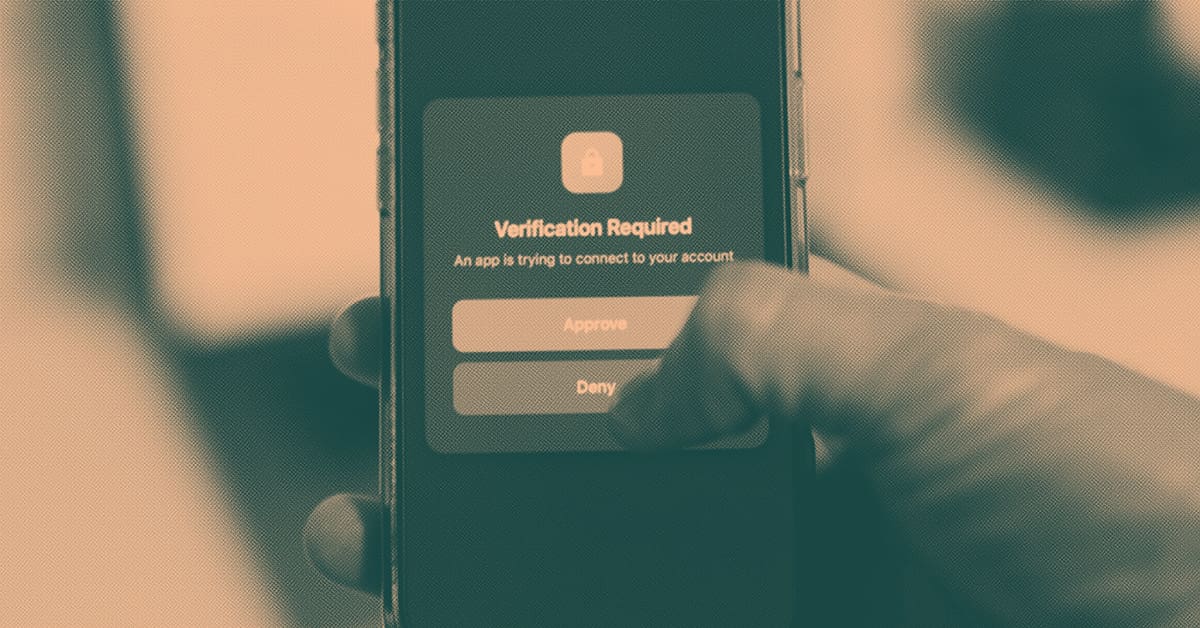
Security researchers have identified multi-factor authentication (MFA) fatigue attacks as a significant risk for mobile users. These attacks exploit repeated push-based MFA prompts, allowing attackers to gain unauthorized access through social engineering tactics. The focus is on the vulnerabilities associated with mobile authentication methods.
Ask AI about this cluster
Answers cite the sources they use
Updated 194d ago How this analysis works
Timeline
2026-03-02
Articles published detailing the risks of MFA fatigue attacks
Recent
MFA fatigue attacks reported as a growing threat
More articles in this cluster (3)
Following this threat?
Track Scattered Spider and Cisco in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Iranian State Actors Deploy CHOSEN BRICK Spyware Against Dissidents On September 15, 2026, the UK, US, and Netherlands issued a joint advisory regarding a spyware campaign attributed to Iranian state actors targeting dissidents, activists, and journalists. The malware, known as CHOSEN BRICK, is delivered through spear-phishing attacks on messaging platforms like WhatsApp and Telegram.…
 PAYLOAD Ransomware Exploits Active Directory GPO for Disruption In April 2026, Kaspersky's Global Emergency Response Team (GERT) responded to a ransomware incident at a manufacturing organization in the Middle East. Attackers gained domain-admin-equivalent control via a compromised FortiGate SSL VPN account and created a malicious Group Policy Object (GPO) named PAYLOAD. This GPO…