 www.kibrispostasi.com
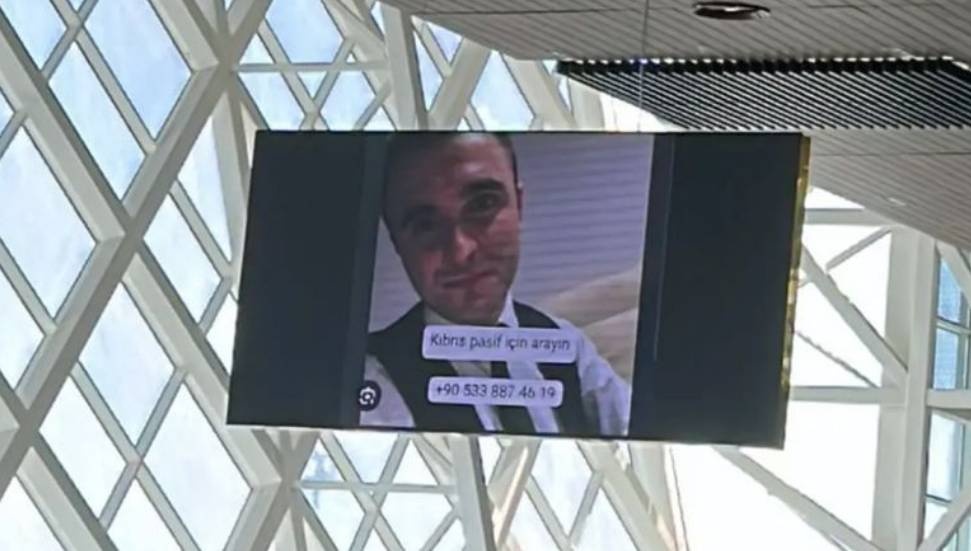
Ercan Airport Digital Screens Hacked, Displaying Offensive Content
Article Content

- •Ercan Airport's digital screens were hacked, displaying offensive messages.
- •The incident caused distress among passengers, prompting an apology from airport management.
- •This is the second cyber incident at Ercan Airport within a few months.
Digital advertising screens at Ercan Airport in Northern Cyprus were hacked, displaying an image of an unknown person alongside a message urging to 'call for passive Cyprus.' The incident occurred in the departure lounge, causing distress among passengers due to the offensive nature of the content. T&T Airport Management, which operates the airport, has apologized and stated that an investigation is underway. The contractor responsible for the screens has been warned, and measures are being taken to prevent future incidents. This is not the first cyber incident at Ercan Airport, as malware was reported to have deleted data from its main server in June 2026. The authorities have not yet released an official statement regarding this latest hacking event.
Ask AI about this cluster
Answers cite the sources they use
Timeline
More articles in this cluster (3)
Following this threat?
Track Ercan Havalimanı in your own feed — you're alerted when they show up in new reporting, leak sites or exploitation.
Free account · no card needed
Continue Reading
 Critical Cisco FMC Vulnerabilities Under Active Exploitation Cisco's Secure Firewall Management Center (FMC) Software has two critical vulnerabilities, CVE-2026-20079 and CVE-2026-20316, that are currently being exploited by state-sponsored and ransomware actors. CVE-2026-20079, rated 10.0 on the CVSS scale, allows unauthenticated remote attackers to bypass authentication and… Critical Zero-Day Vulnerability in Cisco Secure Email Gateway Exploited On September 14, 2026, Cisco disclosed a critical SQL injection vulnerability (CVE-2026-76461) in its Secure Email Gateway, allowing unauthenticated remote attackers to execute arbitrary commands with root privileges. This vulnerability arises from insufficient validation in the email parsing logic. Cisco confirmed…